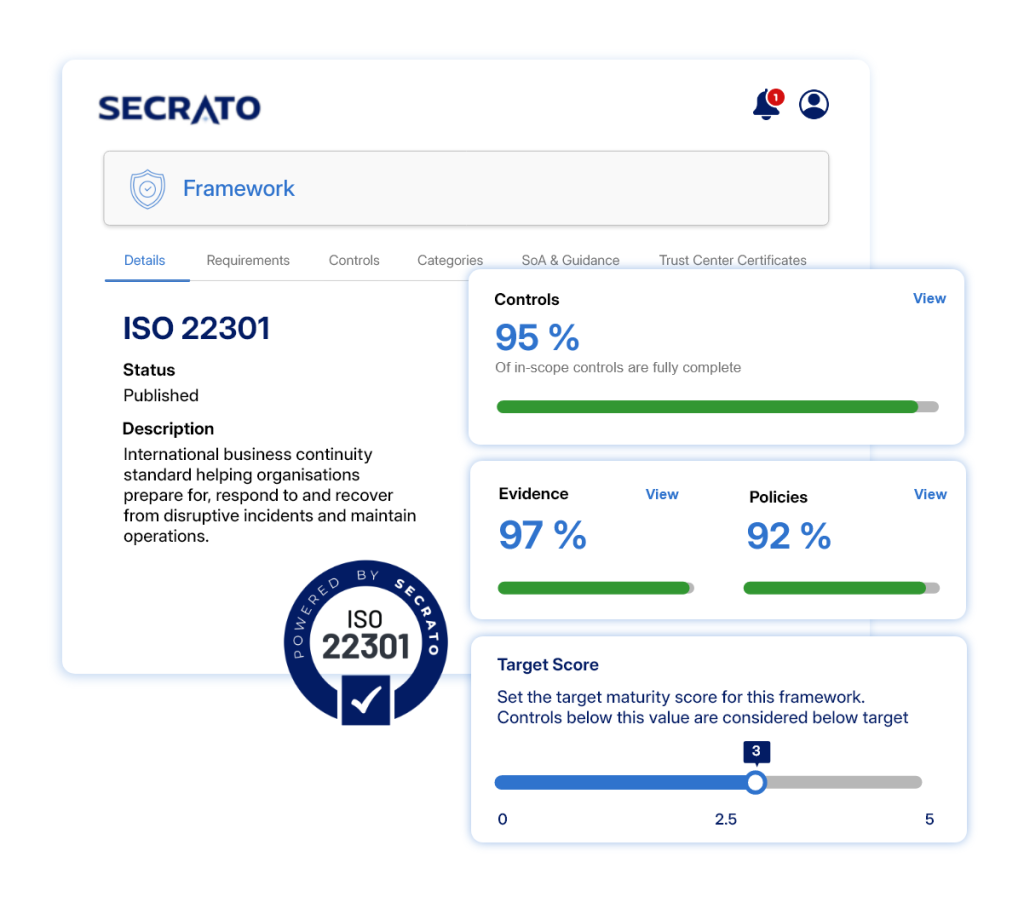
ISO 22301 expects a continuity system you exercise and improve. Secrato keeps the risks, plans, procedures and evidence connected to the requirements they answer, so readiness holds rather than being assembled before each audit.
Maintain continuity plans and their operational procedures as governed, reviewable records. Keep ownership, version history and supporting policies connected as plans change.
Tie continuity risks to the controls used to treat them and keep treatment and residual exposure visible. Connect supporting evidence so teams can see how continuity measures address the risks identified through business impact analysis.
Maintain a current view of BCMS status, control readiness and audit readiness. Organise assessments, evidence and findings so reviews and certification activities work from current records rather than a one-time compilation.
Beyond the core outcomes above, these capabilities support the wider ISO 22301 programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
See where ISO 22301 controls also support requirements in other standards and regulations your organisation manages.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Cascade group-level decisions across workspaces while supporting approved local deviations where needed.
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
Many controls supporting an ISO 22301 BCMS also contribute to requirements under ISO 27001 or NIS2. The Unified Control Library maps those shared controls across the relevant frameworks, so continuity work can be reused without losing sight of the requirements specific to business continuity.
Explore the other supported frameworks →
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
IEC 62443
+ More and growing
ISO 22301:2019 is an international standard specifying requirements for a business continuity management system (BCMS), including processes for planning, implementing, operating, monitoring, reviewing, maintaining and continually improving the system to help an organisation prepare for and recover from disruptive incidents. ISO also lists Amendment 1:2024 on climate action.
ISO/IEC 27001 is an information-security management-system standard that includes information-security controls relevant to continuity. ISO 22301 is specifically a BCMS requirements standard. They share common management-system architecture, but neither standard is equivalent to or automatically satisfies the other.
Secrato supports ISO 22301 by keeping continuity risks, plans, procedures and supporting evidence connected, giving teams a clearer view of BCMS readiness and how the management system is being maintained over time.
Continuity plans and procedures matter most when they are current before disruption or review puts them to the test. See how Secrato can keep the risks, plans, procedures and evidence behind your BCMS connected and easier to oversee.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance