TISAX

TISAX® compliance ready for every partner who asks

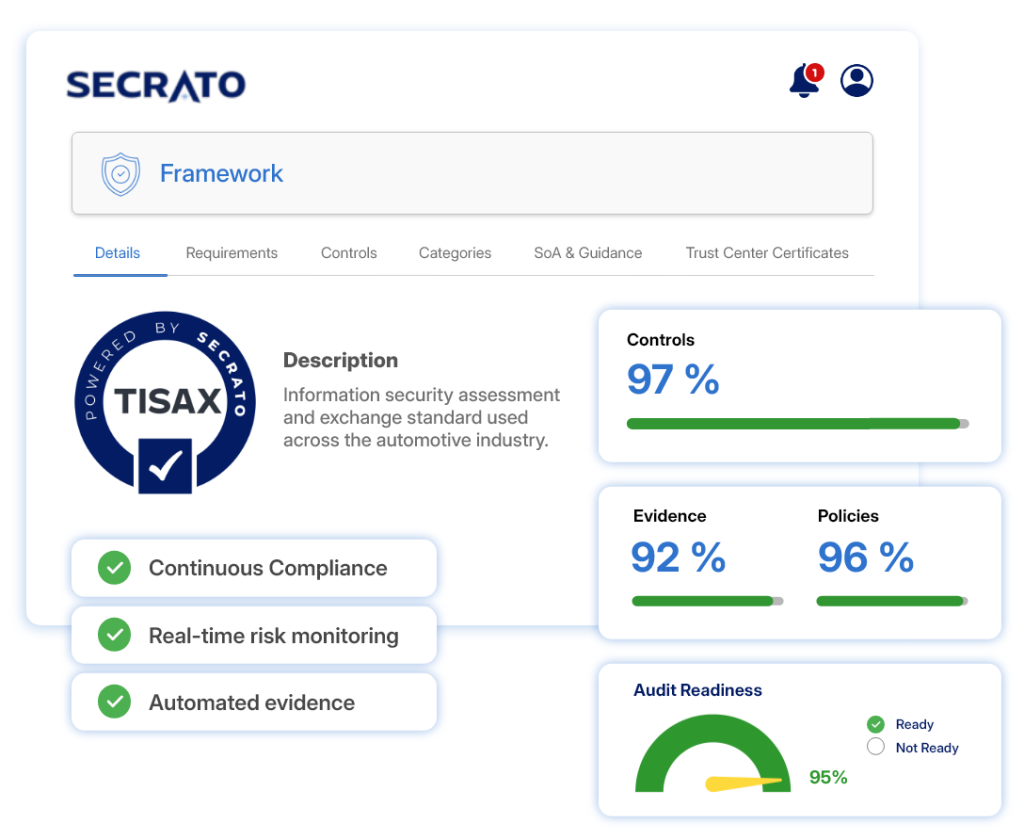
Secrato keeps TISAX controls, policies, evidence and assessment work connected, helping automotive organisations maintain readiness and demonstrate information security posture.

TISAX compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
MATURITY MANAGEMENT

See maturity gaps clearly

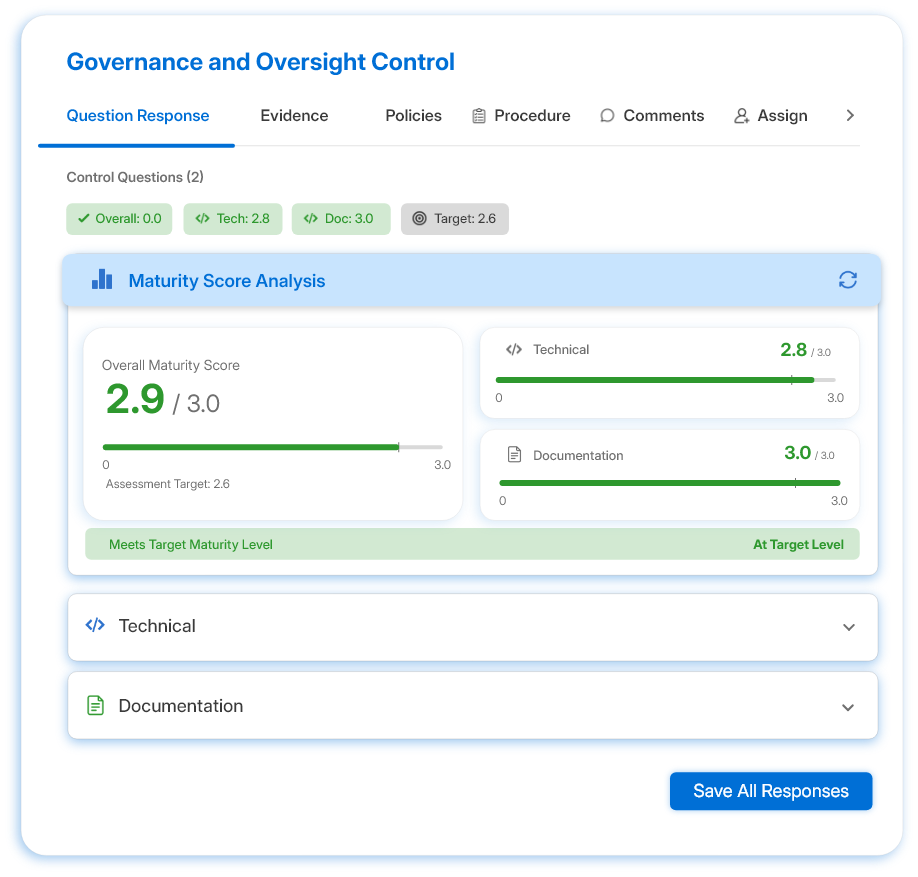
Score controls against their target maturity and see where improvement is required. Connect each response to its evidence, policies and protection needs so progress remains traceable.

  • Score controls against target maturity.
  • Link responses to evidence and policies.
  • Keep maturity gaps and progress visible.
Secrato platform: Maturity score
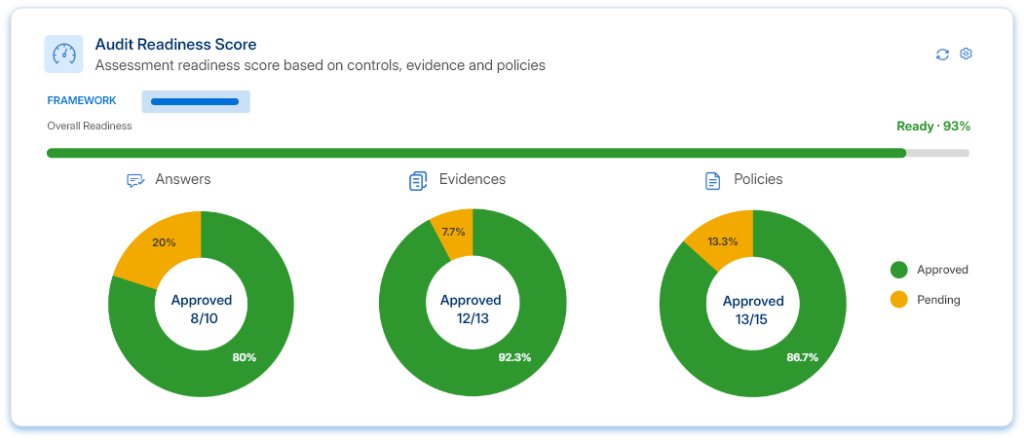
Secrato platform: Audit readiness score
ASSESSMENT READINESS

Prepare evidence before assessment

Maintain supporting evidence against each control and move assessment work from draft through active assessment to audit readiness. Keep records organised for the assessment provider.

  • Keep evidence linked to each control.
  • Move assessments through to audit readiness.
  • Organise records for assessment review.
ASSESSMENT READINESS

Prepare evidence before assessment

Maintain supporting evidence against each control and move assessment work from draft through active assessment to audit readiness. Keep records organised for the assessment provider.

  • Keep evidence linked to each control.
  • Move assessments through to audit readiness.
  • Organise records for assessment review.
Secrato platform: Audit readiness score
ONGOING READINESS

Maintain readiness between assessments

Keep requirements, controls, evidence and status current throughout the validity period. Share selected security information with authorised partners through controlled access when assurance is required.

  • Keep controls, evidence and status current.
  • Maintain readiness throughout the validity period.
  • Share selected assurance information securely.
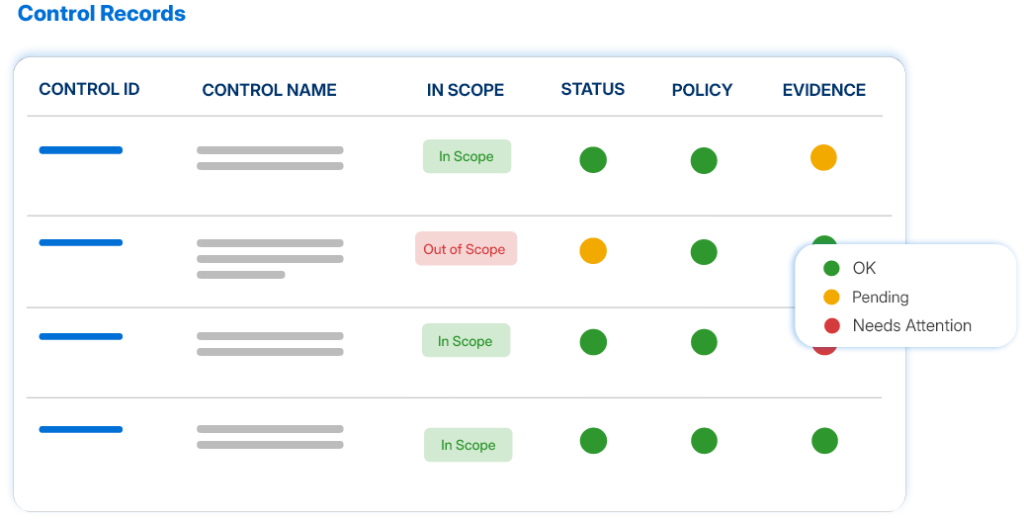
Secrato platform: Control records table
THE REST OF THE PLATFORM

More ways Secrato supports TISAX

Beyond the core outcomes above, these capabilities support the wider TISAX programme.

Keep risks tied to the controls and evidence behind their treatment, with visibility into ownership, treatment status and residual exposure.

Maintain ownership, review cycles, versions and attestations while connecting policies to the controls and evidence they support.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Review control readiness, bring evidence together and manage findings, with structured access for the audit provider where appropriate.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

TISAX shares many information-security foundations with other cybersecurity frameworks. The Unified Control Library maps shared controls across the relevant requirements, so existing security work can support TISAX readiness without being reassessed and maintained separately wherever the requirements overlap.

FAQs for TISAX compliance software

What is TISAX?

TISAX (Trusted Information Security Assessment Exchange) is an information-security assessment and exchange mechanism used by organisations in the automotive supply chain. The VDA Information Security Committee maintains the automotive Information Security Assessment (ISA) requirements, while ENX Association governs the TISAX scheme, including participant processes, approved audit providers and exchange of assessment results. Registered TISAX participants can exchange results through TISAX Exchange when the assessed company explicitly releases the result to the requesting participant.

TISAX is primarily relevant to organisations in the automotive industry and its supply chain that handle sensitive information for manufacturers, suppliers or partners. This can include companies working with confidential development data, prototypes, personal data or other information that needs to meet the information security expectations of the automotive sector.

Secrato makes TISAX preparation easier to manage by connecting VDA ISA requirements with the controls, evidence and assessment work behind them. Teams gain a clearer view of readiness and outstanding gaps, with supporting information kept organised for assessment and reusable across overlapping frameworks.

Stay ready for the next TISAX assessment

A TISAX result may be periodic, but the controls and maturity behind it need to hold up between assessments. See how Secrato can keep ISA readiness visible, so the next assessment starts from a current picture rather than a reconstruction.

Secrato