
IEC 62443 compliance you can show holds up
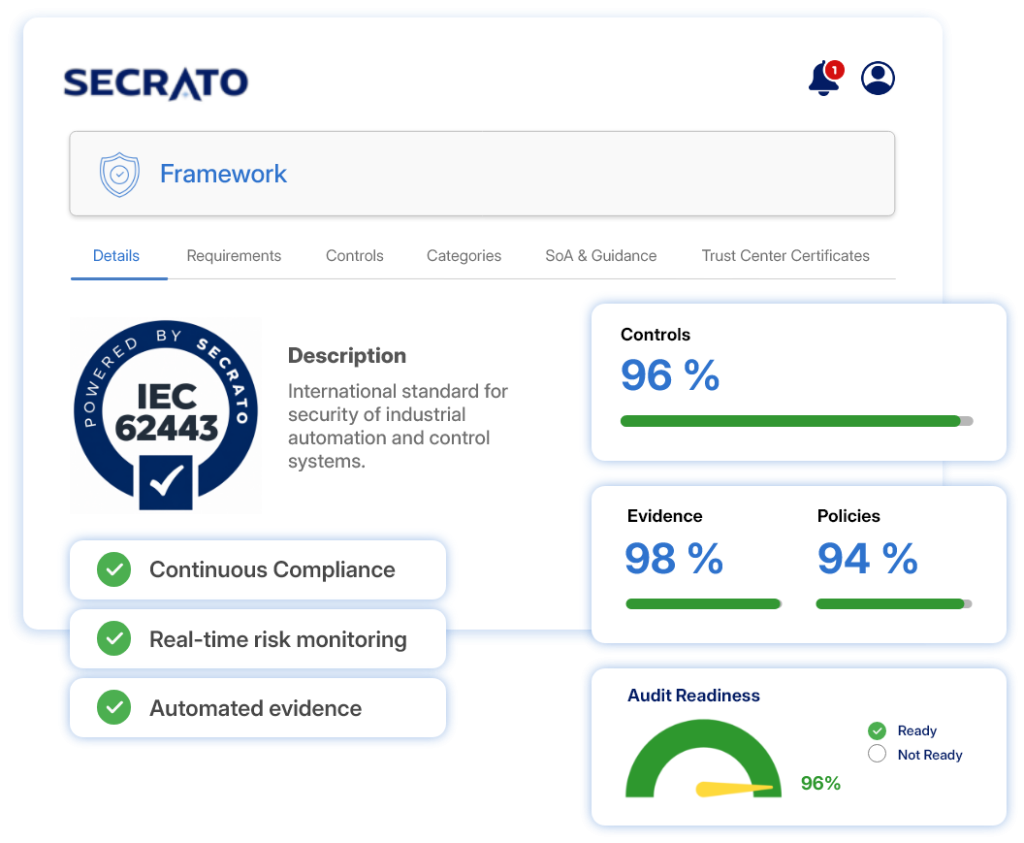
IEC 62443 asks you to prove your control system security holds up, then keep proving it. Secrato connects the controls and evidence to the requirements behind that proof, so the security level you hold stays visible against the one you set.
Connect risk to security controls
Tie identified risks to the controls used to treat them. Score controls against the target security level and keep gaps visible across the relevant requirements.
Link risks to treating controls.
Score controls against target security levels.
Keep security gaps visible.
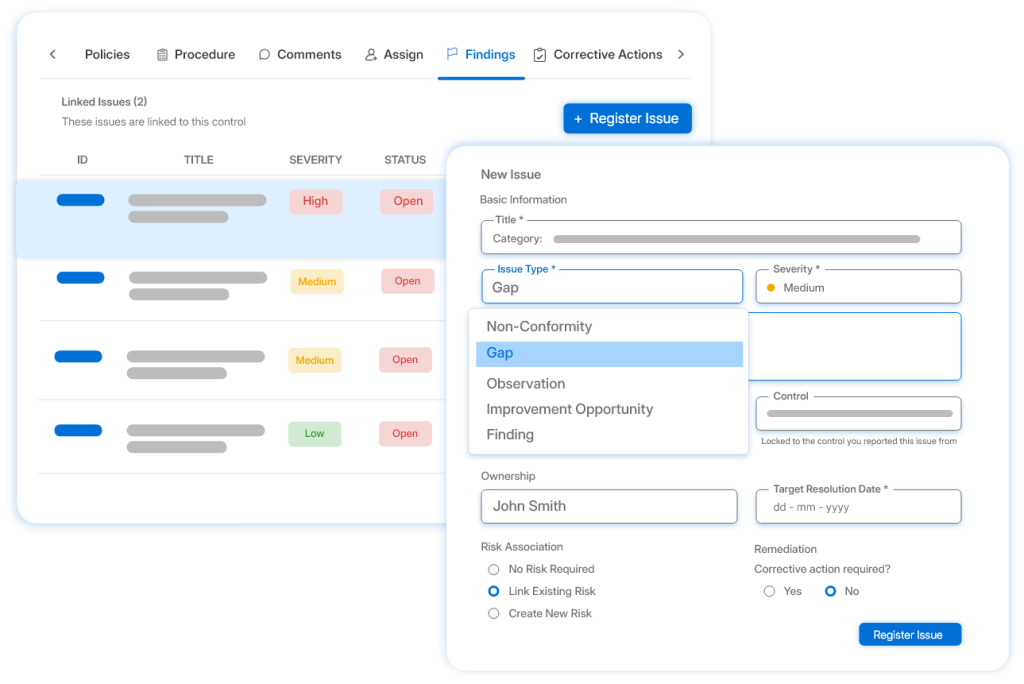
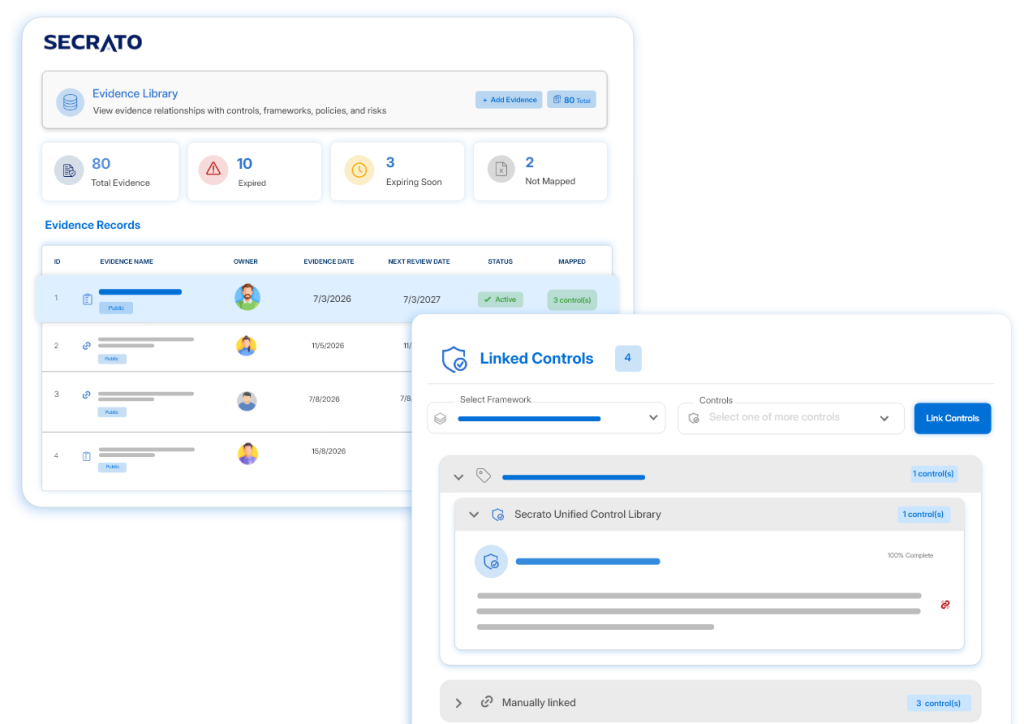
Keep supporting evidence organised
Assess requirements and connect every response to the evidence that supports it. Maintain records against their controls so supporting information stays structured and ready for review.
Link assessment responses to evidence.
Keep evidence organised against controls.
Prepare supporting records for review.
Keep responsibilities visible
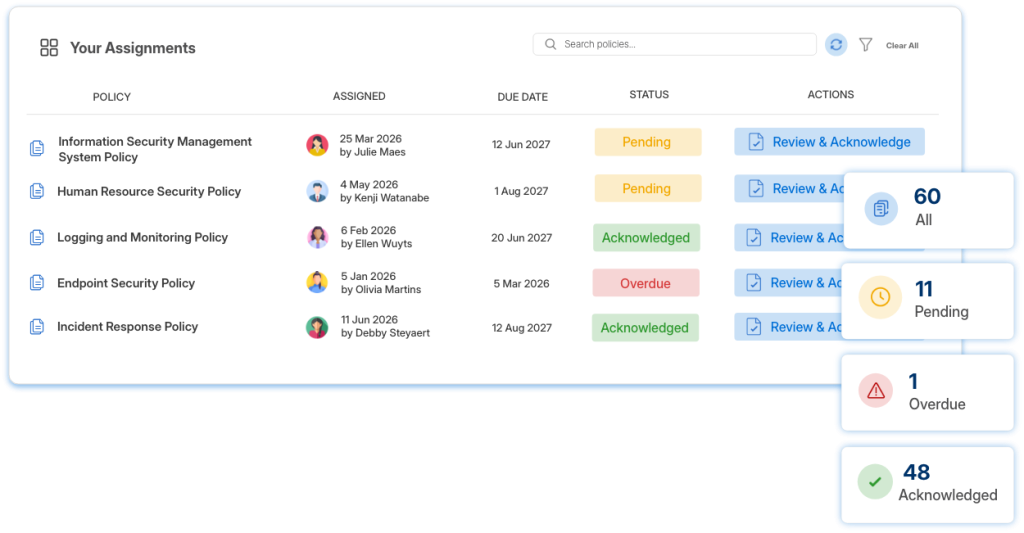
Connect policies, procedures, controls and evidence with clear ownership and review cycles. Maintain a shared view of readiness across parties with defined lifecycle responsibilities.
- Connect policies, procedures and controls.
- Keep ownership and review cycles visible.
- Maintain shared readiness across responsible parties.
More ways Secrato supports IEC 62443
Beyond the core outcomes above, these capabilities support the wider IEC 62443 programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Keep risks tied to the controls and evidence behind them, with visibility into ownership, treatment and residual exposure.
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
One control. Multiple frameworks.
Many IEC 62443 security measures overlap with controls already maintained in other cybersecurity frameworks. The Unified Control Library maps that shared control work across the relevant requirements, reducing duplication while keeping industrial-specific requirements such as zones, conduits and security levels clearly identifiable.
+ More & growing
FAQs for IEC 62443 compliance software
What is IEC 62443?
IEC 62443 is the international series of standards for securing industrial automation and control systems across their lifecycle, with responsibilities spanning asset owners, system integrators and product suppliers. IEC 62443 is voluntary rather than a law with a single compliance deadline, and adoption is commonly driven by procurement, contracts or sector requirements. The individual standards contain the detailed requirements for areas such as zones and conduits, security levels and lifecycle responsibilities.
Who does IEC 62443 apply to?
IEC 62443 addresses shared cybersecurity responsibilities across IACS asset owners, automation product suppliers, system integrators and service suppliers.
How does Secrato support IEC 62443?
Secrato supports the governance and evidence work around IEC 62443 by connecting controls, policies, risks and supporting evidence, giving organisations a clearer view of how requirements and responsibilities are being managed.
Keep security governance connected
IEC 62443 responsibilities span systems, sites and lifecycle roles, making visibility difficult when the supporting work is fragmented. See how Secrato can bring controls, risks, evidence and governance records together so readiness is easier to demonstrate.
