
Unified GRC built for EU-first trust
Secrato brings frameworks, controls, evidence, policies, risks, assessments and audits together in one governed environment. Give teams clearer oversight, reduce duplicated work and build assurance you can rely on.
ONE CONNECTED SYSTEM
A single place where frameworks, controls and evidence stay connected.
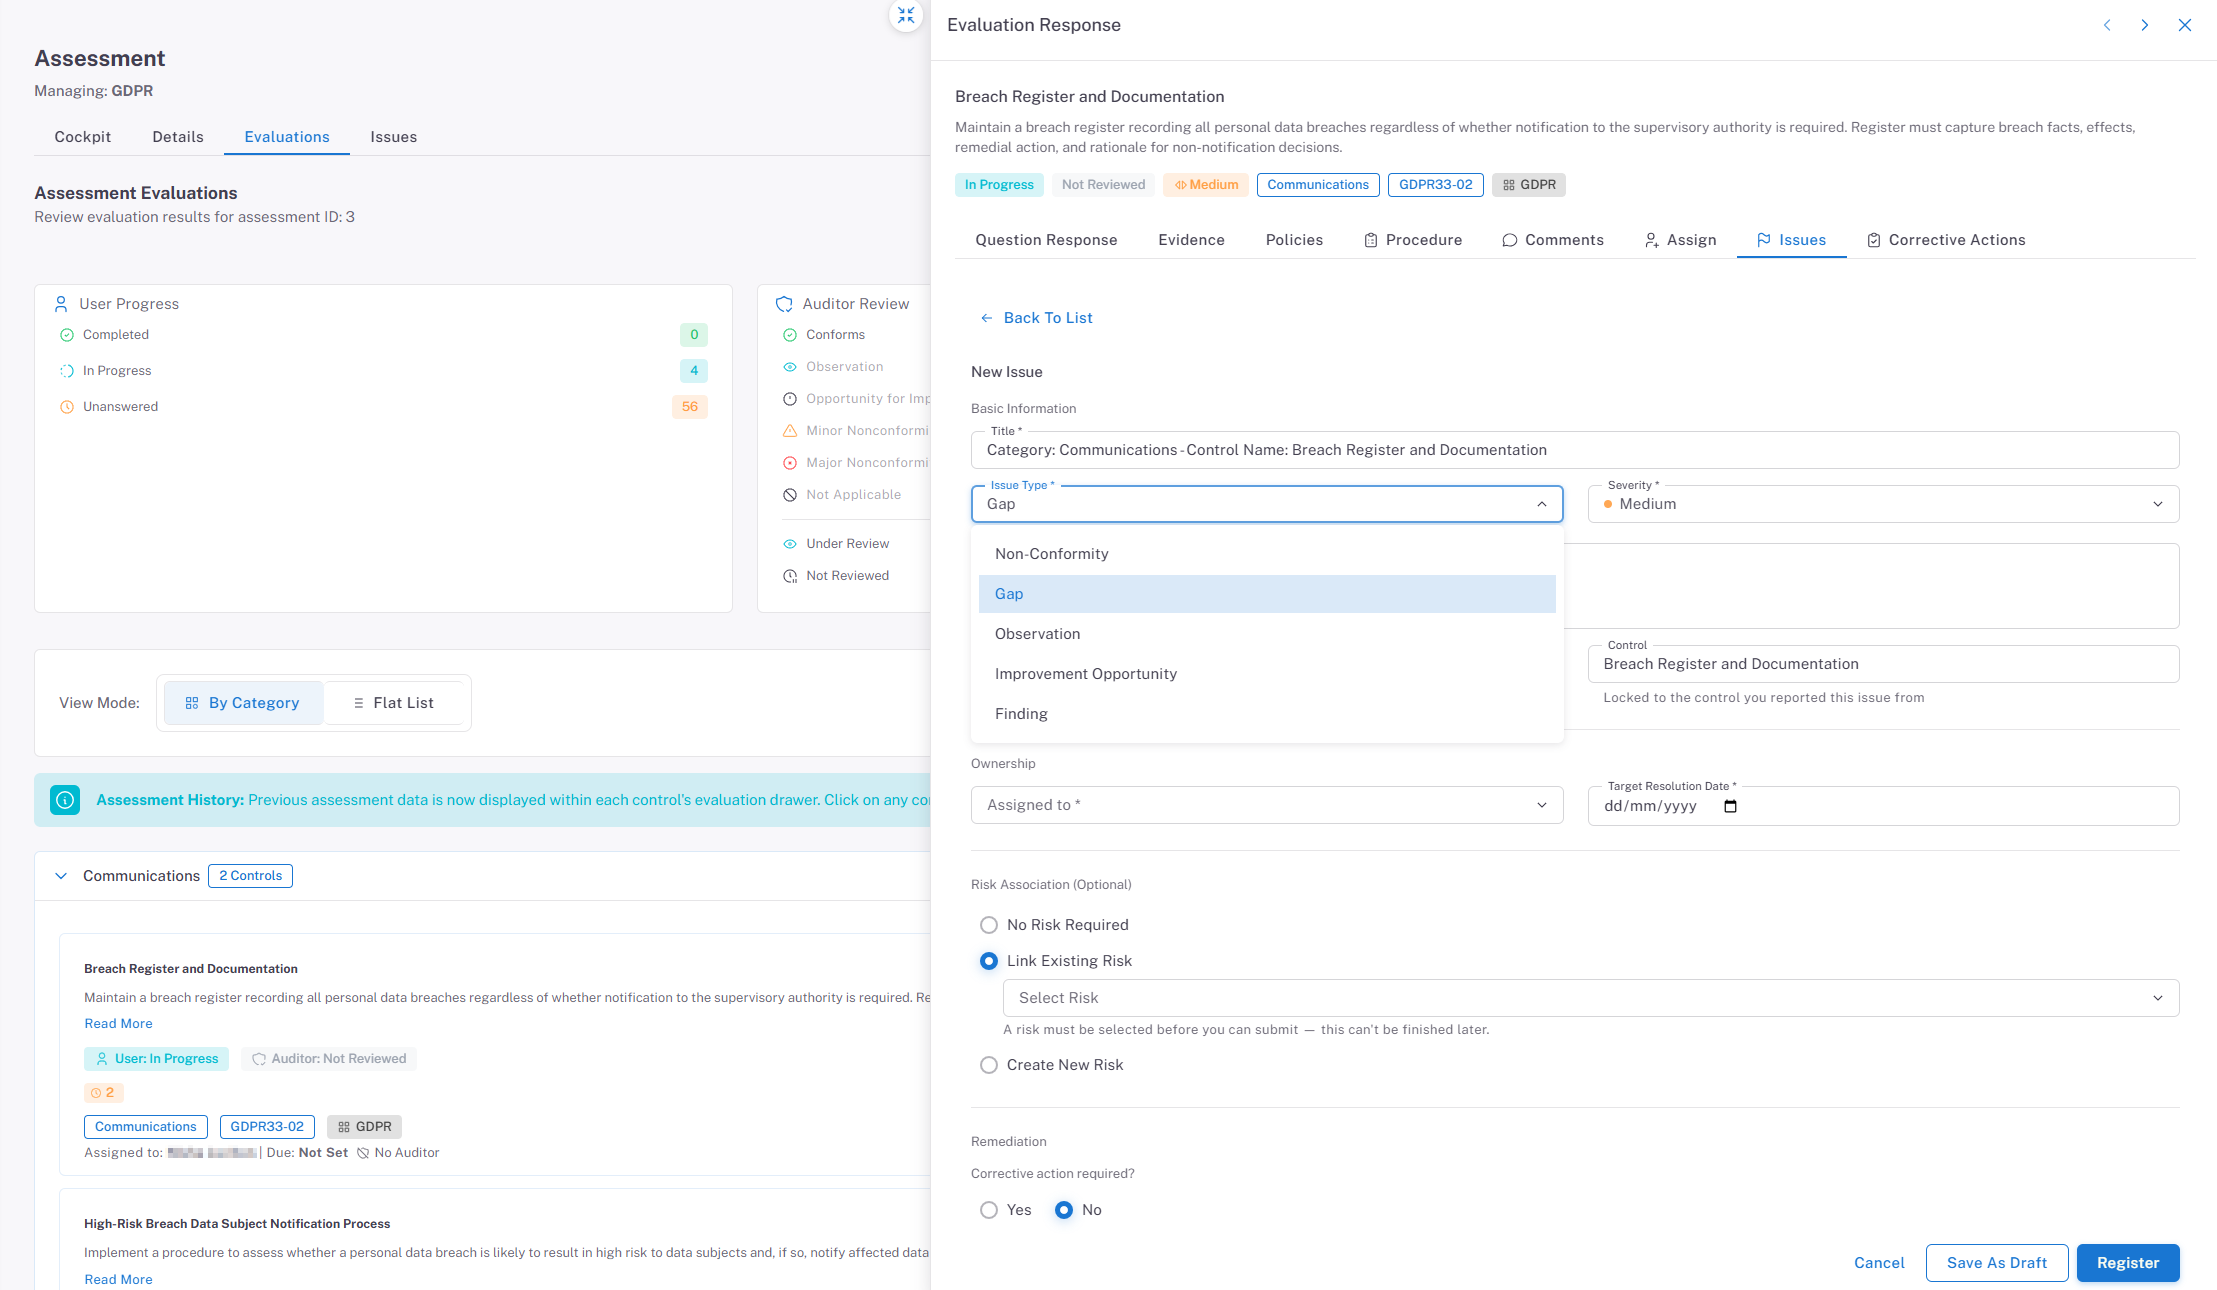
Assess a control once and it evidences every framework that depends on it, so overlapping requirements stop generating duplicate work.
Fragmented compliance, made whole.
One architecture. Every part of GRC connected.
At the centre of Secrato is the Unified Control Library, connecting requirements across frameworks with the controls and assurance activity that support them.
Build around common controls
Bring controls from different frameworks into a shared structure. See where they align and manage overlapping compliance work without treating every framework separately.
Keep context attached
Link controls with evidence, policies, procedures, risks, assessments and audits. Keep the records needed to understand and demonstrate compliance connected.
Build once. Apply more widely.
Reuse controls and supporting records across overlapping requirements. Reduce repeated work while maintaining clear traceability to each framework.
Be ready before the audit starts
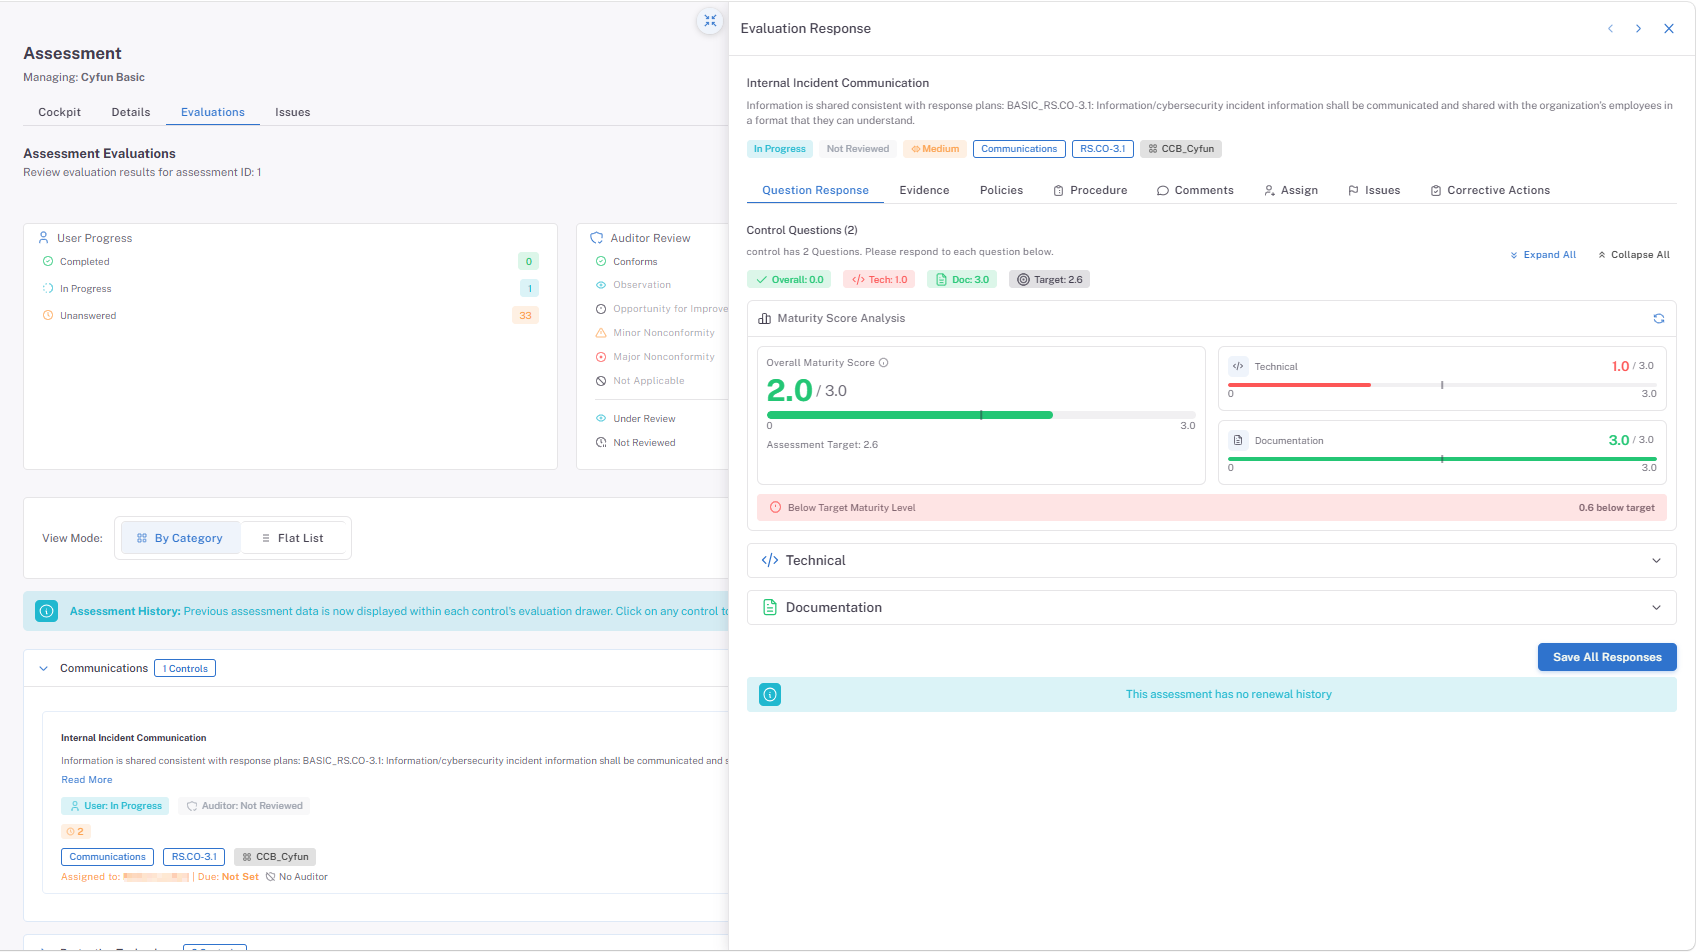
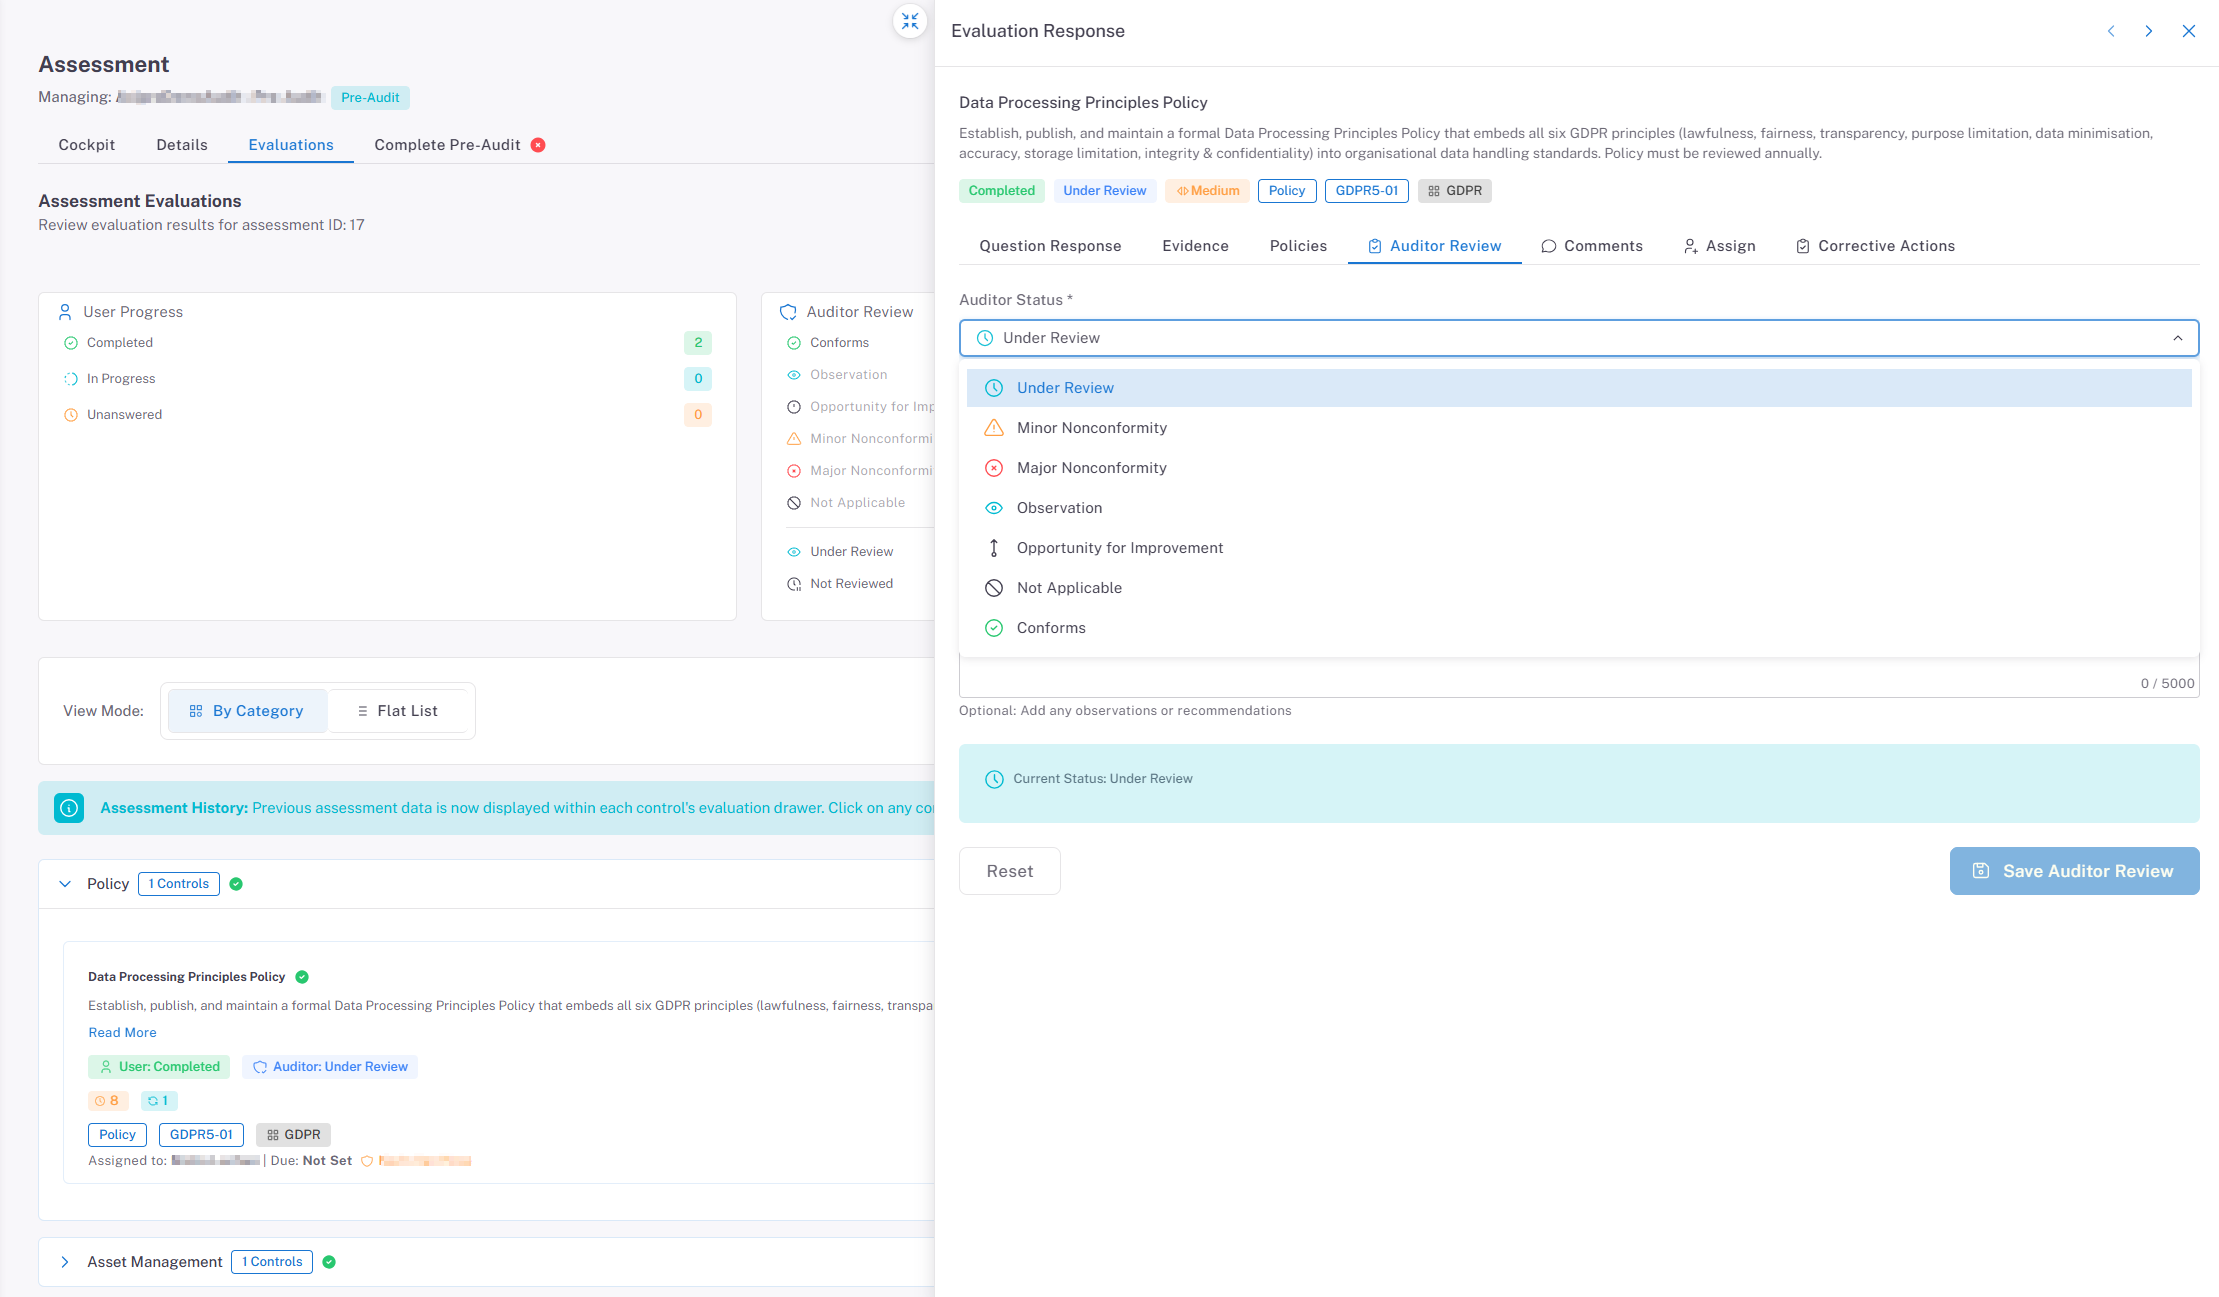
Keep the controls, evidence, policies and assessment activity behind assurance connected throughout the year. When an audit arrives, the supporting context is already structured and easier to review.
Know where compliance stands
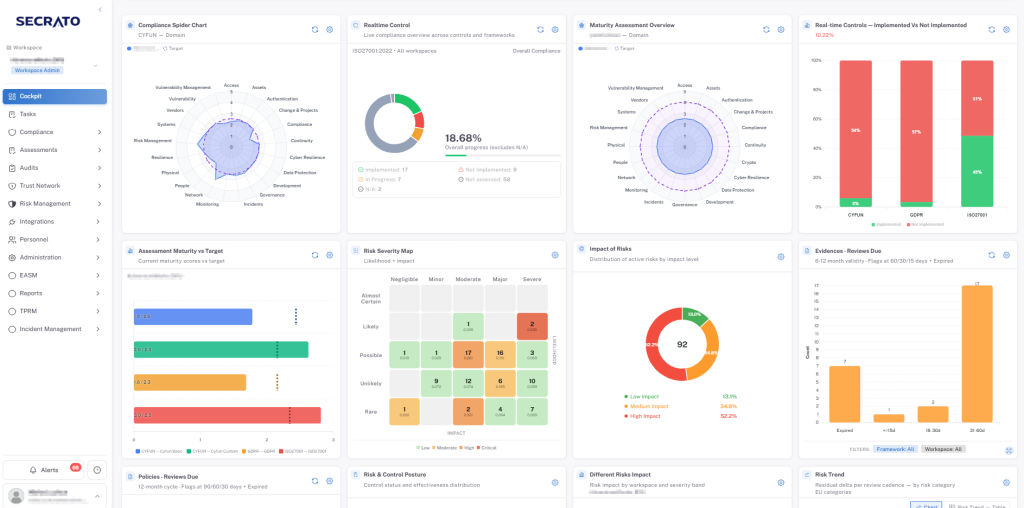
Keep controls, evidence and assessments current as work progresses. Secrato gives teams an ongoing view of compliance instead of rebuilding the picture only when reporting or review begins.
See what needs your attention
Bring activity across frameworks, risks, controls and teams into a clearer organisational view. Secrato helps leadership understand progress, gaps and accountability without relying on fragmented reporting.
Everything you need to govern and demonstrate compliance
Secrato brings the core disciplines of GRC together with each capability connected to the same underlying governance structure.
Devices & Personnel Management
Keep devices and people connected to the controls that govern them.
Trust Network
Present selected security and compliance information to external stakeholders.
Set direction centrally. Keep accountability local.
Secrato gives organisations the structure to govern across entities, teams and workspaces without losing local ownership.
Bring structure across the organisation
Manage governance across workspaces and subworkspaces while maintaining common standards and visibility at group level.
Keep responsibility where the work is
Let local teams manage the controls, evidence and compliance activity relevant to them, with clear roles and accountability.
See the bigger picture
Bring local records back into a wider organisational view so leadership can understand progress, exposure and where action is needed.
Work across frameworks without multiplying the work
Regulatory and assurance requirements increasingly overlap. Secrato helps teams map those connections, reuse controls and supporting evidence, and understand coverage across frameworks without rebuilding the same compliance work each time.
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
EU DATA SOVEREIGNTY
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Belgium · EU
Common questions
Who is Secrato designed for?
Secrato is designed for organisations managing growing governance, risk and compliance requirements across teams, entities or frameworks. It supports compliance, security, risk and audit teams while giving leadership a clearer view of how those activities connect.
Can Secrato adapt to the way our organisation manages GRC?
Yes. Secrato is designed to support different organisational structures, responsibilities and compliance programmes without forcing every team into an identical setup. Workspaces, roles, assessments and governance structures can be configured around how your organisation operates.
How does Secrato reduce manual compliance work?
Secrato reduces repeated work by connecting information that would otherwise be maintained separately, reusing controls across overlapping requirements and bringing supporting evidence into the compliance process through integrations and automation. Teams spend less time chasing information and more time acting on what needs attention.
Can Secrato support both ongoing compliance and audit preparation?
Yes. Compliance activity, evidence, policies, risks and assessments remain connected throughout the year rather than being assembled only when an audit approaches. This gives teams a stronger foundation for ongoing oversight and makes audit preparation a continuation of existing work rather than a separate exercise.
See how it all fits together
Discover how controls, evidence, policies, risk, assessments and audit connect across the frameworks your organisation needs to manage.
