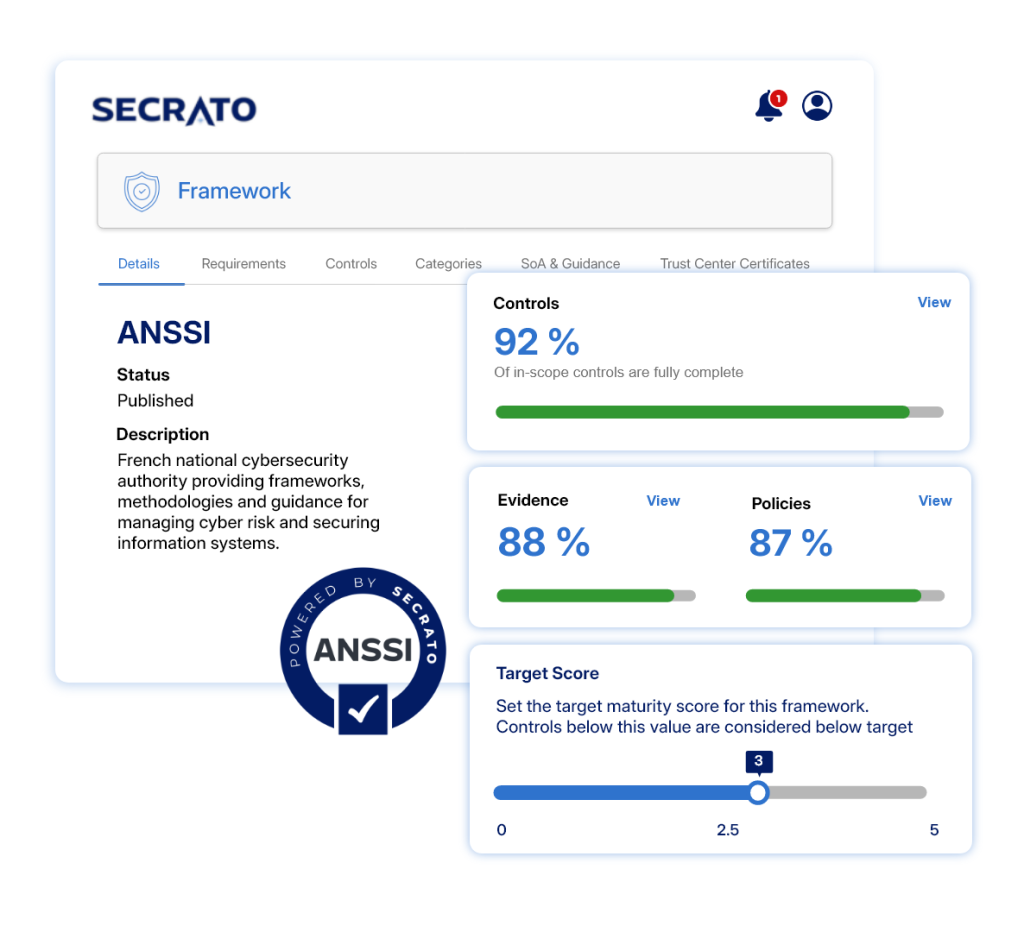
Secrato supports ANSSI-aligned security work by bringing controls, risks, policies, procedures and evidence into a traceable view, making it easier to maintain the security baseline and demonstrate how it is being applied over time.
Maintain security measures with their status, ownership, procedures and supporting evidence. Bring controls, policies and evidence together so teams can see what is implemented, what is supported and where further action is required.
Tie security measures and additional safeguards to the risks they address. Keep the risk context, treating controls, policies and supporting evidence connected so teams can follow why a measure exists and how it is being maintained.
Organise compliance status, evidence and findings into a traceable view of readiness. Keep records current and structured so internal teams, auditors and other authorised reviewers can follow how the security baseline is implemented and supported.
Beyond the core outcomes above, these capabilities support the wider ANSSI programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Maintain ownership, review cycles, versions and attestations while connecting policies and evidence to the controls, risks and assessments they support.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Cascade group-level decisions across workspaces while supporting approved local deviations where needed.
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
Many security controls supporting ANSSI guidance overlap with controls organisations already maintain. Secrato’s Unified Control Library maps shared controls across the relevant requirements, reducing repeated assessment and evidence work while keeping ANSSI-specific measures visible.
Explore the other supported frameworks →
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
ANSSI, the Agence nationale de la sécurité des systèmes d’information, is France’s national authority for cybersecurity and cyberdefence. It publishes cybersecurity guidance, supports public authorities and critical organisations, and operates certification and qualification schemes for defined products and services.
ANSSI guidance and ISO/IEC 27001 share many information-security foundations, creating opportunities to reuse controls and evidence where requirements correspond. They are not interchangeable, however. ANSSI publications can introduce national, technical or assurance requirements that sit outside ISO 27001, so mappings should be treated as correspondence rather than equivalence.
Secrato connects ANSSI requirements with the controls, risks, policies, evidence and assessments used to manage them. Teams can track implementation, identify gaps and maintain clear traceability across their security programme, while reusing relevant control work across other supported frameworks.
ANSSI-aligned security work is easier to defend when the measures, controls and evidence behind it remain connected. Secrato keeps that governance record visible and traceable, so teams can maintain readiness between reviews.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance