
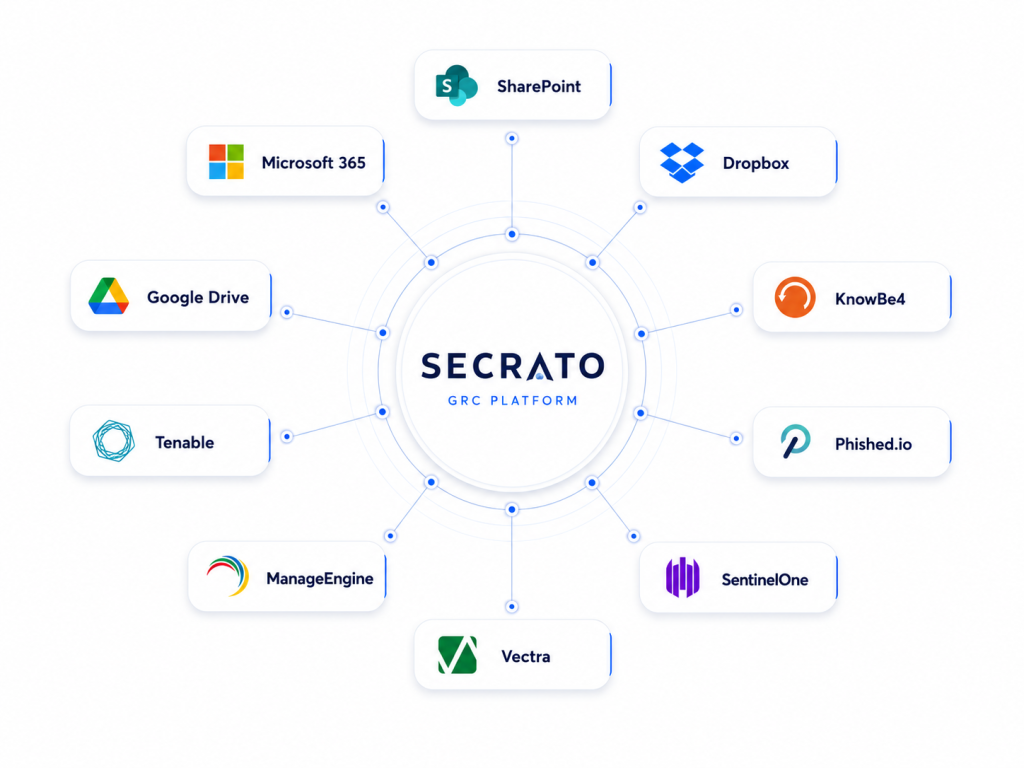
Connect your systems once and turn them into evidence you can reuse
Bring evidence from the systems your teams already use into Secrato. Through APIs and integrations, evidence can stay connected to the controls, risks and assurance activity it supports, reducing repeated collection and keeping compliance work better prepared for audits.
Keep evidence closer to its source
The evidence behind compliance already exists across security, IT and business systems, but bringing it together and keeping it current is the challenge. Secrato turns connected systems into ongoing evidence sources, keeping evidence governed, reusable and connected to the wider compliance picture.
Integrations Catalog
Secure enterprise collaboration and content management through Microsoft 365.
Cloud-based file storage and sharing for managing compliance and operational documents.
Secure document repository with versioning and easy external sharing.
Centralized endpoint configuration, patching, and remote management across devices.
Delivers simulated phishing campaigns and security awareness training to employees.
Unified log collection, correlation, and threat analytics for regulatory compliance.
Identity governance and secure access across hybrid and cloud environments.
AI-driven phishing simulations and adaptive learning for user risk reduction.
Autonomous endpoint protection with behavioral AI for real-time threat response.
Continuous vulnerability detection and risk-based prioritization across assets.
Comprehensive IT service management solution with automation and SLA tracking.
Not limited to this list. Connect any cloud tool via our open API — new integrations are added continuously.

Built around the work that matters
Automate evidence collection
Bring evidence into Secrato through connected systems and APIs, supporting more continuous collection between audit cycles.
Import from cloud storage
Import evidence from connected cloud storage and associate it with the records and controls it supports.
Flexibility and manual collection
Upload files or add external share links when evidence cannot be collected through an integration.
Control-level evidence
Attach evidence directly from the control it supports, keeping compliance work connected without moving between separate records.
Bring different sources together
Files, tickets, alerts, configuration data and scan are easier to review alongside the controls they support.
Evidence Provenance
Imported evidence retains information about its source and collection time, so you can trace back to the system it came from.
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Belgium · EU
Common questions
Which systems can Secrato collect evidence from?
Secrato connects to security, IT and business systems through APIs and integrations. Evidence can include files, tickets, alerts, configuration data and scan outputs, depending on the connected source.
Can we still add evidence manually?
Yes. Automated collection can be complemented by manual options, including file uploads, external share links, connected cloud storage and evidence added directly from a control. These routes feed into the same evidence environment.
How does connected evidence relate to controls and risks?
Evidence can be mapped to Unified Control Library controls, the frameworks those controls support and relevant risk records. This gives teams clearer context around what the evidence supports and where it can be reused.
Connect with Confidence
The evidence your audits depend on already exists in your organisation. See how a connected system can move from evidence source to control, framework and audit preparation in Secrato.