ISO 27001

ISO 27001 compliance that stays audit-ready

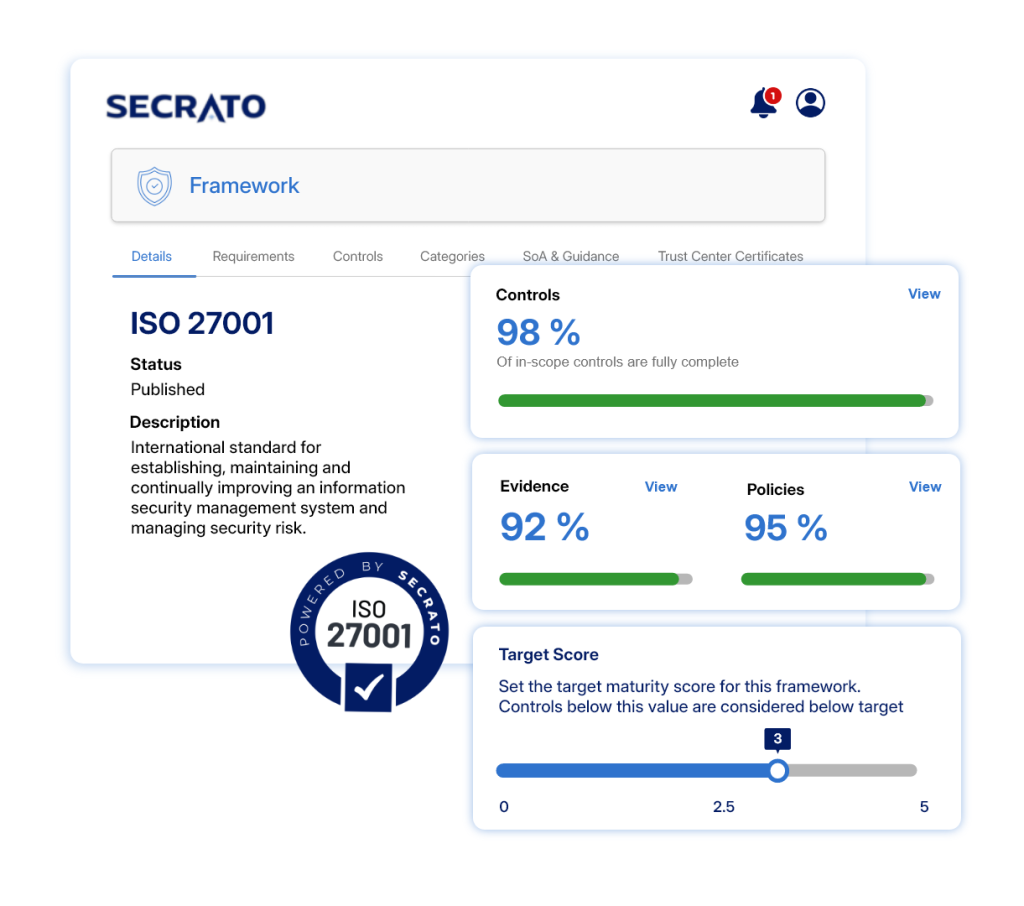
ISO 27001 asks you to run an information security management system and show it works. Secrato keeps your controls and evidence connected to the requirements they answer, so what you can demonstrate stays current.

GDPR BY DESIGN
HOSTED IN BELGIUM
EU DATA SOVEREIGNTY
ENTERPRISE-GRADE SECURITY
EVIDENCE READY

Keep controls backed by current evidence

Connect evidence directly to the Annex A controls it supports, so you can see what is in place and where attention is needed. Keep records current and traceable as evidence changes, reducing manual work when preparing for reviews and audits.

IEC 62443 compliance risk management controls
CONNECTED ENVIRONMENT

Connect risks, controls and policies

Bring the relationships between risks, controls and governing policies into one connected environment. See how risks are treated, who owns each control and which policies and procedures support it, without reconciling information across disconnected records.

AUDIT READINESS

Stay ready for review and audit

Maintain a current view of control status, risk posture and ISO 27001 readiness throughout the assessment cycle. Give leadership, internal audit and certification auditors clearer access to the records and evidence needed to review how requirements are being met.

THE REST OF THE PLATFORM

More ways Secrato supports ISO 27001

Beyond the core outcomes above, these capabilities support the wider ISO 27001 programme.

Compliance Engine

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Assessments

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Audit Hub

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

Framework Mapping

See where controls supporting ISO 27001 also address requirements in the other standards and regulations your organisation carries.

API and integrations

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Trust Network

Share relevant security and compliance information with stakeholders through controlled public or gated access.

SUPPORTED FRAMEWORKS

One control. Multiple frameworks.

Many ISO 27001 controls overlap with security requirements organisations also manage under NIS2, DORA and other cybersecurity frameworks. Secrato’s Unified Control Library maps shared controls across the relevant requirements, so teams can maintain and assess common control work once while keeping the requirements unique to each framework clearly visible.

Explore the other supported frameworks →

NIS 2

CYFUN

GDPR

DORA

EU CRA

NIST CSF 2.0

PCI DSS

TISAX

ISO/IEC 42001

ANSSI

ISO 9001

ISO 14001

BSI

ISO 22301

IEC 62443

+ More and growing

FAQs for ISO 27001 compliance software

What is ISO 27001?

ISO/IEC 27001 is the international standard setting the requirements for an information security management system (ISMS). ISO/IEC 27001:2022 is the current edition of the international standard for information security management systems. It defines the requirements an ISMS must meet, while ISO/IEC 27002:2022 provides companion guidance on information security controls.

Yes, where requirements genuinely overlap. Controls maintained for ISO 27001 can often support corresponding requirements in other cybersecurity frameworks. Secrato maps that shared control work through the Unified Control Library while keeping each framework’s distinct obligations visible.

Secrato supports ISO 27001 readiness by connecting requirements, controls, risks, policies, evidence and assessments, giving organisations a clearer and more traceable view of how the ISMS is being implemented, maintained and demonstrated.

Keep ISO 27001 readiness current between audits

An ISMS is stronger when controls, risks and evidence remain connected. Secrato keeps the governance record behind ISO 27001 visible and traceable, giving teams a clearer view of readiness as the management system evolves.

Secrato