ALL FRAMEWORKS

Compliance frameworks for every requirement that matters

Explore the compliance frameworks Secrato supports—from GDPR, NIS2 and DORA to ISO/IEC 27001—in one connected, EU-first GRC platform.

FRAMEWORKS SECRATO SUPPORTS

Compliance frameworks that matter for Europe

Secrato is built for European businesses first, delivering seamless compliance coverage for critical EU regulations and global standards.

20+

FRAMEWORKS

1

CONTROL LIBRARY
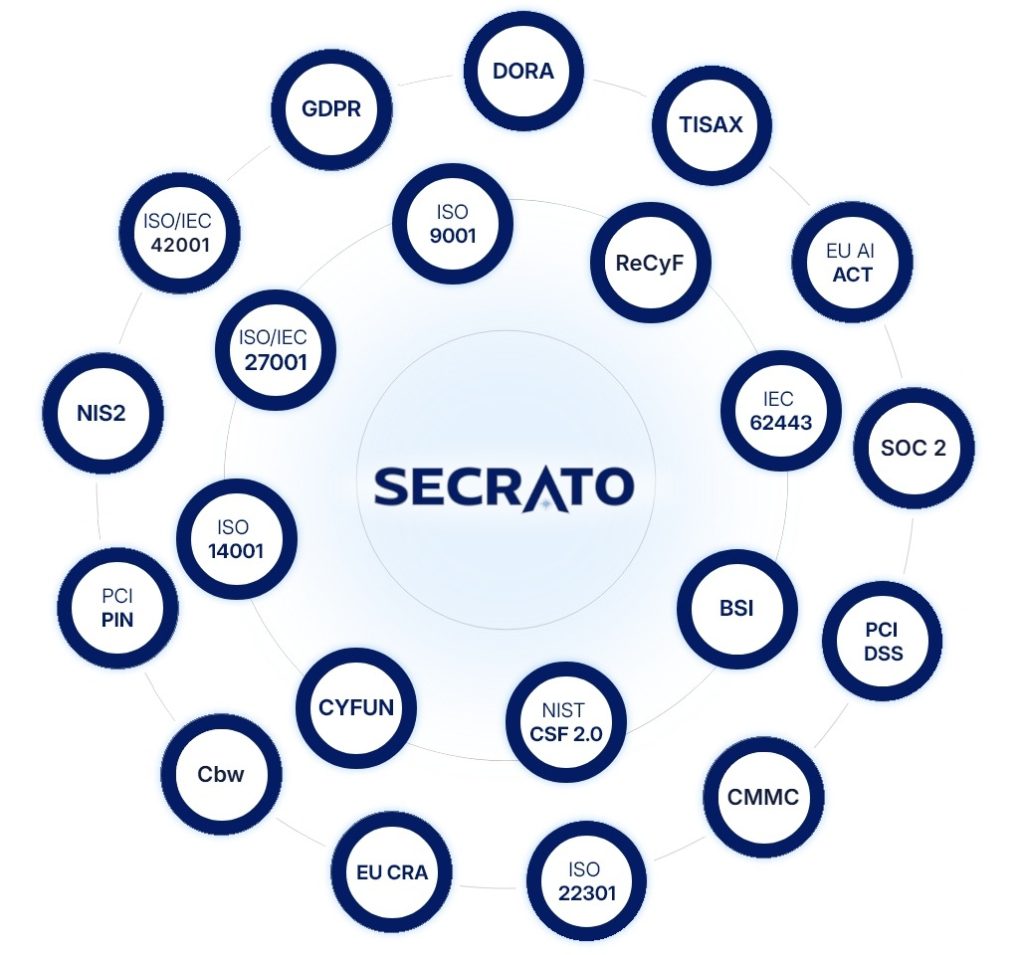
Frameworks supported by Secrato: EU regulations, ISO standards, national laws and schemes, and industry and security standards
EU REGULATIONS & DIRECTIVES

Binding obligations set by EU

NIS2 DIRECTIVE

NIS2

EU directive setting cybersecurity and incident-reporting obligations for essential and important entities. 

DATA PROTECTION

GDPR

EU regulation governing the protection of personal data and privacy for individuals in the EU.

OPERATIONAL RESILIENCE

DORA

EU regulation setting ICT risk management and resilience requirements for the financial sector.

CYBER RESILIENCE ACT

CRA

EU regulation setting cybersecurity requirements for products with digital elements sold in the EU market.

ARTIFICIAL INTELLIGENCE

EU AI Act

EU regulation setting risk-based requirements for AI systems and general-purpose AI models.

INTERNATIONAL MANAGEMENT STANDARDS

Certifiable management systems across markets and sectors

ISMS

ISO/IEC 27001

International standard for establishing and maintaining an information security management system.

QMS

ISO 9001

International standard for quality management systems.

EMS

ISO 14001

International standard for environmental management systems.

AIMS

ISO/IEC 42001

International standard for management systems governing the responsible use of artificial intelligence.

BCMS

ISO 22301

International standard for business continuity management systems.

NATIONAL LAWS & SCHEMES

Country-specific requirements from national laws and cybersecurity authorities

BELGIUM · CCB

CyFun®

Belgian cybersecurity framework of baseline controls for organisations operating in Belgium.

FRANCE · ANSSI

ReCyF

ANSSI reference for NIS2 in France, with security objectives and acceptable means of compliance.

GERMANY · BSI

BSI IT-Grundschutz

Reference security standards and certification schemes set by Germany’s federal cybersecurity agency.

NETHERLANDS · NCSC

CyberbeveiligingswetCbw

Dutch law implementing NIS2, with the Cyberbeveiligingsbesluit setting the minimum security measures.

UNITED STATES · DoD

CMMC

US Department of Defense programme that verifies how contractors protect FCI and CUI.

INDUSTRY & SECURITY STANDARDS

Sector standards and security frameworks for supply chains and industries

AUTOMOTIVE SECURITY

TISAX®

Information security assessment and exchange standard used across the automotive industry.

PAYMENT CARD SECURITY

PCI DSS

Global security standard for organisations handling payment card data.

PIN SECURITY

PCI PIN Security

PCI SSC standard for the secure management, processing and transmission of PIN data in card payments.

INDUSTRIAL CONTROL SECURITY

IEC 62443

International standard for security of industrial automation and control systems.

CYBERSECURITY FRAMEWORK

NIST CSF 2.0

Voluntary NIST framework for managing cybersecurity risk, organised around six core functions from Govern to Recover.

SERVICE ASSURANCE

SOC 2®

AICPA attestation report on a service organisation’s controls against the Trust Services Criteria.

CUSTOM FRAMEWORKS

Don't see your framework? Ask Secrato to build it for you. Or create a custom one.

Combine requirements from any standard framework or your own internal policies into a framework built around your organisation, tracked the same way as everything else in the register. 

EU DATA SOVEREIGNTY

GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.

Belgium · EU

Common questions

Which frameworks does Secrato support today?

Secrato covers 20+ frameworks across four groups: EU regulations and directives, international management standards, national laws and schemes, and industry and security standards. The full set is listed in the register above and new frameworks are added regularly.

You can build it yourself. Alongside the supported frameworks, Secrato lets you compile controls from any standard framework or your own internal policies into a custom framework, tracked the same way as every other entry in the register.

No. When a control satisfies requirements across more than one framework, Secrato maps it once and reuses it everywhere it applies. Mapping a control for NIS2 that also counts toward ISO/IEC 27001 means the work carries across without being repeated.

Run your frameworks in Secrato

Request a demo and we’ll walk through the frameworks that apply to your organisation, and how Secrato maps them together.

Secrato