NIS2

NIS2 compliance that's reporting-ready before the clock starts

NIS2 asks essential and important entities to show risk management continuously and report inside 24 and 72 hours. Secrato keeps the risk measures and incident records connected to the requirements they answer, so each submission draws on evidence already in order.

In short: Secrato is an EU-first GRC platform for NIS2 compliance, hosted in Belgium. It links the NIS2 risk-management measures to controls, owners, evidence and risks, and keeps incident records ready for the 24-hour early warning, the 72-hour notification and the final report. Belgian organisations can start free with the NIS2 Starter, built on CyFun® BASIC.

NIS2 compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
CONTROL ACCOUNTABILITY

Turn measures into accountable controls

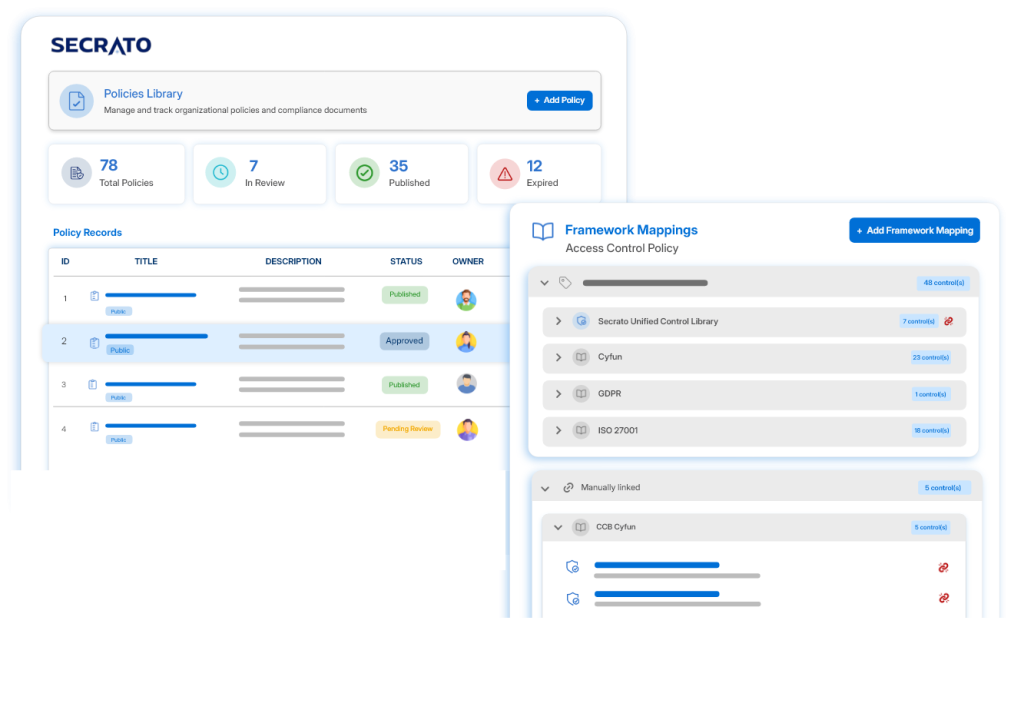
Connect NIS2 measures to the risks they address, the controls that implement them and the policies that govern them. Keep ownership, acknowledgement and supporting records visible.

  • Connect policies to the controls they govern.
  • Keep ownership and acknowledgements visible.
  • Link measures to risks and supporting controls.
Secrato platform: Policies library
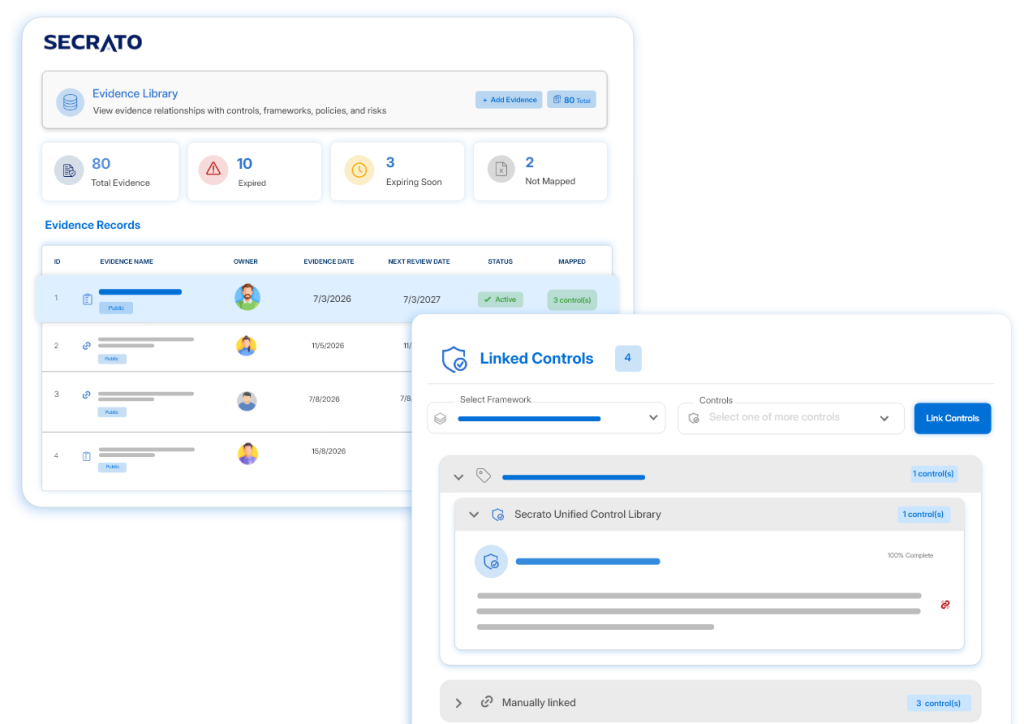
Secrato platform: Evidence library
EVIDENCE READINESS

Keep the evidence ready when it matters

Maintain evidence against the controls it supports and keep records current between incidents. When reporting obligations arise, teams can work from information already organised.

  • Keep evidence linked to supporting controls.
  • Maintain current records between incidents.
  • Reduce evidence gathering when reporting starts.
EVIDENCE READINESS

Keep the evidence ready when it matters

Maintain evidence against the controls it supports and keep records current between incidents. When reporting obligations arise, teams can work from information already organised.

  • Keep evidence linked to supporting controls.
  • Maintain current records between incidents.
  • Reduce evidence gathering when reporting starts.
Secrato platform: Evidence library
MANAGEMENT OVERSIGHT

Strengthen management oversight

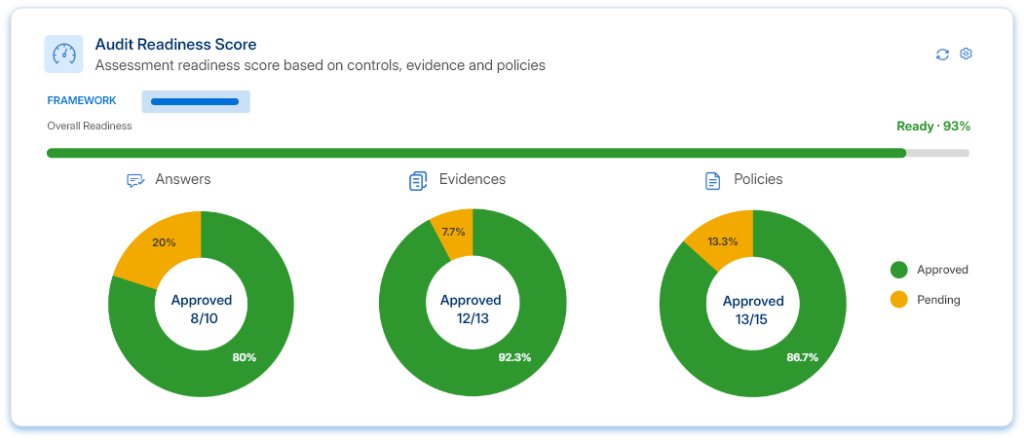
Give the management body a current view of compliance status, risk posture and readiness. Keep assessments, findings and supporting records organised for internal and competent-authority review.

  • Track compliance status and readiness.
  • Keep findings and assessments organised.
  • Support management and authority review.
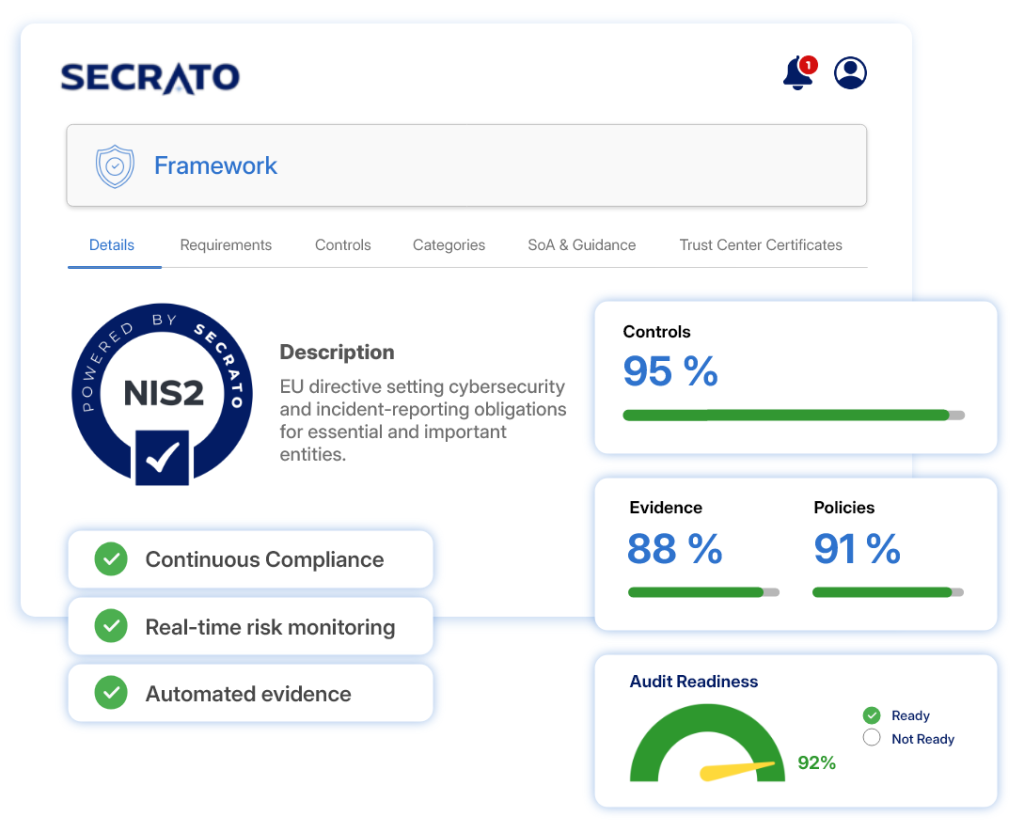
Secrato platform: Audit readiness score
THE REST OF THE PLATFORM

More ways Secrato supports NIS2

Beyond the core outcomes above, these capabilities support the wider NIS2 programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Bring the evidence that supports NIS2 controls, policies and risks so implementation is backed by maintained operational detail.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

Many NIS2 risk-management measures overlap with controls already maintained for ISO/IEC 27001 and other cybersecurity frameworks. The Unified Control Library maps those shared controls across the relevant requirements, reducing repeated assessment work while keeping the obligations unique to NIS2 visible.

FAQs for NIS2 compliance software

What is NIS2?

NIS2 is the EU directive setting cybersecurity risk management and incident reporting obligations for essential and important entities, with management bodies accountable for compliance. NIS2 has applied since 18 October 2024 and sets baseline obligations for essential and important entities across the sectors in Annexes I and II. 

NIS2 applies to entities in the sectors listed in Annexes I and II that fall within the Directive’s definitions and size rules, including generally medium-sized and larger entities. Certain categories are covered irrespective of size, while exclusions and special rules also apply. Whether a particular organisation is in scope ultimately depends on the Directive as transposed and applied in the relevant Member State. Check your scope with the NIS2 scope checker or see all NIS2 sectors.

For significant incidents, NIS2 (Article 23) sets a staged timeline: an early warning to the CSIRT or competent authority within 24 hours of becoming aware of the incident, an incident notification with an initial assessment within 72 hours, intermediate reports on request, and a final report no later than one month after the incident notification. National transposition laws can add detail, so check the rules of the Member State concerned.

Secrato supports NIS2 readiness by connecting risk measures, controls, evidence and reporting records to the requirements they satisfy, so an organisation can maintain and demonstrate them over time.

It should map the NIS2 measures through a recognised framework (CyFun® or ISO/IEC 27001), track owners and evidence for every control, support incident reporting to the CCB within 24 hours, 72 hours and one month, and keep compliance data in the EU. Secrato does all four and is hosted in a Belgian data centre. See how it compares with other platforms on our comparison page.

See where your NIS2 readiness stands

Bring risk-management measures, controls, evidence and ownership into a clearer view of what is covered and what still needs attention. See how Secrato can make NIS2 easier to oversee, maintain and demonstrate across the organisation.

Secrato