Keep sensitive GRC data within European control
Secrato processes GRC data on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment, combining European data sovereignty with a governance model designed for complex organisations.
In short: Secrato processes all GRC data – controls, evidence, policies, risks, assessments and audits – on self-managed infrastructure in a Tier IV data centre in Antwerp, Belgium, under EU law. Compliance data stays under European jurisdiction for organisations that must show data residency to regulators, customers or auditors.
Control starts with where data runs
Sensitive GRC information can include evidence, risks, policies, assessments and audit records. Its location and the legal environment surrounding it therefore matter alongside the controls applied within the platform.
For organisations operating under European regulatory requirements, clear answers around hosting, processing and governance provide a stronger foundation for security and procurement review.
Infrastructure, jurisdiction and governance aligned
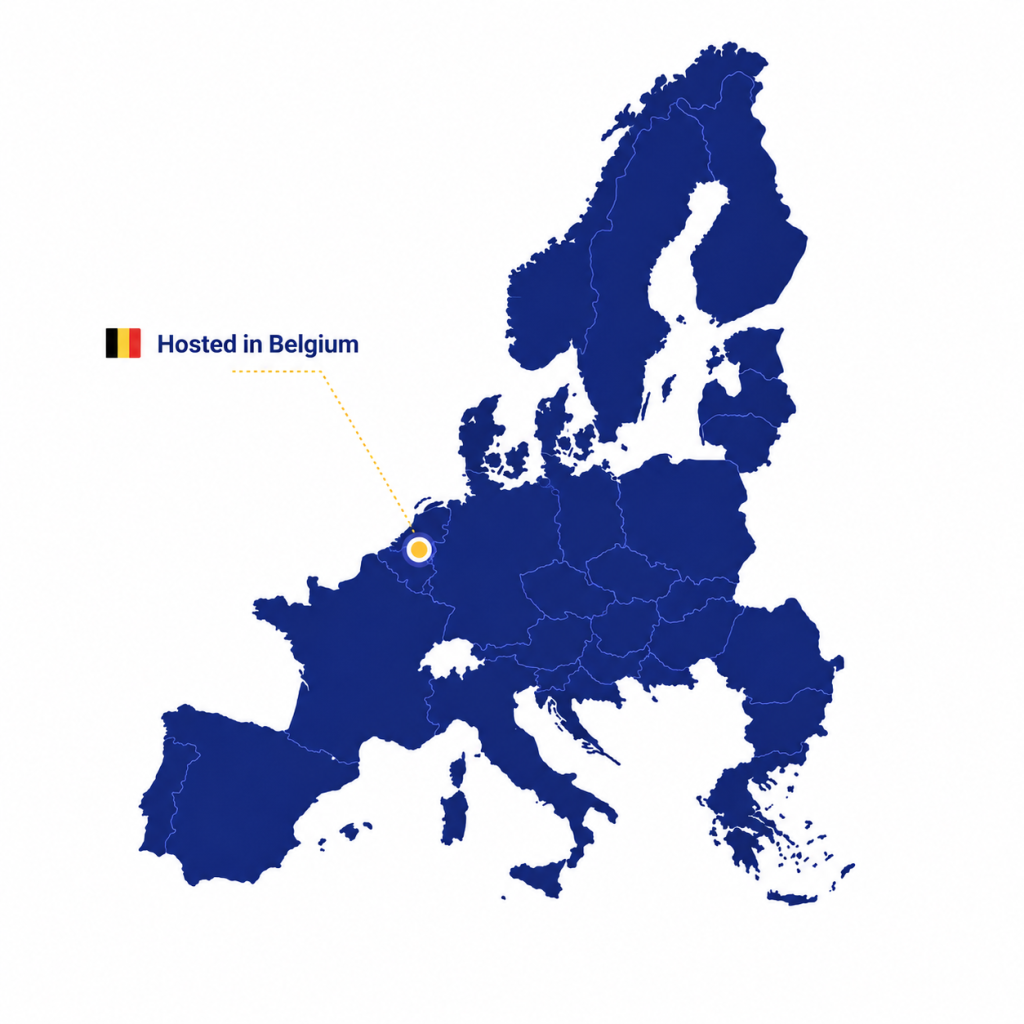
Your data lives in the EU
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Enterprise-Grade Security
Built for enterprise assurance, with alignment to GDPR and EU cybersecurity frameworks, hosting at Datacenter United’s Tier IV data centre in Antwerp (ISO/IEC 27001, ISAE 3402 Type II), TLS 1.3 encryption, immutable audit logs and soft-deletion lifecycles across all plans.
Independence and Trust by Design
Gain strategic and regulatory independence through fully EU-operated infrastructure aligned with GDPR, NIS2 and the EU Cybersecurity Act.
BUILT FROM BELGIUM
European at the core
Secrato combines an EU-focused GRC platform with self-managed infrastructure in Belgium and governance capabilities designed for organisations operating across multiple entities.
For security, compliance and procurement teams assessing data residency and organisational control, those foundations provide clear, verifiable points to evaluate.
Common questions
Where is Secrato's GRC data hosted?
GRC data is processed on self-managed infrastructure in a Belgian datacentre within the EU legal and regulatory environment.
How does Secrato support governance across multiple entities?
Global Governance applies top-level governance decisions across tenants and workspaces and can cascade defined attributes through the organisational hierarchy. Multi-Tenant & Workspace Management structures the entities, workspaces and sub-workspaces within that governed environment.
Does data sovereignty apply across the whole Secrato platform?
The same hosting environment applies to the connected GRC records managed within Secrato, including controls, evidence, policies, procedures, risks, assessments and audits.
Which compliance platforms keep data in the EU?
Several GRC platforms offer EU hosting, but where data is stored, who operates the infrastructure and which law applies differ per vendor. Our comparison of 13 GRC platforms lists the published hosting options for each: EU alternatives to Vanta and Drata.
Put sovereignty requirements against the platform
Data residency, jurisdiction and governance increasingly form part of the security assessment before a GRC platform is selected. Book a demo to review Secrato’s hosting arrangement against the requirements of your organisation.