ISO/IEC 42001

ISO/IEC 42001 compliance your board can account for

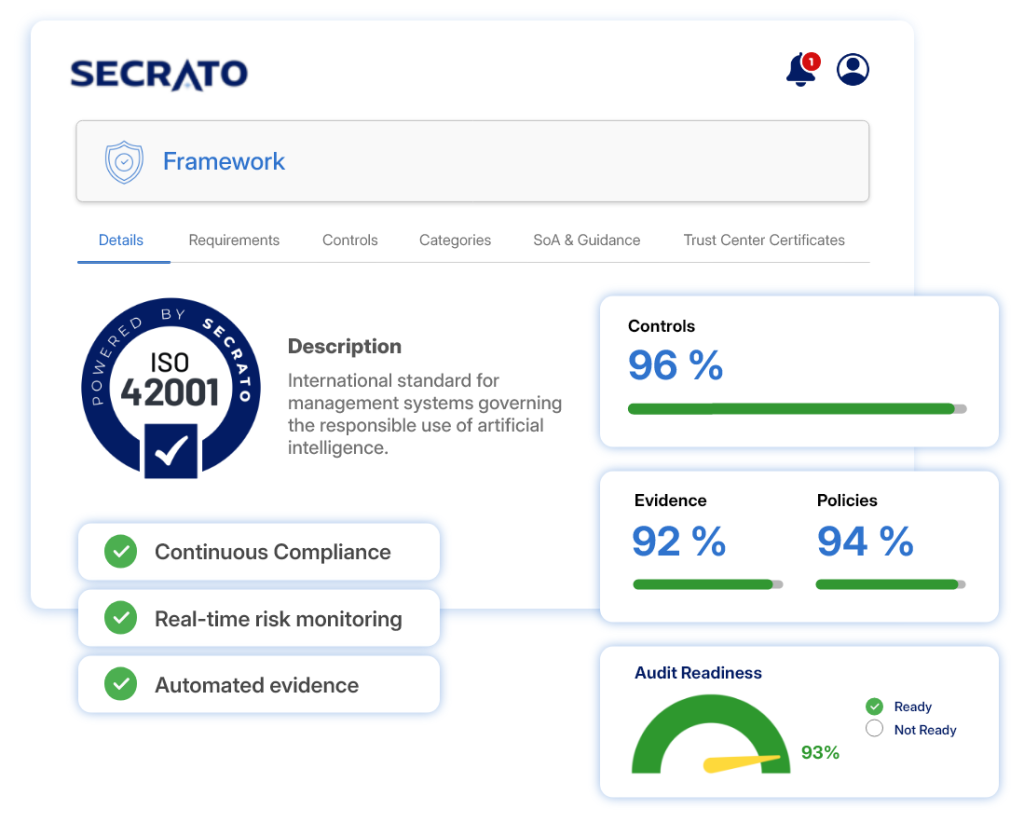
AI governance is now a board-level question and ISO/IEC 42001 answers it with a certifiable management system. Secrato keeps the AI policy, risk and impact assessments, controls and evidence connected to the requirements they answer, so oversight holds as the AI estate grows.

ISO/IEC 42001 compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
RISK MANAGEMENT MEASURES

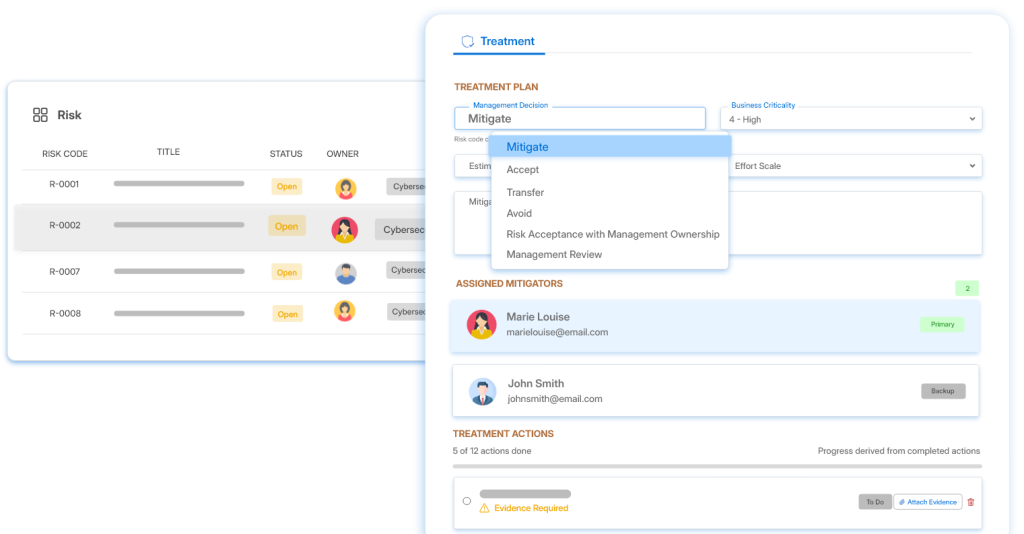
Connect impact and risk to controls

Scope and assess impacts against defined requirements and targets. Tie AI risks to the controls that treat them, with supporting evidence and policies connected to the assessment.

  • Assess AI impacts against defined targets.
  • Link AI risks to the controls that treat them.
  • Connect evidence and policies to assessment
Secrato platform: Treatment plan
Secrato platform: Control connection
AI GOVERNANCE

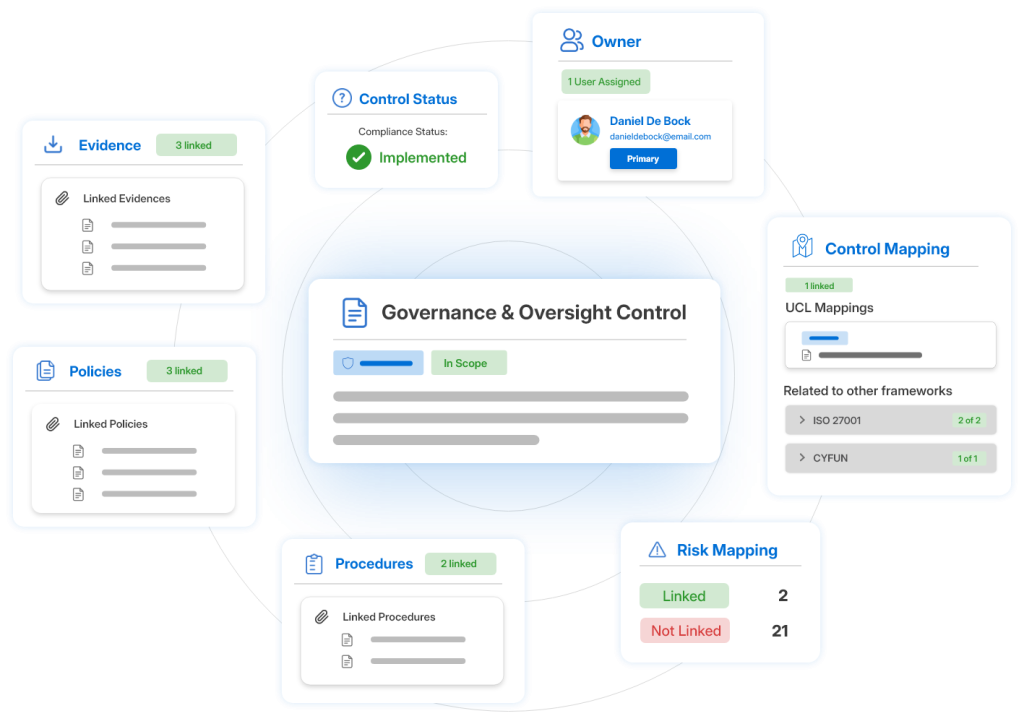
Run the AIMS as a connected system

Maintain each control with its status, evidence, procedures, policies and ownership in one environment. Keep governance records versioned and traceable as changes occur.

  • Keep control status and ownership together.
  • Connect evidence, policies and procedures.
  • Maintain versioned and traceable records.
AI GOVERNANCE

Run the AIMS as a connected system

Maintain each control with its status, evidence, procedures, policies and ownership in one environment. Keep governance records versioned and traceable as changes occur.

  • Keep control status and ownership together.
  • Connect evidence, policies and procedures.
  • Maintain versioned and traceable records.
Secrato platform: Control connection
MANAGEMENT OVERSIGHT

Give top management clear oversight

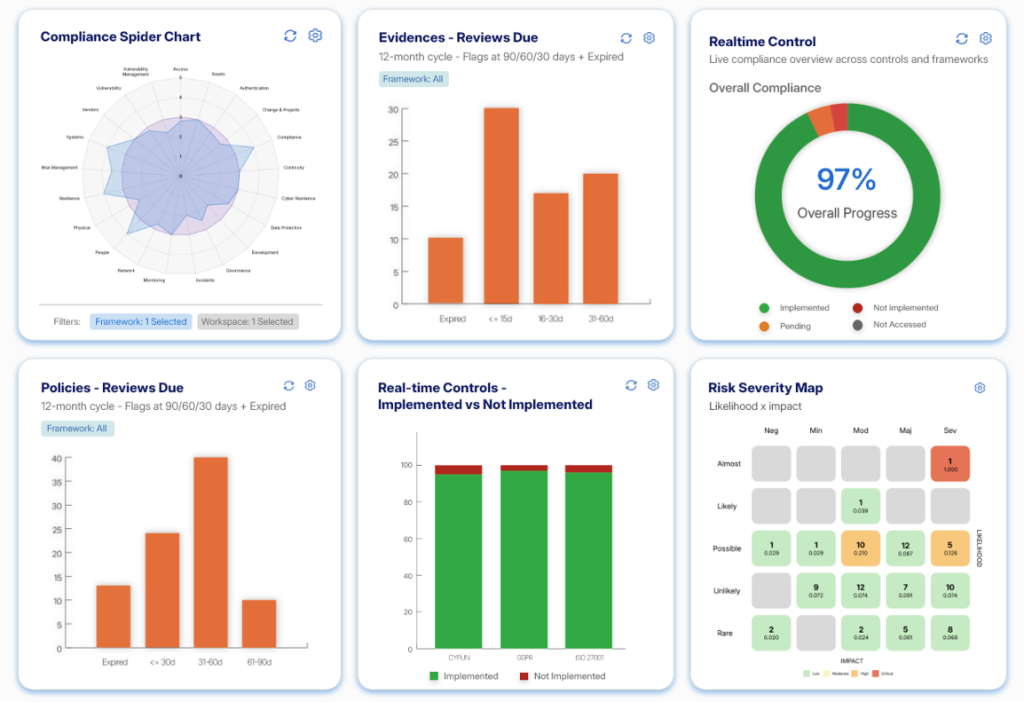
Give leadership visibility into compliance status, risk posture and readiness across the organisation. Apply governance decisions across entities while retaining local responsibilities.

  • Track compliance status and risk posture.
  • Apply governance decisions across entities.
  • Allow local adjustments where needed.
Secrato platform: Dashboard
THE REST OF THE PLATFORM

More ways Secrato supports ISO/IEC 42001

Beyond the core outcomes above, these capabilities support the wider ISO/IEC 42001 programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Collect and reuse supporting records while maintaining their connection to the controls, policies and assessments they substantiate.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured auditor access where appropriate.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Connect controls and requirements across standards and regulations to identify shared coverage and remaining gaps.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

Many controls within an ISO/IEC 42001 AI management system overlap with governance already maintained for other standards. The Unified Control Library maps shared controls across the relevant requirements, reducing duplicated work while keeping AI-specific governance visible.

FAQs for ISO/IEC 42001 compliance software

What is ISO/IEC 42001?

ISO/IEC 42001:2023 specifies requirements for establishing, implementing, maintaining and continually improving an AI management system (AIMS) for organisations developing, providing or using AI systems. It provides a structured management framework and includes an AI-specific Annex A control set; the applicable controls must be considered in the context of the organisation’s AIMS, risk assessment and applicability decisions.

ISO/IEC 42001:2023 applies to organisations of any size, type or nature that provide or use products or services using AI systems. It follows the management-system structure used by standards such as ISO/IEC 27001 and adds an AI-specific control set in Annex A.

Secrato supports ISO/IEC 42001 readiness by connecting AI risks, assessments, controls, policies and evidence, giving teams and management a traceable view of how AI governance is being implemented and maintained.

Bring AI governance into clearer view

As AI use grows, so does the need to understand which risks, assessments, controls and responsibilities sit behind it. See how Secrato can keep your ISO/IEC 42001 management system connected and easier for management to oversee.

Secrato