
Compliance Engine
Manage controls, evidence, policies, procedures, and status across the frameworks you carry from one connected environment. Shared controls let progress carry across overlapping obligations without rebuilding the same work framework by framework.
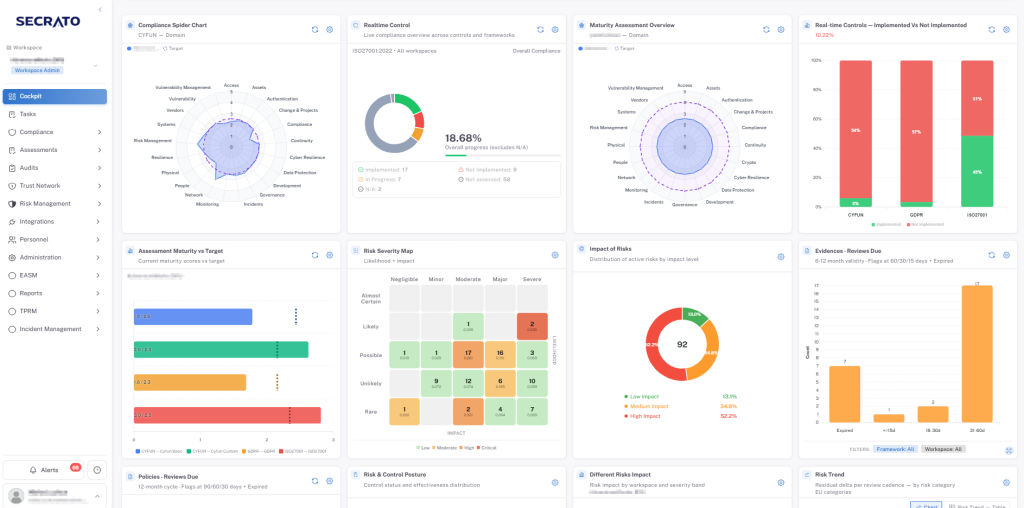
Compliance work scattered across spreadsheets and tools
Compliance work is often spread across spreadsheets, shared drives and separate tools, with each framework managed as another layer of work. Overlapping controls and evidence are handled repeatedly, while teams still have to piece together a current view of where the organisation stands before reviews, audits or management reporting.
Do the work once, apply it wherever it counts
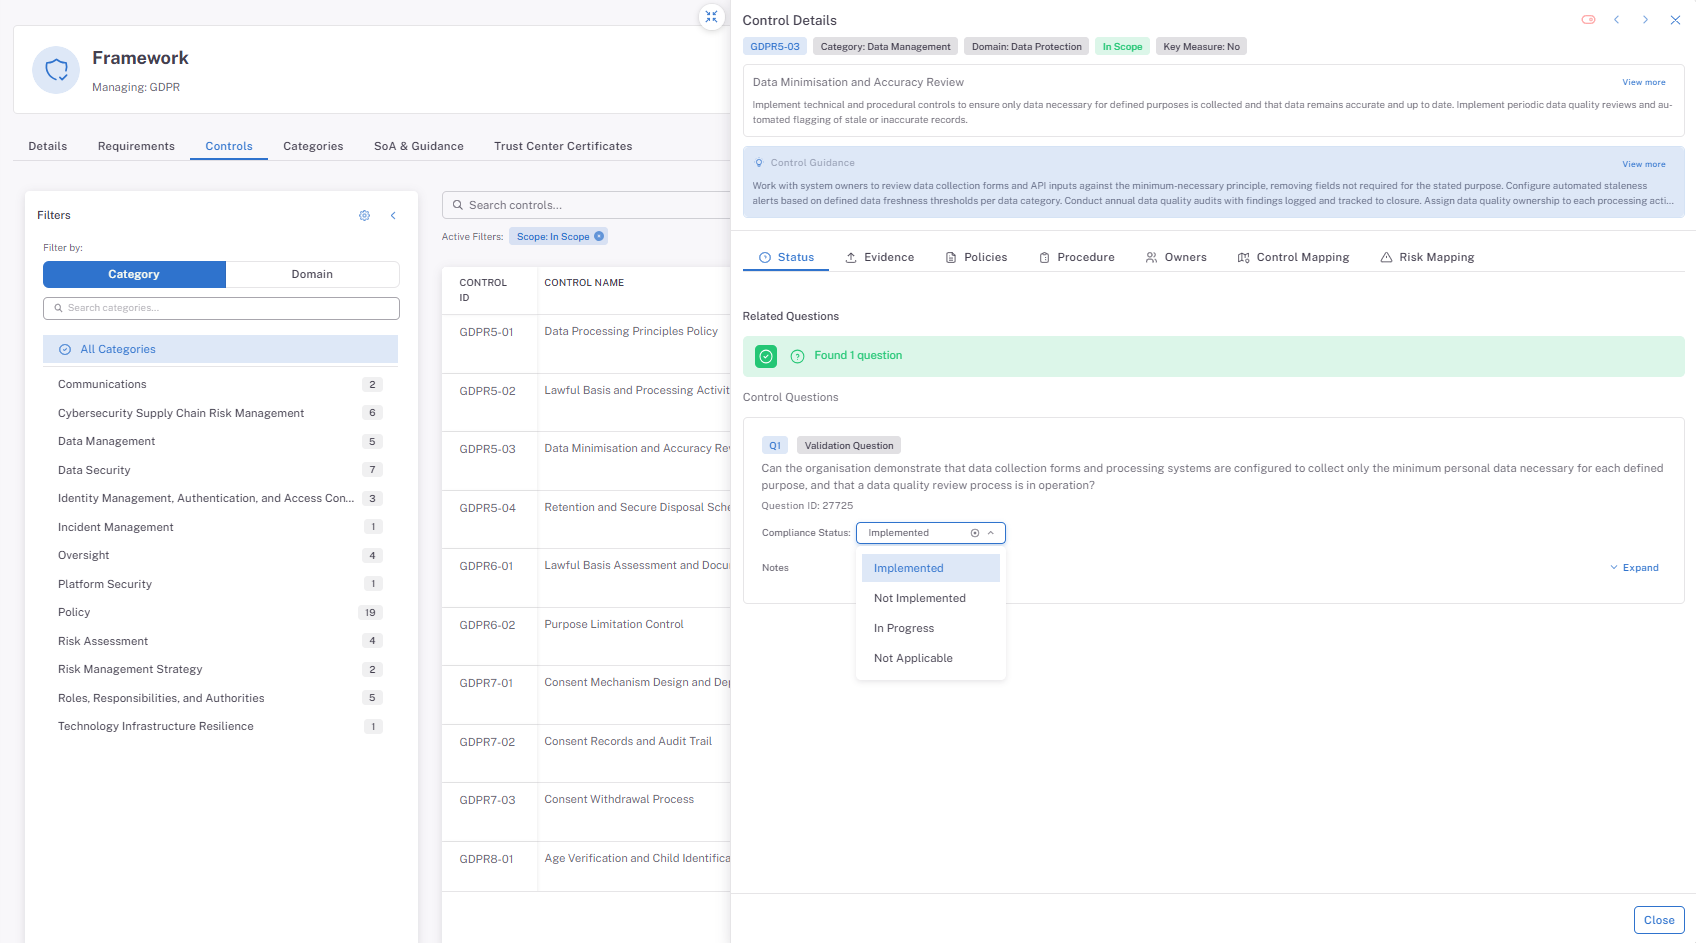
Assess a control once and reuse it across every framework you carry, through the Unified Control Library. This cuts repeated control and evidence work as your compliance programme expands.
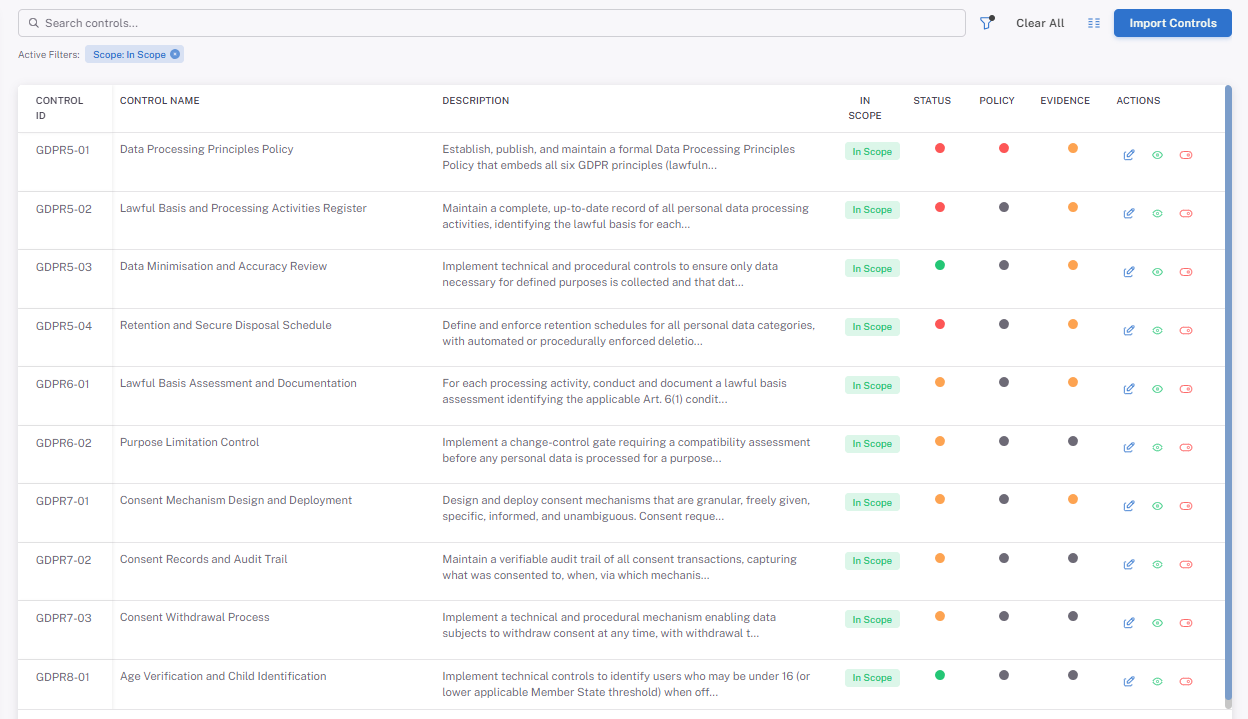
Know where compliance stands now
Track control status as work progresses, so gaps and controls needing attention remain visible between audits. You get a current view of compliance instead of reconstructing it before every review.
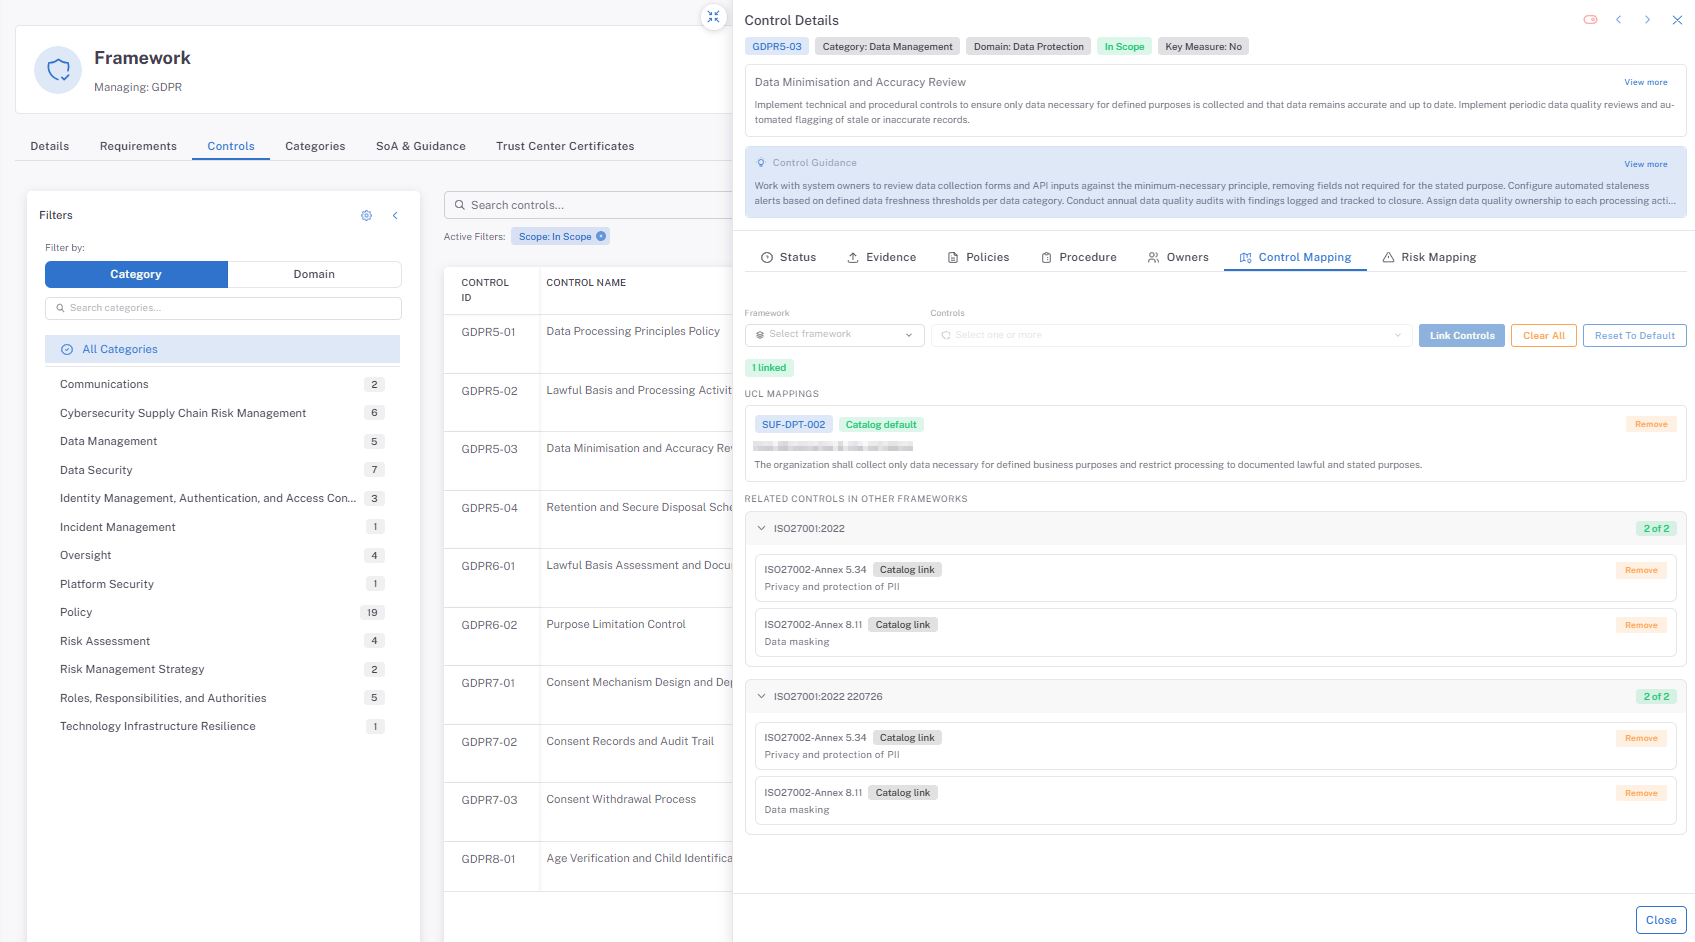
Be ready to explain every control
Keep each control connected to its evidence, policies, procedures, risks, owner and review status. When a control is questioned, the record already shows what supports it, who owns it and when it was last reviewed.
Built into the Compliance Engine
Set a maturity target
A framework can carry a target maturity level, and the controls that fall below it are highlighted for attention.
Set which controls are in scope
Each control can be set in or out of scope, so the working set holds only the controls that apply.
Work from within a control
Create or link evidence, policies, and procedures directly from a control, keeping the proof easy to trace.
Work from shared libraries
Manage controls, evidence, policies and procedures from workspace-wide libraries with ownership, dates and status visible in one central inventory.
Connect compliance to risk
Link controls directly to the risks they treat, so compliance activity can be understood in the context of the exposure it is designed to manage.
Reuse records across shared controls
Map records to Unified Control Library controls using labels, so the same supporting records can serve the frameworks that depend on them.
Compliance work stays connected across Secrato. What changes in one part of the platform remains visible and useful wherever it matters.
Policy & Evidence Management
Keep supporting evidence and policies connected to the controls they substantiate.
Assessments
Evaluate the same controls without rebuilding the compliance picture elsewhere.
Audit Hub
Carry control and evidence readiness into review against the work already maintained.
Dashboards & Reporting
Read compliance status, risk posture and audit readiness from connected records.
Unified Control Library
Use the shared control structure that connects the work across Secrato.
Run more frameworks without multiplying the work
The Compliance Engine supports compliance work across Secrato’s framework coverage, with shared controls mapped through the Unified Control Library. Where obligations overlap, existing control work can support more than one framework instead of being managed again from the beginning.
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Belgium · EU
Common questions
We carry several frameworks. Does the Compliance Engine mean managing each one separately?
Every framework runs against a single set of controls in the Unified Control Library, so a control assessed once evidences the matching requirements across the other frameworks an organisation carries. Overlapping obligations stop generating duplicate work, and taking on another framework draws on control work already recorded.
When an auditor questions a control, what does the Compliance Engine show?
The control’s record. Each control keeps the evidence, policies, procedures and risks behind it, along with its owner and review status, so the record already shows what was done, who owns it, what supports it and when it was last reviewed.
Does Secrato determine whether we are compliant?
Your team remains responsible for scoping and deciding whether requirements and controls are satisfied. Secrato supports that work by keeping the controls, evidence and related compliance records organised, connected and current.
Make compliance easier to carry forward
As frameworks grow and audits return, the work already completed should continue to count. Book a demo to walk through the Compliance Engine with your framework set and your controls.
