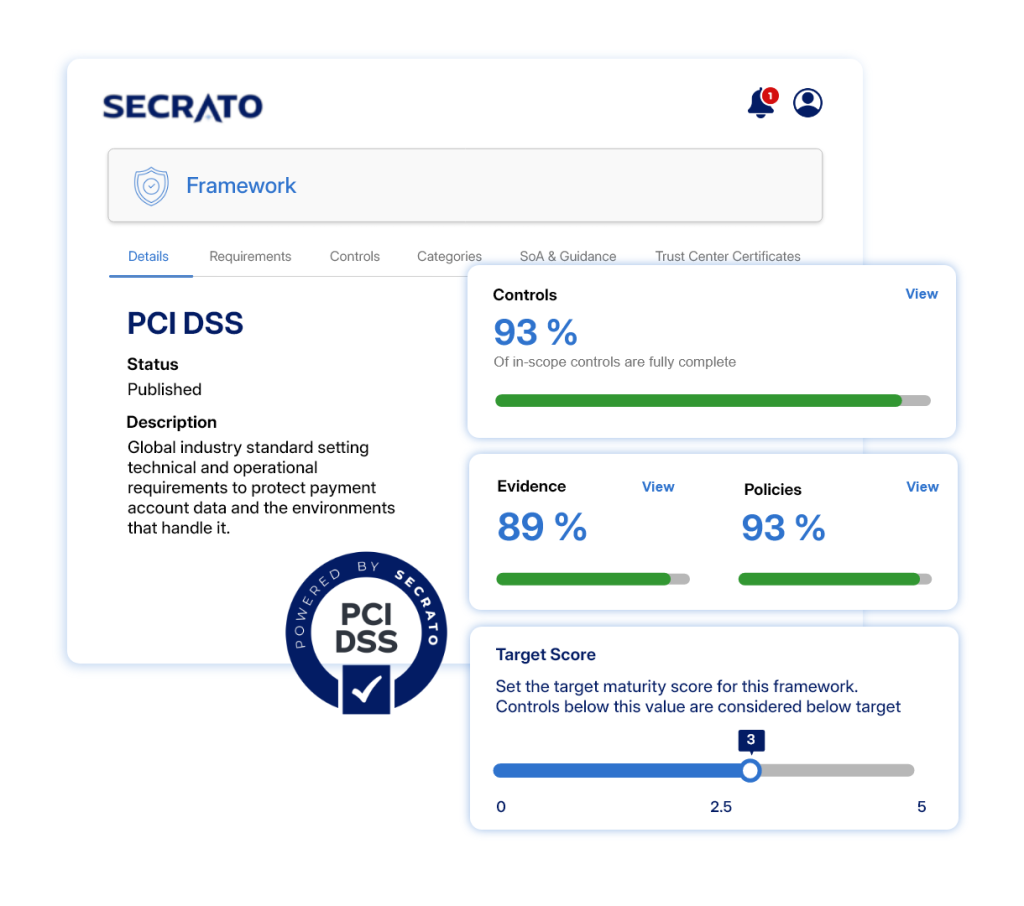
PCI DSS makes you validate cardholder-data protection every year. Secrato keeps the controls, evidence and policies connected to the requirements they satisfy, so the assessment draws on records already in order.
Maintain each PCI DSS requirement with its status, ownership, procedures and supporting mappings. Connect risks identified through targeted risk analysis to the controls used to treat them.
Assess work against the PCI DSS requirements and connect responses directly to supporting evidence. Keep records organised for SAQ or QSA review so validation does not begin with a manual evidence-gathering exercise.
Keep requirements, controls, evidence and status connected throughout the year. Use automated evidence collection and ongoing visibility to see compliance status, risk posture and readiness as the environment changes.
Beyond the core outcomes above, these capabilities support the wider PCI DSS programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Document and review the procedures that support NIS2 controls, policies and risks so implementation is backed by maintained operational detail.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
See where PCI DSS controls overlap with other standards and regulations, helping teams identify shared coverage and remaining gaps.
Cascade top-level decisions through workspaces while allowing approved local variations where necessary.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
Many PCI DSS controls overlap with security work already maintained for other frameworks. The Unified Control Library maps shared controls across the relevant requirements, reducing repeated assessment and evidence work while keeping PCI DSS-specific requirements and validation needs distinct.
Explore the other supported frameworks →
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
PCI DSS is the Payment Card Industry Data Security Standard, setting security requirements for organisations that store, process or transmit cardholder data. Compliance is validated regularly, with the applicable assessment route depending on the organisation’s circumstances. Defining the scope of the cardholder data environment is a fundamental part of that process and remains the organisation’s responsibility.
PCI DSS is intended for entities that store, process or transmit payment-account data, whether those activities are performed directly or through a third-party service provider. Requirements may also apply to entities whose systems or services can affect the security of that data. The applicable validation method depends on the entity’s role, payment environment, and the requirements of the relevant acquirer, payment brand or other compliance-accepting entity; transaction volume may be one factor.
Secrato supports PCI DSS readiness by keeping requirements, controls, policies and evidence connected in a traceable view, making it easier to monitor readiness and maintain the supporting record for recurring validation.
PCI DSS readiness does not start when the next assessment approaches. See how Secrato can keep requirements, controls, evidence and policies connected, giving your team a clearer picture before validation begins.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance