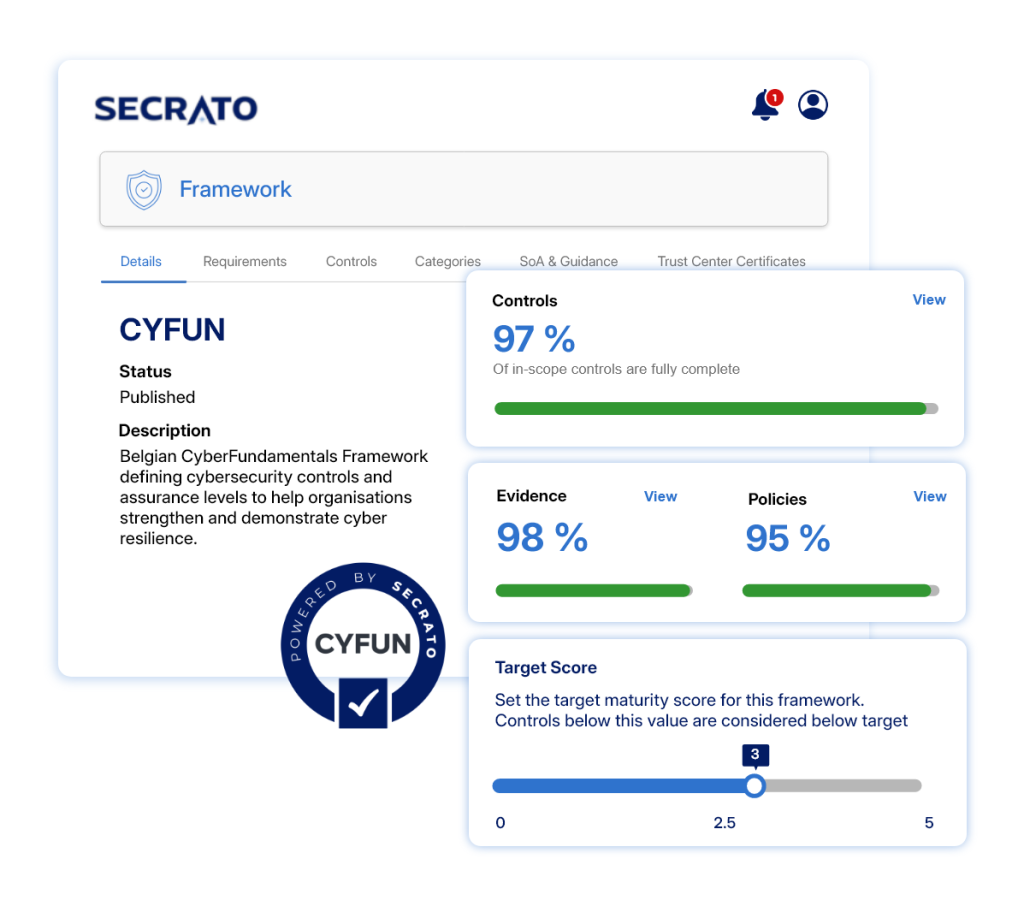
In Belgium, CyFun is the CCB’s recognised route to demonstrating your NIS2 risk-management measures. Secrato keeps the controls, key-measure evidence and self-assessment connected to the level they answer, so readiness holds between assessments.
Set the target maturity for your selected CyFun level and identify controls that fall below it. Connect key measures to their owners, evidence and the risks they address.
Assess controls against the selected level and connect each response to its supporting evidence. Move assessment work through to audit readiness with records organised for the Conformity Assessment Body that performs the verification or certification.
Connect policies, risks, controls and evidence across CyFun’s governance and cybersecurity functions. Maintain visibility across entities with central governance decisions and controlled local deviations.
Beyond the core outcomes above, these capabilities support the wider CyFun programme.
Connect controls and requirements across frameworks to identify shared coverage and reduce duplicated assessment work.
Keep risks connected to the controls and evidence behind their treatment, with visibility into ownership and residual exposure.
Bring evidence together, review control readiness and manage findings, with structured assessor access where appropriate.
Bring compliance status, risk posture, assessment progress and audit readiness into one view.
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
CyFun draws on established sources including ISO/IEC 27001, NIST CSF, CIS Controls and IEC 62443, creating significant opportunities to reuse existing cybersecurity controls. The Unified Control Library maps shared controls across frameworks so teams can see where existing work already contributes to CyFun, while keeping clear that mapping shows correspondence, not equivalence.
Explore the other supported frameworks →
NIS 2
ISO 27001
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
CyFun is the CyberFundamentals Framework published and recommended by the Centre for Cybersecurity Belgium. It is not itself a legal instrument: the obligations come from the Belgian NIS2 framework, while CyFun provides a recognised route for organisations to demonstrate the relevant cybersecurity risk-management measures. Both the 2023 and 2025 versions remain valid until 18 April 2027. For the framework’s scope, assurance levels and verification or certification scheme in full, see the CyFun hub.
CyFun is a CCB-developed framework that organisations can use in the Belgian NIS2 context. The underlying NIS2 legal obligations remain mandatory, the applicable conformity route and any required verification or certification depend on the organisation’s NIS2 status and Belgian implementation rules. CyFun verification or certification may support a presumption of conformity when the relevant assurance level, scope and conformity-assessment conditions are met. It does not replace other NIS2 duties, including incident reporting and management-body responsibilities.
Secrato supports CyFun readiness by connecting assurance-level requirements, controls, key-measure evidence and assessment work, making it easier to monitor maturity and prepare for external verification or certification.
Your selected assurance level creates an ongoing set of measures and assessment work to maintain. See how Secrato can keep that work connected and give your team a clearer view of readiness before and between external assessments.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance