
Risk Management
Manage risks alongside the controls and evidence used to treat them. Ownership, treatment and residual exposure remain visible as the organisation changes, giving you a more defensible view than a register maintained separately from your compliance work.
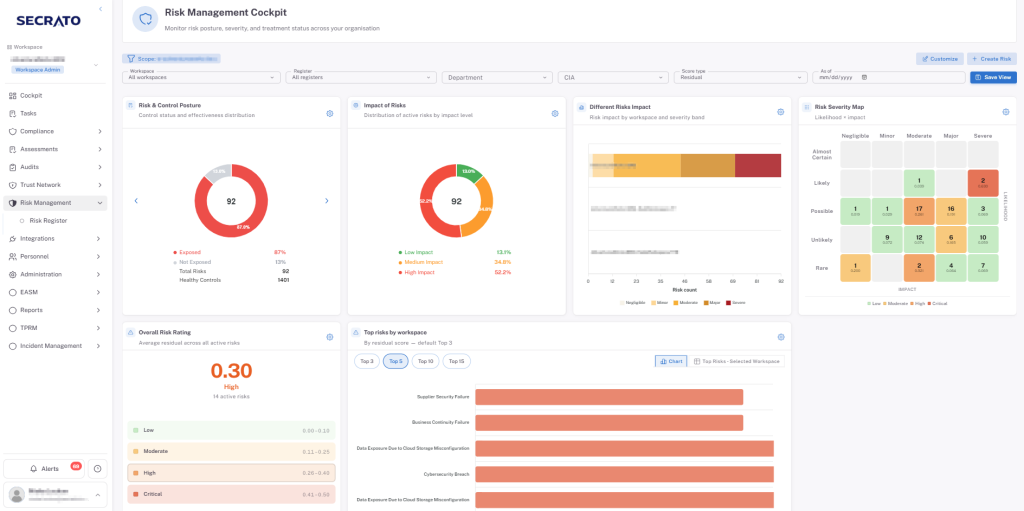
A risk register that drifts from reality
Risk registers are often maintained separately from the controls, assessments and evidence used to manage the risks they contain. As those underlying conditions change, the recorded view of exposure can drift from reality, leaving teams to reconstruct how a risk is being treated when management, auditors or other stakeholders need an answer.
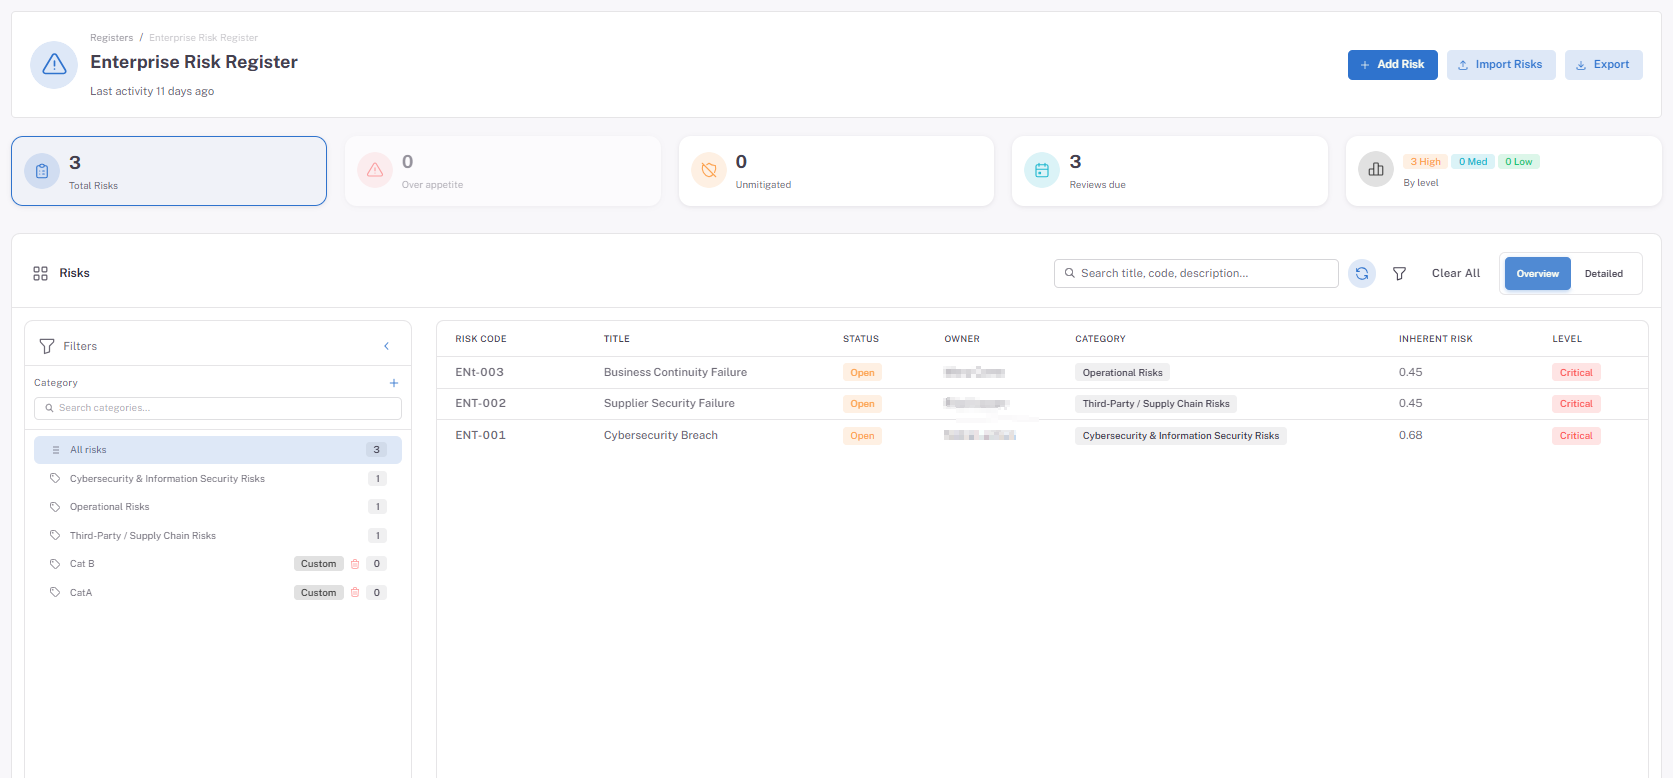
Understand what sits behind every risk
Connect risks to the controls that address them and the evidence that supports those controls. With assessment and audit activity linked as well, your teams gain a clearer view of how risk is being managed instead of relying on a standalone risk register.
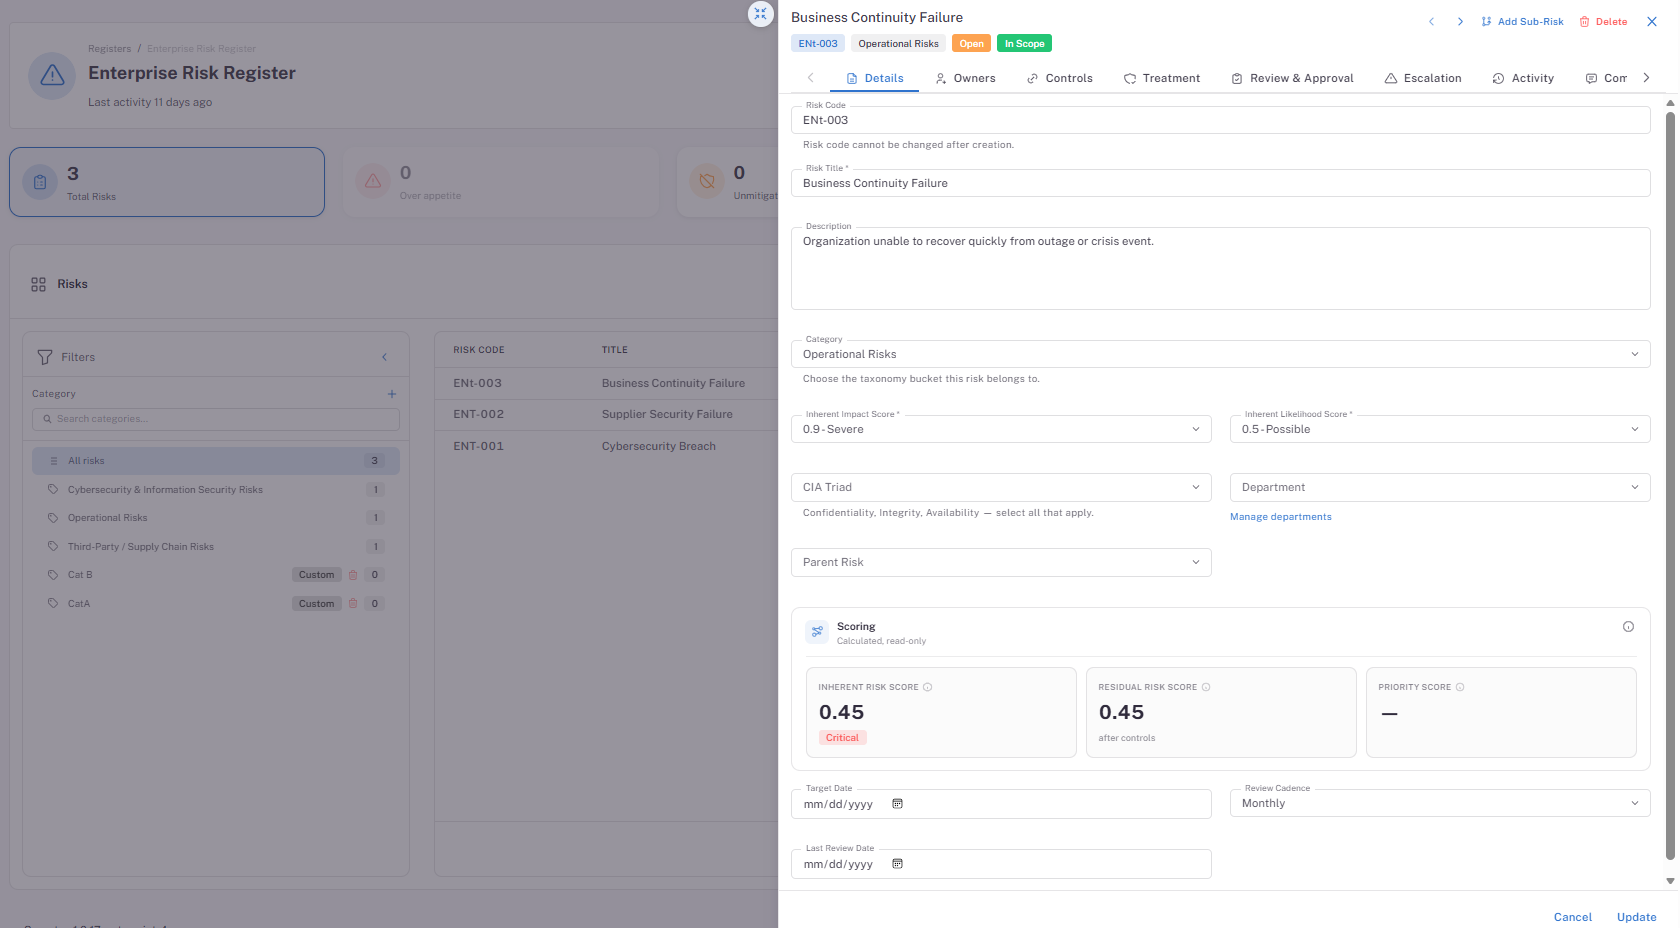
Focus on what matters most
Assess likelihood and impact to understand where exposure is highest and attention is needed most. Inherent and residual risk assessment, together with consistent scoring and visual heatmaps, gives your teams a clearer basis for prioritisation and decision-making.
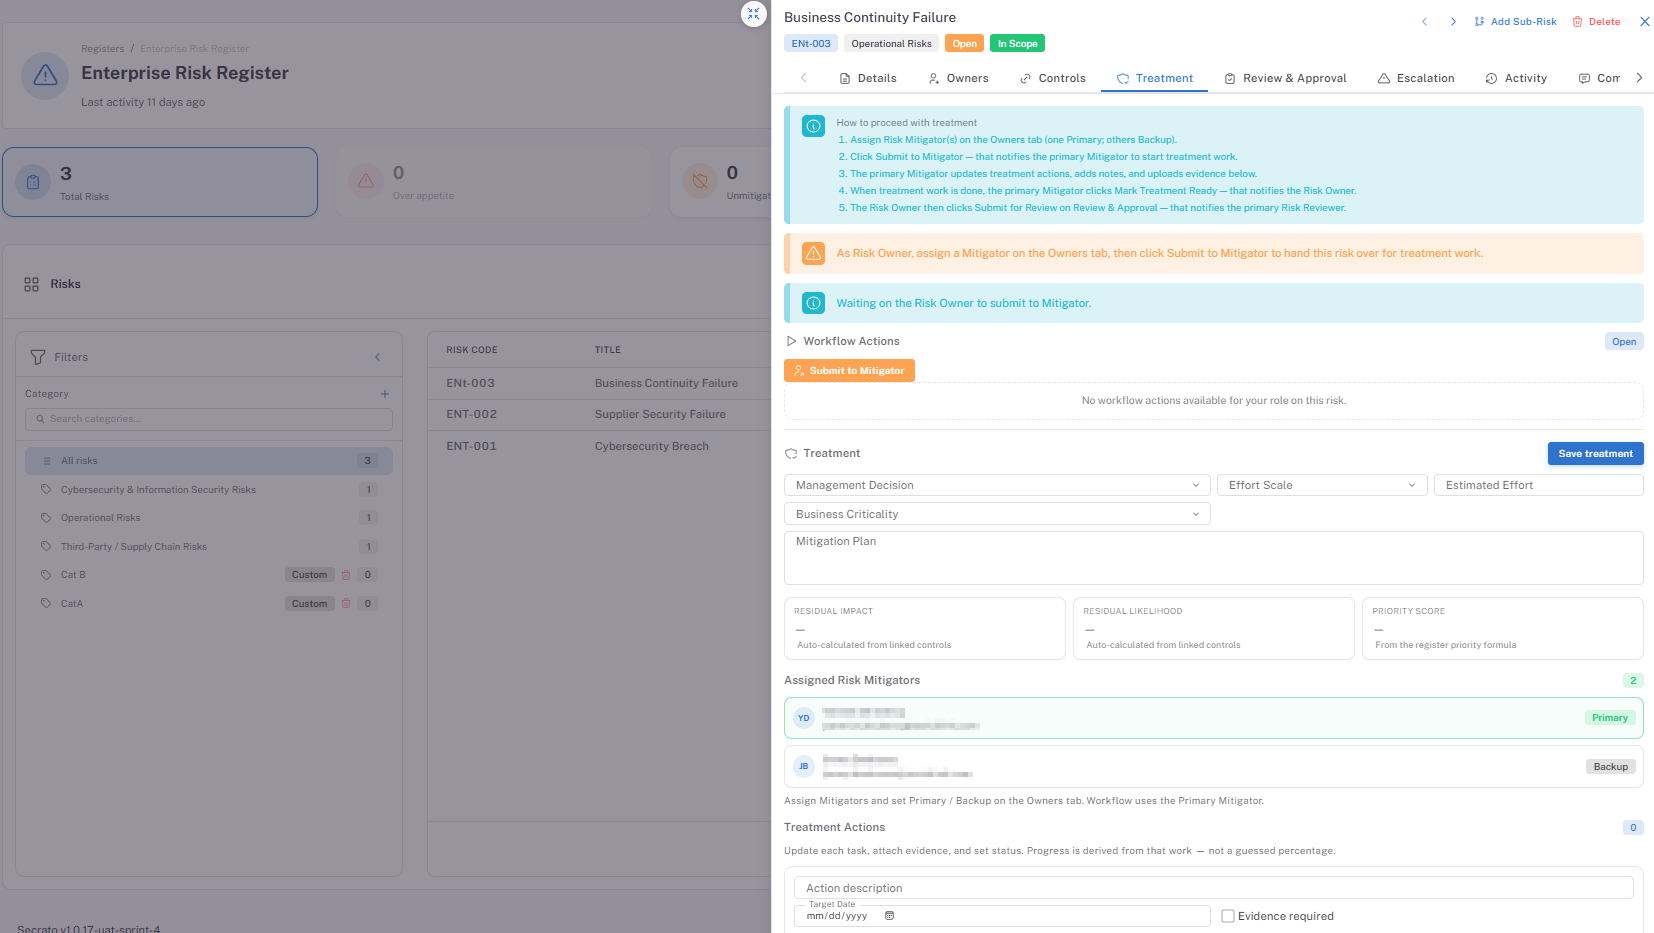
Turn risk insight into action
Manage risk treatment with defined roles, clear accountability and escalation when greater attention is required. By bringing risk information together across the organisation, Secrato gives leadership clearer oversight of exposure and how it is being addressed.
Built into the Risk Management
Create a risk register
Create a register from scratch or start from a predefined sample, with categories to reflect how your organisation groups risk.
Score risk around control effectiveness
Use supported scoring approaches to reflect how effectively controls treat risk and, where configured, the weight of their mitigation.
Keep inherent and residual risk in view
Track inherent and residual risk to help teams understand the exposure that remains and where further attention is needed.
Make risk responsibilities explicit
Assign defined roles across ownership, mitigation, review and escalation so accountability does not stop with a single risk owner.
Manage different types of risk
Bring different risk registers into the same environment, without separating them across disconnected processes.
Configure the register to your risk model
Set risk codes, categories, and likelihood and impact scales to reflect how your organisation structures and assesses risk.
Risk Management stays connected across Secrato. As the picture changes, that context remains visible throughout the wider platform.
Evidence Management
Keep supporting evidence connected to the risk activity behind treatment decisions.
Compliance Engine
Connect risks to the controls used to treat them, grouped by risk register.
Audit Hub
Make risk activity available for review alongside the supporting compliance work.
Connect risk management to the frameworks that depend on it
Risk management is central to several frameworks supported by Secrato, including ISO 27001, NIS2 and DORA. By connecting risks to the same controls used across those frameworks, teams can manage risk activity without creating a separate register or treatment view for every obligation.
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Belgium · EU
Common questions
Can risks stay connected to the controls they relate to?
Yes. Risks and the controls associated with them can be related through the Unified Control Library, keeping risk work connected to the wider governance and compliance context.
Who decides how serious a risk is?
The judgement remains with your team. Secrato provides a consistent way to score and compare risks, but decisions around likelihood, impact and treatment remain with the people responsible for managing them.
Where is our risk data held?
Your GRC data stays in the EU, processed on Secrato-managed infrastructure in a Belgian datacentre and within the EU legal and regulatory environment.
See your risk register connected to your controls
Risks shift as controls and evidence shift. A register that moves with them holds up under review better than one maintained off to the side. Book a demo to walk through Risk Management with your own registers and controls.
