ISO 9001 compliance that holds between surveillance audits
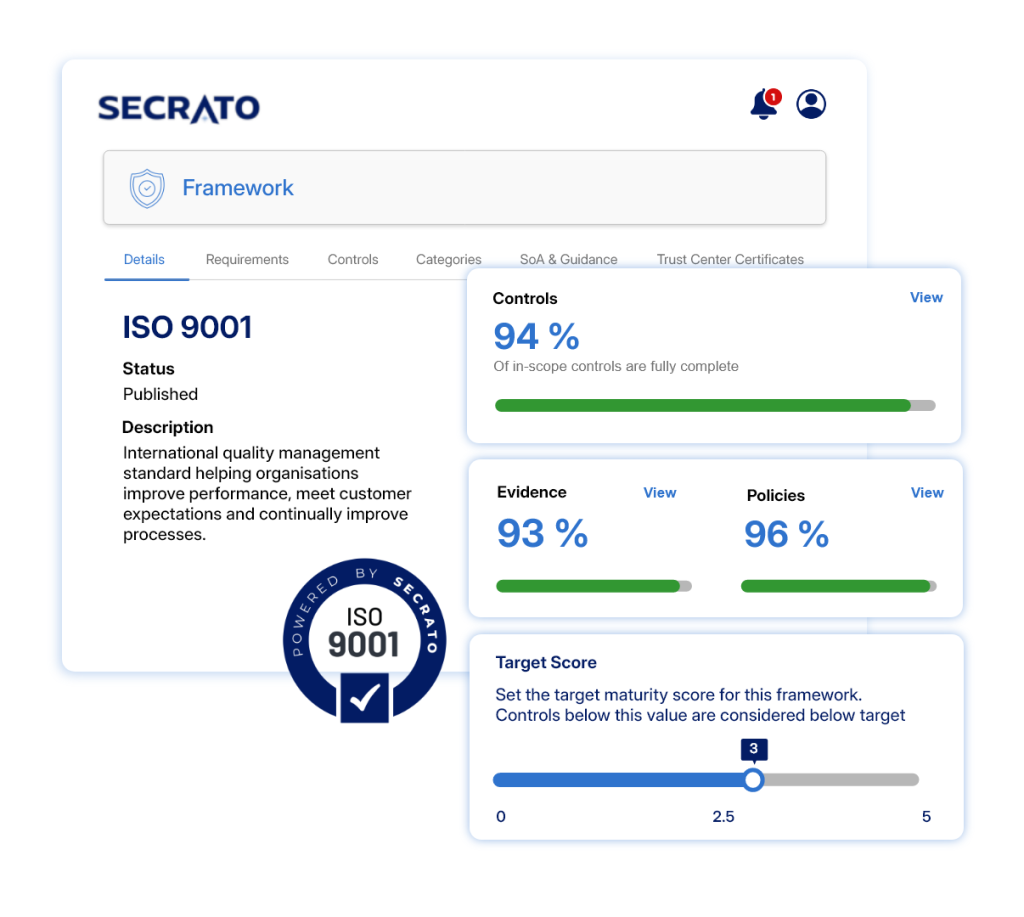
ISO 9001 turns quality into a system you run and evidence continuously. Secrato keeps the documented processes, evidence and reviews connected to the requirements they answer, so a management review works from the current picture.
Keep processes and records together
Maintain processes with their owners, procedures, status and supporting evidence in one environment. Keep policies and procedures versioned, reviewed and governed as the QMS changes.
Connect quality risks to action
Tie quality risks to the controls and processes used to address them, with treatment and residual exposure kept in view. Give teams clearer visibility into where action is required and how risks affect quality objectives.
Bring the current picture to review
Give leadership a current view of QMS status, findings and audit readiness. Assess requirements and organise supporting records so internal audit, management review and certification activity work from the same current information.
More ways Secrato supports ISO 9001
Beyond the core outcomes above, these capabilities support the wider ISO 9001 programme.
Compliance Engine
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Procedure Management
Document and review the procedures that support NIS2 controls, policies and risks so implementation is backed by maintained operational detail.
Assessments
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Global Governance
Cascade group-level decisions across workspaces while supporting approved local deviations where needed.
Framework Mapping
See where ISO 9001 controls and requirements overlap with standards such as ISO 14001 and ISO 27001.
Trust Network
Share relevant security and compliance information with stakeholders through controlled public or gated access.
One control. Multiple frameworks.
ISO management-system standards share common governance requirements, creating opportunities to reuse work across ISO frameworks and other standards. The Unified Control Library maps shared controls across those requirements, so common management-system work can be maintained once while each standard remains independently visible.
Explore the other supported frameworks →
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 14001
BSI
ISO 22301
IEC 62443
+ More and growing
FAQs for ISO 9001 compliance software
What is ISO 9001?
ISO 9001:2015 sets the requirements for a quality management system and can be applied by organisations of any size or sector. Its requirements sit within Clauses 4 to 10 and are built around principles including the process approach, risk-based thinking and continual improvement through the Plan-Do-Check-Act cycle.
Who does ISO 9001 apply to?
Any organisation can implement ISO 9001, regardless of its size or sector and whether it provides products or services. It specifies requirements for a quality management system intended to support consistent fulfilment of customer and applicable statutory and regulatory requirements.
Does Secrato make an organisation ISO 9001 compliant?
No platform issues ISO 9001 certification or makes an organisation conform by itself. Secrato is a platform to centralise policies, controls, evidence, risk and audit workflows, but process design, internal audit, management review and organisational judgement remain with the organisation.
Keep your QMS ready for what comes next
A quality management system should give you a current view of performance and improvement. See how Secrato can keep the processes, evidence and governance behind ISO 9001 connected as your QMS evolves.