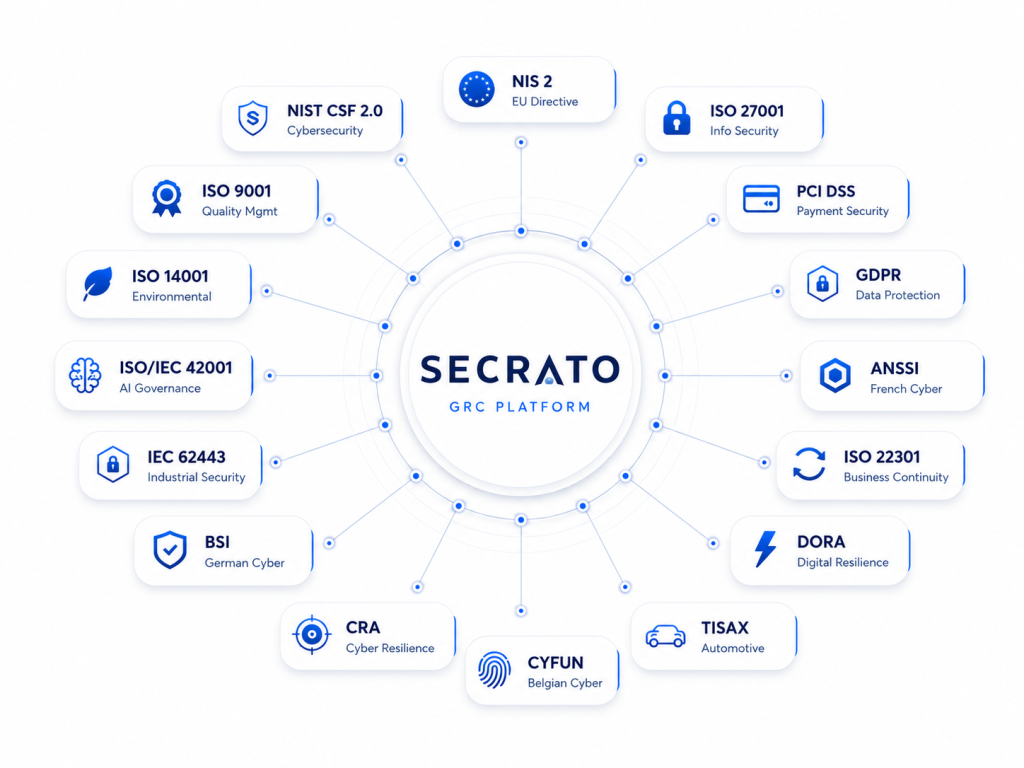
Explore the compliance frameworks Secrato supports—from GDPR, NIS 2 and DORA to ISO 27001—in one connected, EU-first GRC platform.
Secrato is built for European businesses first, delivering seamless compliance coverage for critical EU regulations and global standards.
EU directive setting cybersecurity and incident-reporting obligations for essential and important entities.
EU regulation governing the protection of personal data and privacy for individuals in the EU.
EU regulation setting ICT risk management and resilience requirements for the financial sector.
EU regulation setting cybersecurity requirements for products with digital elements sold in the EU market.
International standard for establishing and maintaining an information security management system.
International standard for management systems governing the responsible use of artificial intelligence.
International standard for business continuity management systems.
Voluntary framework for managing and reducing cybersecurity risk, organised around core functions.
Belgian cybersecurity framework of baseline controls for organisations operating in Belgium.
Reference security requirements and certification schemes set by France’s national cybersecurity agency.
Reference security standards and certification schemes, including IT-Grundschutz, set by Germany’s federal cybersecurity agency.
Information security assessment and exchange standard used across the automotive industry.
Global security standard for organisations handling payment card data.
International standard for security of industrial automation and control systems.
CUSTOM FRAMEWORKS
Combine requirements from any standard framework or your own internal policies into a framework built around your organisation, tracked the same way as everything else in the register.
GRC data is processed on self-managed infrastructure in a Belgian datacentre, within the EU legal and regulatory environment.
Belgium · EU
Secrato covers 16+ frameworks across four groups: EU regulations and directives, international management standards, national and regional schemes, and industry-specific standards. The full set is listed in the register above and new frameworks are added regularly.
You can build it yourself. Alongside the supported frameworks, Secrato lets you compile controls from any standard framework or your own internal policies into a custom framework, tracked the same way as every other entry in the register.
No. When a control satisfies requirements across more than one framework, Secrato maps it once and reuses it everywhere it applies. Mapping a control for NIS2 that also counts toward ISO 27001 means the work carries across without being repeated.
Request a demo and we’ll walk through the frameworks that apply to your organisation, and how Secrato maps them together.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance