IEC 62443 compliance you can show holds up
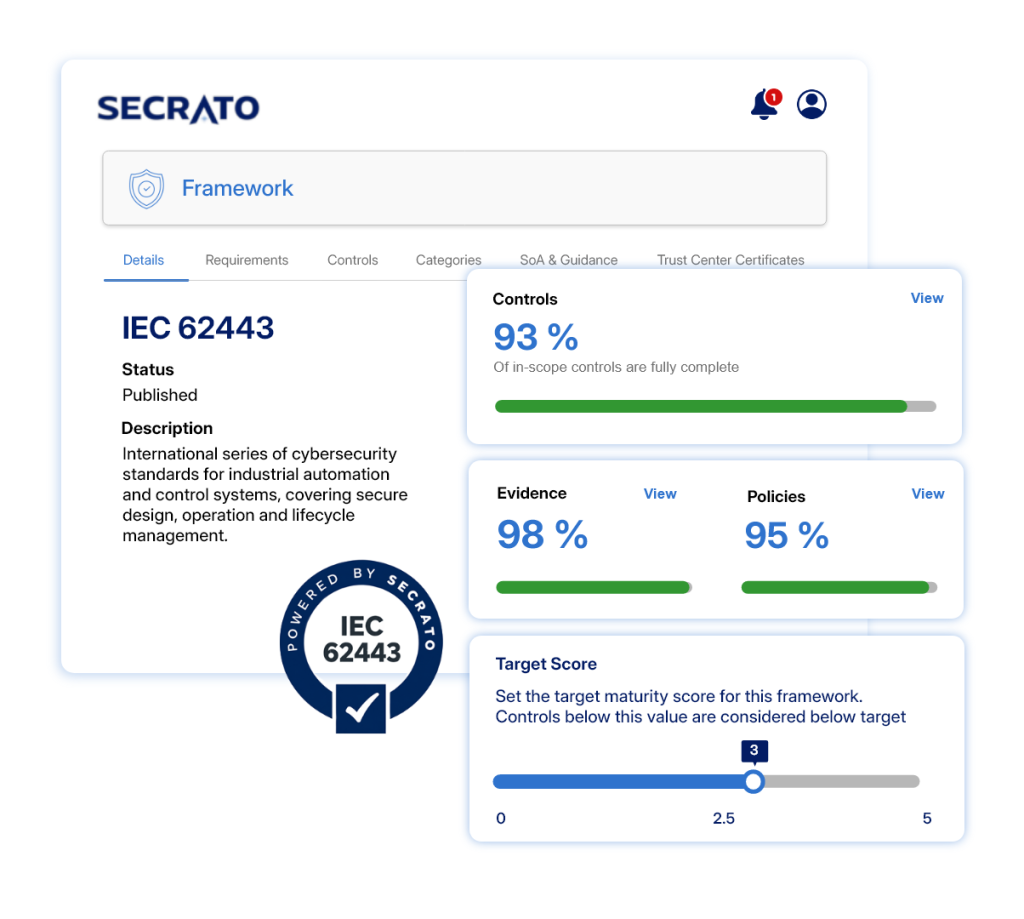
IEC 62443 asks you to prove your control system security holds up, then keep proving it. Secrato connects the controls and evidence to the requirements behind that proof, so the security level you hold stays visible against the one you set.
Connect zone risk to security controls
Tie the risks identified for each zone to the controls used to treat them. Score controls against the target security level and keep gaps visible across the foundational requirements.
Keep conformance evidence organised
Assess requirements and connect every response to the evidence that supports it. Maintain records against their controls so supporting information is already organised when a conformance review takes place.
Each party's responsibility, documented and reviewable
Connect policies, procedures, controls and evidence with clear ownership and review cycles. Maintain a shared view of readiness across asset owners, integrators, suppliers and other parties with defined lifecycle responsibilities.
More ways Secrato supports IEC 62443
Beyond the core outcomes above, these capabilities support the wider IEC 62443 programme.
Compliance Engine
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Audit Hub
Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.
Assessments
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Global Governance
Cascade group-level decisions across workspaces while supporting approved local deviations where needed.
API and integrations
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Trust Network
Share relevant security and compliance information with stakeholders through controlled public or gated access.
One control. Multiple frameworks.
Many IEC 62443 security measures overlap with controls already maintained in other cybersecurity frameworks. The Unified Control Library maps that shared control work across the relevant requirements, reducing duplication while keeping industrial-specific requirements such as zones, conduits and security levels clearly identifiable.
Explore the other supported frameworks →
NIS 2
ISO 27001
CYFUN
GDPR
DORA
EU CRA
NIST CSF 2.0
PCI DSS
TISAX
ISO/IEC 42001
ANSSI
ISO 9001
ISO 14001
BSI
ISO 22301
+ More and growing
FAQs for IEC 62443 compliance software
What is IEC 62443?
IEC 62443 is the international series of standards for securing industrial automation and control systems across their lifecycle, with responsibilities spanning asset owners, system integrators and product suppliers. IEC 62443 is voluntary rather than a law with a single compliance deadline, and adoption is commonly driven by procurement, contracts or sector requirements. The individual standards contain the detailed requirements for areas such as zones and conduits, security levels and lifecycle responsibilities.
Who does IEC 62443 apply to?
IEC 62443 addresses shared cybersecurity responsibilities across IACS asset owners, automation product suppliers, system integrators and service suppliers.
How does Secrato support IEC 62443?
Secrato supports the governance and evidence work around IEC 62443 by connecting controls, policies, risks and supporting evidence, giving organisations a clearer view of how requirements and responsibilities are being managed.
Keep security governance connected
IEC 62443 responsibilities span systems, sites and lifecycle roles, making visibility difficult when the supporting work is fragmented. See how Secrato can bring controls, risks, evidence and governance records together so readiness is easier to demonstrate.