





BSI IT-GRUNDSCHUTZ

BSI IT-Grundschutz compliance, every module requirement in one place

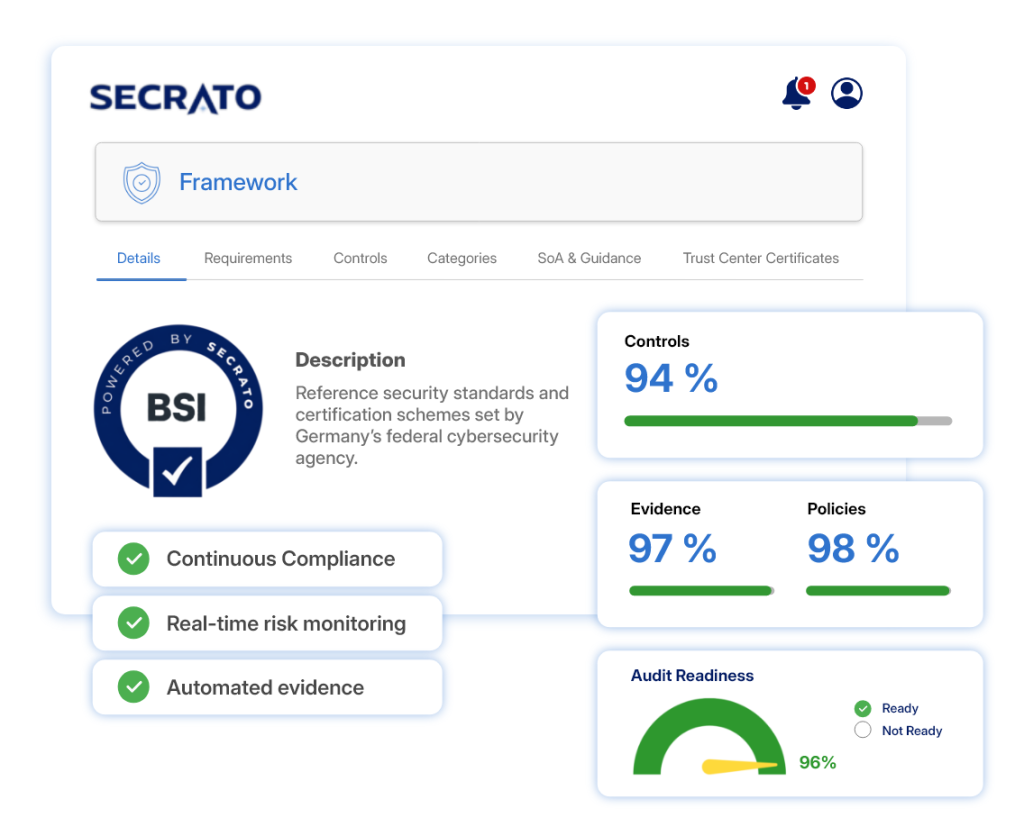
Secrato organises the governance work behind BSI IT-Grundschutz, giving teams a traceable view of implementation, gaps and readiness as the ISMS and its safeguards evolve.

BSI IT-Grundschutz compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
REQUIREMENT MANAGEMENT

Track every requirement clearly

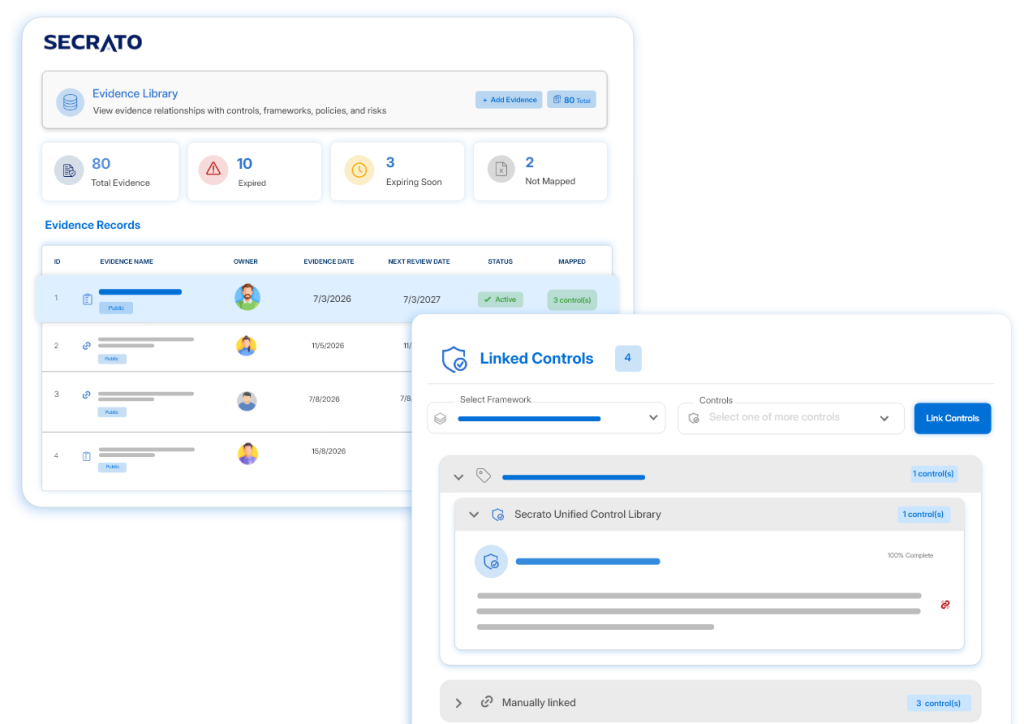
Maintain each module requirement with its status, owner, procedures and supporting evidence. Bring controls, policies and evidence into shared libraries so teams can see what is implemented and what needs attention.

  • Track requirement status and ownership.
  • Connect procedures and supporting evidence.
  • Show what is implemented and needs attention.
Secrato platform: Evidence library
Secrato platform: Findings
INCIDENT REPORTING

Connect risk decisions to controls

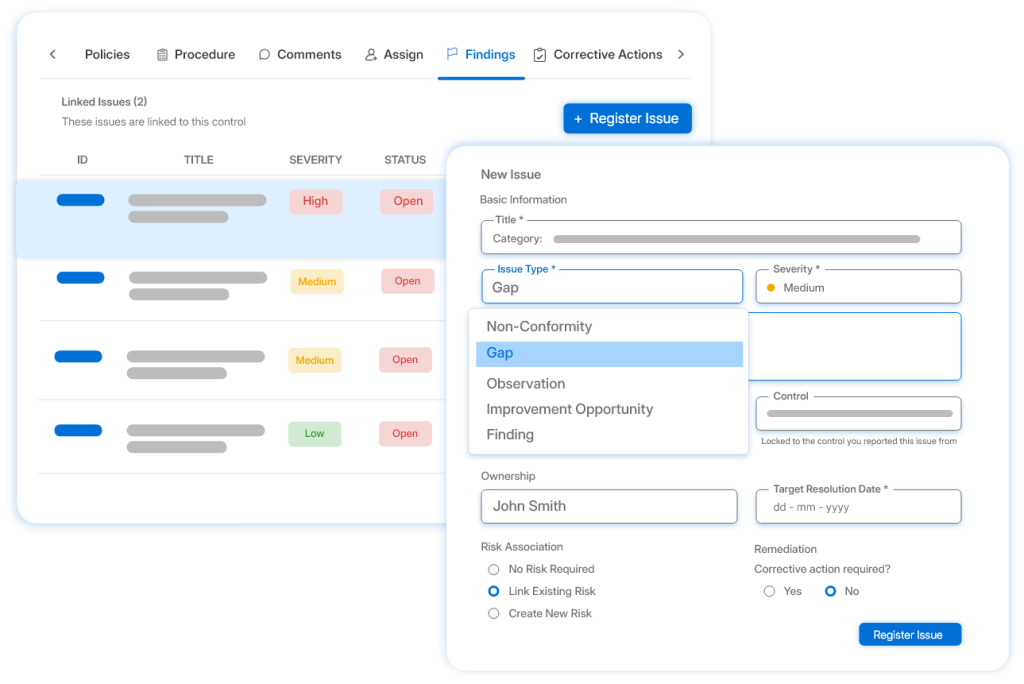
Tie identified risks and protection needs to the controls used to address them. Keep the reasoning, policies and supporting evidence connected so teams can follow how risk is being managed.

  • Link identified risks to supporting controls.

  • Connect policies and supporting evidence.

  • Keep risk decisions visible and traceable.

Secrato platform: Findings
GOVERNANCE & ACCOUNTABILITY

Build a system reviewers can follow

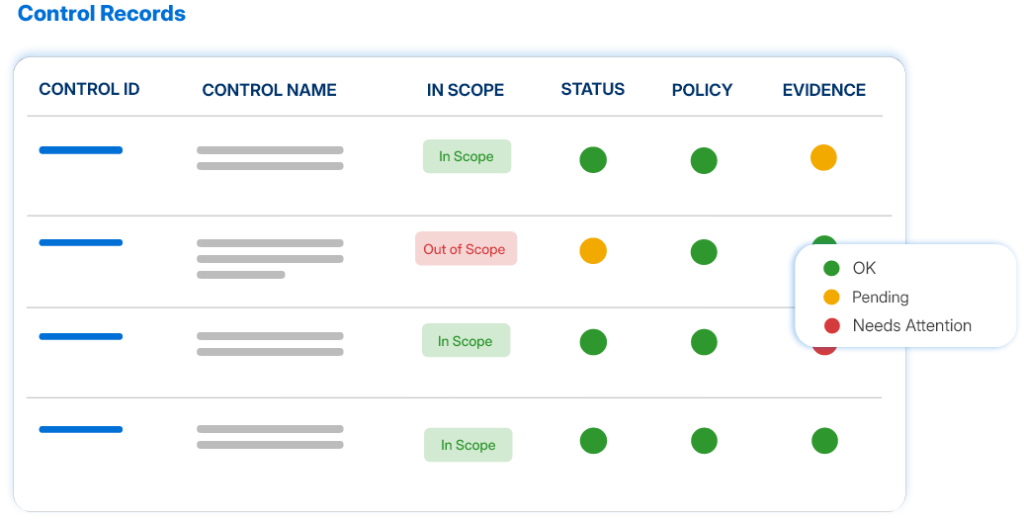
Organise compliance status, evidence and findings into a traceable view of readiness. Keep records current and structured so reviewers can follow how the documented security concept is supported.

  • Keep compliance status and findings traceable.
  • Maintain current and structured records.
  • Support a clear reviewer trail.
Secrato platform: Control records table
THE REST OF THE PLATFORM

More ways Secrato supports BSI IT-Grundschutz

Beyond the core outcomes above, these capabilities support the wider IT-Grundschutz programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Connect policies with the controls, risks, evidence and audits they support while maintaining ownership, review cycles and version history.

Structure and assign assessment work against requirements or controls, with responses linked to the records supporting them.

Keep risks tied to the controls and evidence behind their treatment, with visibility into ownership, status and residual exposure.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

See where IT-Grundschutz requirements overlap with other standards and regulations, helping teams identify shared coverage and remaining gaps.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

IT-Grundschutz is designed to be compatible with ISO/IEC 27001, so much of its security control work can overlap with other cybersecurity frameworks. The Unified Control Library maps shared controls across the relevant requirements, allowing existing implementation and evidence to be reused while keeping IT-Grundschutz-specific requirements visible.

FAQs for BSI IT-Grundschutz compliance software

What is BSI IT-Grundschutz?

BSI IT-Grundschutz is the Federal Office for Information Security’s methodology for building and maintaining an information security management system, supported by the BSI Standards and IT-Grundschutz Compendium. 

BSI IT-Grundschutz can be used by public authorities, companies and other organisations of any size or sector. It is particularly relevant to organisations operating in Germany or those that choose the IT-Grundschutz methodology to structure their ISMS and pursue ISO/IEC 27001 certification on the basis of IT-Grundschutz.

Secrato connects BSI IT-Grundschutz requirements with the controls, risks, policies, evidence and assessments behind them. This gives teams a clearer view of implementation, gaps and readiness while keeping the supporting GRC work structured and traceable as the ISMS evolves.

See where your IT-Grundschutz readiness stands

See how Secrato can keep IT-Grundschutz requirements, evidence and governance records connected as your information security programme evolves.

Secrato