






CMMC

CMMC compliance you can affirm with confidence

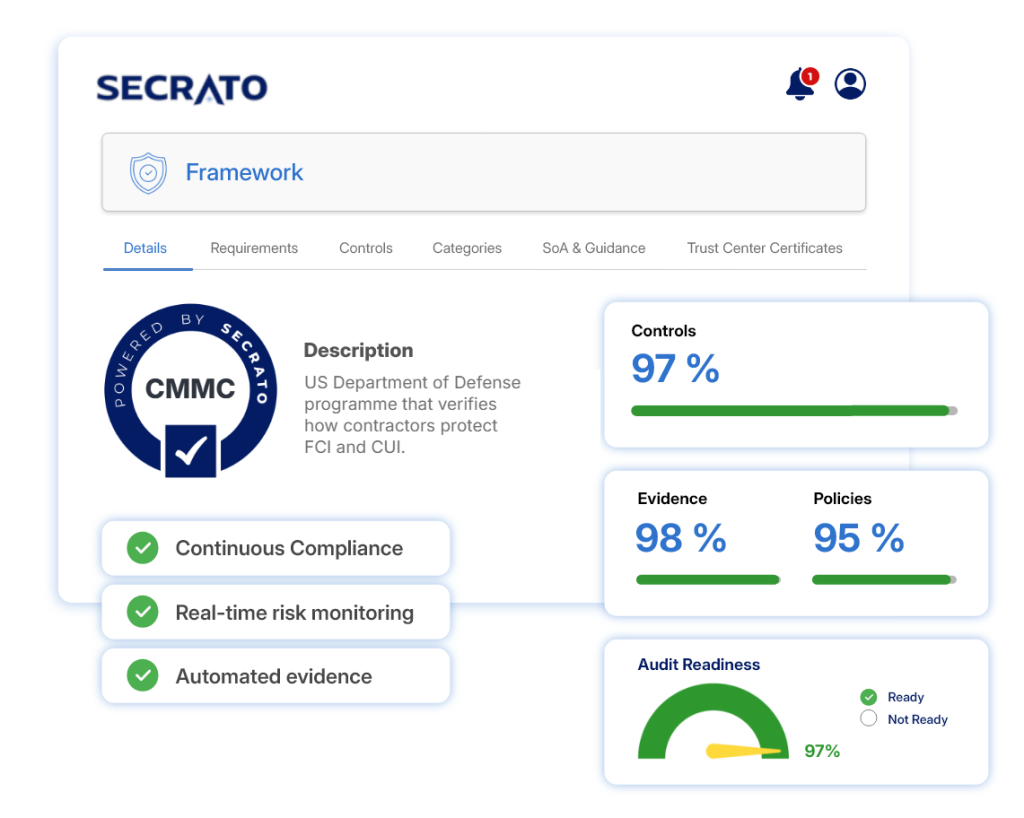
The Cybersecurity Maturity Model Certification (CMMC) Program is how the US Department of Defense checks that contractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). Secrato keeps your requirements, assessment results and evidence connected, so your SPRS score and annual affirmation rest on proof.

In short: Secrato helps defence suppliers prepare for CMMC. Establish whether you handle FCI or CUI and which level your contracts require, implement the 15 Level 1 requirements or the 110 requirements of NIST SP 800-171 Rev. 2 for Level 2, keep your System Security Plan and plan of action current, post your results in SPRS and support the annual affirmation by a senior official.

CMMC compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
REQUIREMENTS

Map every requirement to an owner and evidence

Break your CMMC level down into requirements and assessment objectives, then connect each one to controls, owners, policies and evidence. See what is met, what is not met yet and what belongs in your plan of action.

  • Track the Level 1 and Level 2 requirements.
  • Link assessment objectives to evidence.
  • Keep the System Security Plan current.
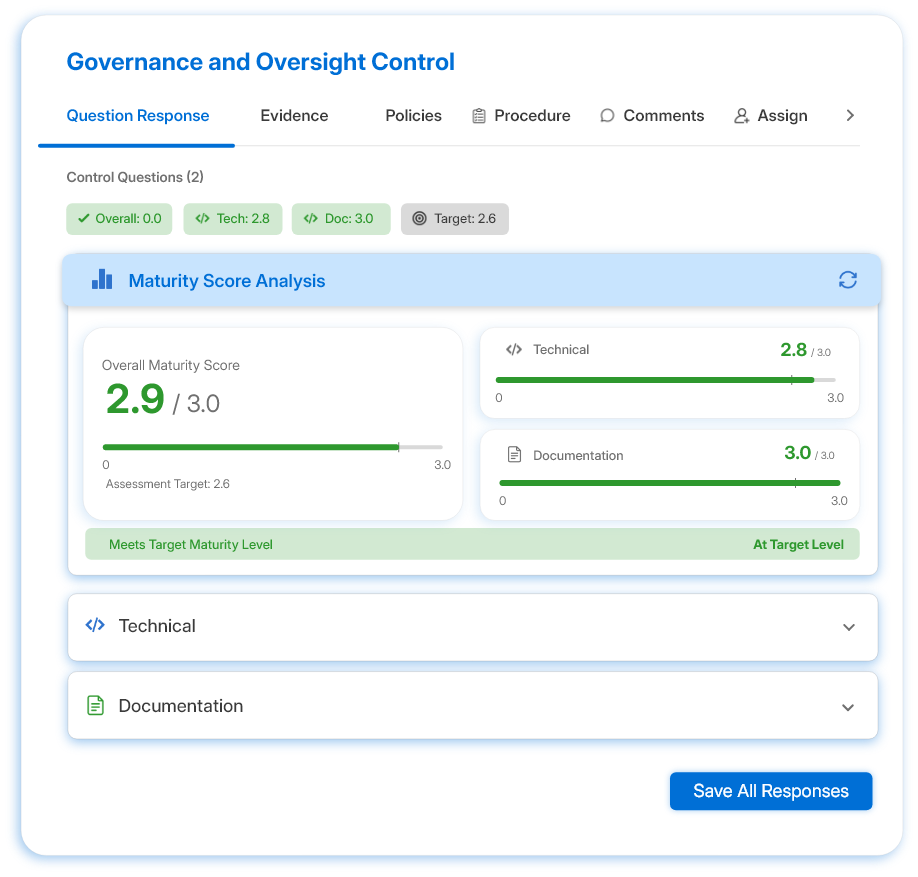
Secrato platform: Maturity score
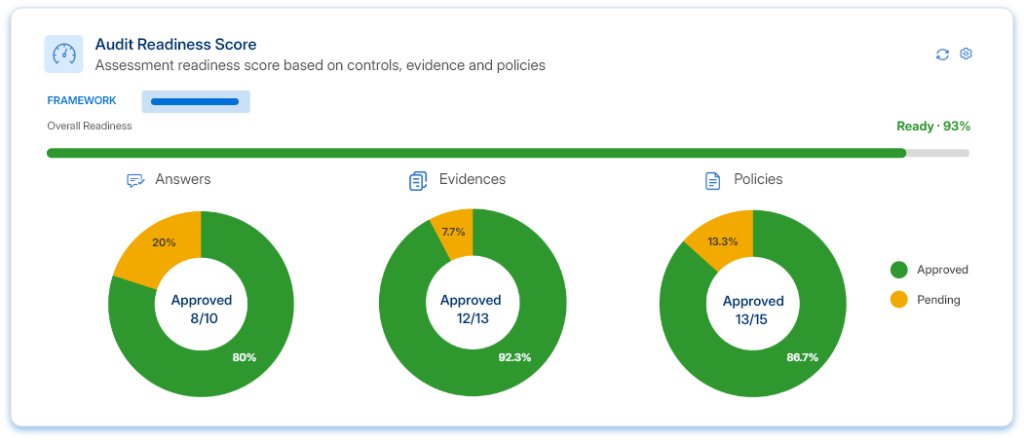
Secrato platform: Audit readiness score
SELF-ASSESSMENT

Score your assessment the way an assessor would

Assess each requirement against its objectives, calculate your score and keep the result ready for SPRS. Track open items in a plan of action with owners and deadlines, so a conditional status does not turn into a lost contract.

  • Mark requirements as met, not met or not applicable.
  • Track POA&M items and the 180-day closeout.
  • Keep a record of what was posted to SPRS and when.
Secrato platform: Audit readiness score
AFFIRMATION

Give the affirming official proof, not promises

Every CMMC status must be affirmed in SPRS by a senior company official, and again each year. Give that official a current view of requirements, open actions and evidence, and keep a record of every affirmation and the suppliers it depends on.

  • Show requirement status and open actions.
  • Record each affirmation and its date.
  • Track the CMMC level of subcontractors.
Secrato platform: Control connection
THE REST OF THE PLATFORM

More ways Secrato supports CMMC

Beyond the core outcomes above, these capabilities support the wider CMMC programme.

Connect controls and requirements across frameworks to identify shared coverage and reduce duplicated assessment work.

Keep risks connected to the controls and evidence behind their treatment, with visibility into ownership and residual exposure.

Bring evidence together, review control readiness and manage findings, with structured assessor access where appropriate.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

CMMC Level 2 is built on NIST SP 800-171, which shares much of its ground with ISO/IEC 27001 and NIST CSF 2.0, creating opportunities to reuse existing cybersecurity controls. The Unified Control Library maps shared controls across frameworks so teams can see where existing work already contributes to CMMC, while keeping clear that mapping shows correspondence, not equivalence.

FAQs for CMMC compliance software

What is CMMC?

The Cybersecurity Maturity Model Certification (CMMC) Program, set out in 32 CFR Part 170, is how the US Department of Defense verifies that contractors and subcontractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). Contracts set the required level through DFARS clause 252.204-7021, and a current status must be recorded in the Supplier Performance Risk System (SPRS).

Level 1 covers FCI with 15 basic safeguarding requirements and an annual self-assessment. Level 2 covers CUI with the 110 requirements of NIST SP 800-171 Rev. 2, assessed every three years by the contractor itself or by a certified third-party assessment organisation (C3PAO). Level 3 adds 24 requirements from NIST SP 800-172 and is assessed by the government (DIBCAC). Every level needs an annual affirmation by a senior official.

Secrato maps CMMC requirements and assessment objectives to controls, owners and evidence, keeps the System Security Plan and plan of action connected to them, and gives the affirming official a current view of the score, open actions and supporting records. Work you already did for ISO/IEC 27001 or NIST CSF 2.0 counts where controls correspond.

The CMMC Program rule took effect on 16 December 2024, and phase 1 of the rollout started on 10 November 2025 with Level 1 and Level 2 self-assessments in new contracts. In July 2026 the Department suspended phase 2, which would have required Level 2 certification by a C3PAO from 10 November 2026, pending a review. Self-assessments, SPRS scores and annual affirmations still apply, and existing certificates remain valid.

Keep CMMC readiness moving with you

CMMC is not a one-off project: requirements, assessments, plans of action and affirmations keep moving. See how Secrato keeps that work connected and gives your team a clear view of readiness before a contracting officer asks.

Secrato