






SOC 2

SOC 2® readiness your auditor can follow

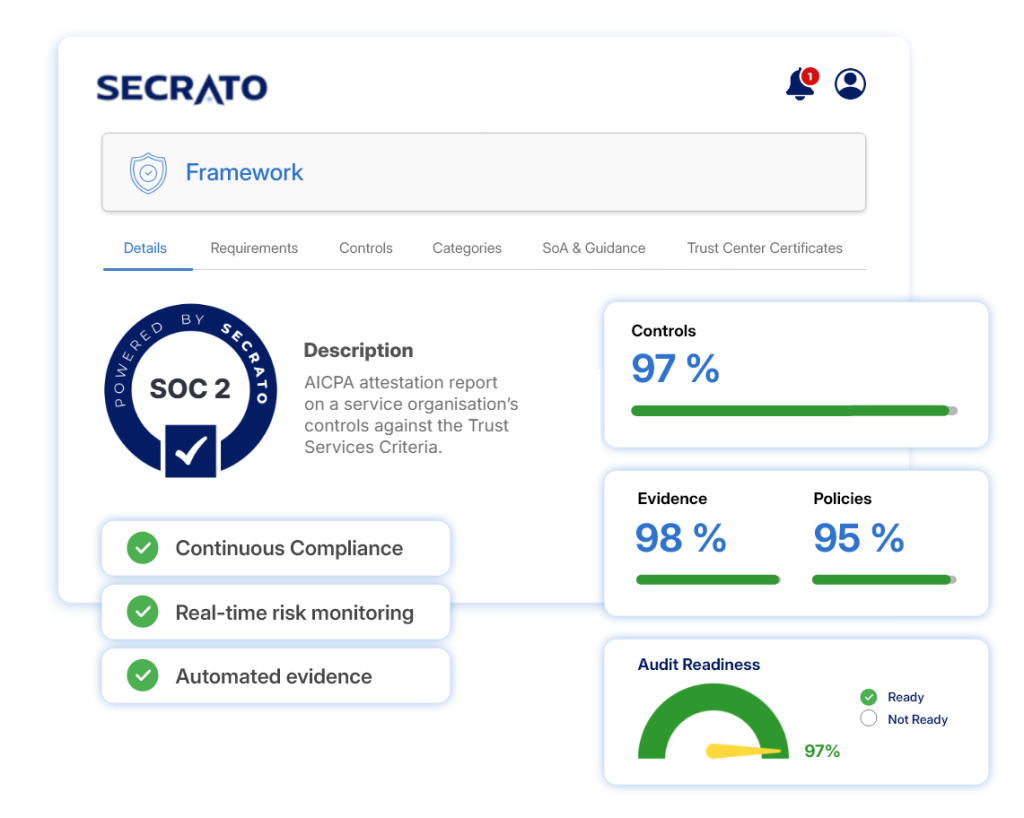
A SOC 2® examination reports on how a service organisation’s controls meet the AICPA Trust Services Criteria for security, availability, processing integrity, confidentiality and privacy. Secrato keeps your controls, owners and evidence connected to each criterion, so Type 1 and Type 2 reports are built from records, not from a last-minute scramble.

In short: Secrato helps service organisations prepare for SOC 2. Choose the Trust Services Categories in scope, with security always included, map the criteria and points of focus to your controls, collect evidence across the observation period for a Type 2 report, and keep the system description, exceptions and auditor requests ready for your CPA firm.

SOC 2 compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
TRUST SERVICES CRITERIA

Map every criterion to the controls that meet it

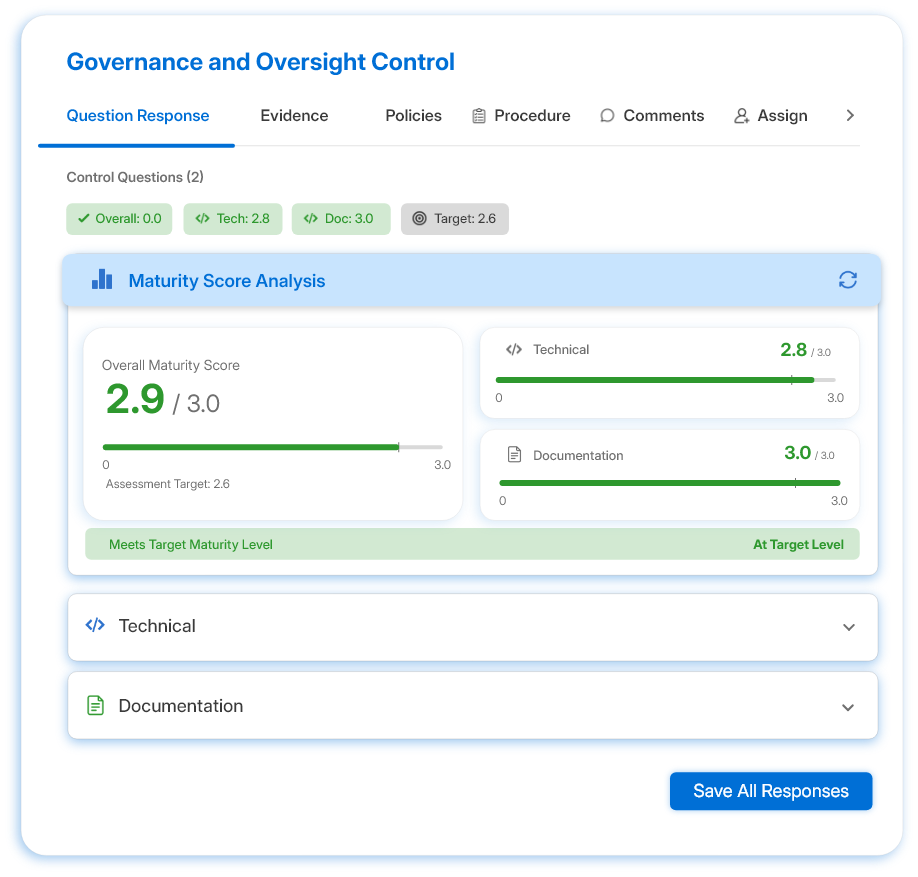
Bring the common criteria for security and any additional categories into scope, then connect each criterion and its points of focus to controls, owners and policies. See where coverage is complete and where design gaps remain.

  • Select the categories in scope.
  • Map criteria and points of focus to controls.
  • Assign an owner to every control.
Secrato platform: Maturity score
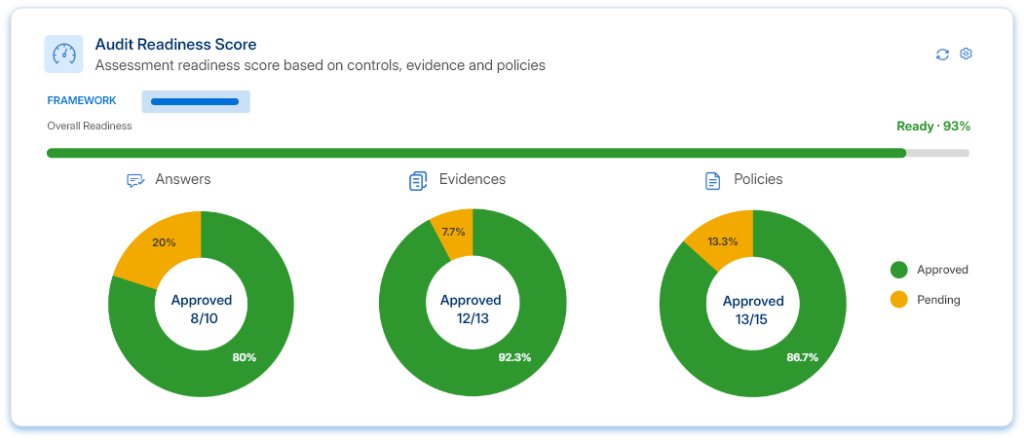
Secrato platform: Audit readiness score
OPERATING EFFECTIVENESS

Collect evidence across the whole observation period

A Type 2 report tests whether controls operated effectively over a period, typically three to twelve months. Schedule recurring evidence, follow up on missed runs and document exceptions and remediation before the auditor samples them.

  • Schedule recurring evidence per control.
  • Flag missing evidence and exceptions early.
  • Keep remediation linked to the control.
Secrato platform: Audit readiness score
AUDIT COLLABORATION

Give your CPA firm one place to work

Share the system description, control matrix and evidence with your auditor through structured access. Track requests and findings, and keep management’s responses with the controls they concern.

  • Prepare the system description and control matrix.
  • Track auditor requests and findings.
  • Share the final report through your Trust Center.
Secrato platform: Control connection
THE REST OF THE PLATFORM

More ways Secrato supports SOC 2

Beyond the core outcomes above, these capabilities support the wider SOC 2 programme.

Connect controls and requirements across frameworks to identify shared coverage and reduce duplicated assessment work.

Keep risks connected to the controls and evidence behind their treatment, with visibility into ownership and residual exposure.

Bring evidence together, review control readiness and manage findings, with structured assessor access where appropriate.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

The Trust Services Criteria overlap strongly with ISO/IEC 27001 and NIST CSF 2.0, creating significant opportunities to reuse existing controls and evidence. The Unified Control Library maps shared controls across frameworks so teams can see where existing work already contributes to SOC 2, while keeping clear that mapping shows correspondence, not equivalence.

FAQs for SOC 2 compliance software

What is SOC 2?

SOC 2® is an examination under AICPA attestation standards in which an independent CPA firm reports on a service organisation’s controls relevant to security, availability, processing integrity, confidentiality or privacy. The criteria are the 2017 Trust Services Criteria, with points of focus revised in 2022. The result is a report for customers and their auditors, not a certificate.

A Type 1 report covers the description of the system and the suitability of the design of controls at a specific date. A Type 2 report also covers whether those controls operated effectively throughout a period, typically three to twelve months, and is the report most customers ask for.

Secrato maps the Trust Services Criteria to controls, owners and policies, schedules and collects evidence across the observation period, and tracks exceptions and auditor requests. Work you already did for ISO/IEC 27001 counts where controls correspond, and the final report can be shared with customers through the Trust Center.

Security, covered by the common criteria, is part of every SOC 2 examination. Availability, processing integrity, confidentiality and privacy are optional and are added when they matter for the services you provide and the commitments you make to customers.

Keep SOC 2 readiness moving with you

SOC 2 is not a one-off project: controls, evidence and exceptions keep moving between reports. See how Secrato keeps that work connected and gives your team a clear view of readiness before your auditor asks.

Secrato