
NIS2 for cloud, data centre, managed and digital service providers
Cloud and data centre providers, content delivery networks, DNS and TLD operators, trust service providers, managed service providers and managed security service providers, as well as online marketplaces, search engines and social networks, all fall under NIS2. Many of them also follow a detailed EU implementing regulation.
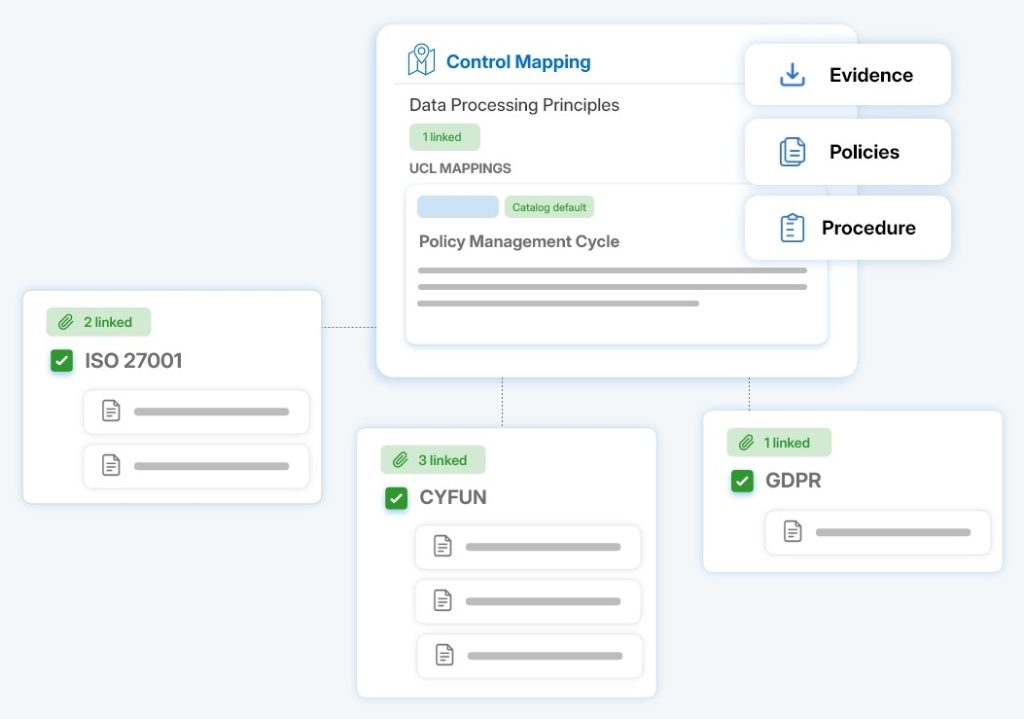
In short: Digital infrastructure and ICT service management are Annex I sectors, and digital providers are in Annex II. For cloud, data centre, CDN, DNS, TLD, trust service, MSP, MSSP and online platform providers, Implementing Regulation (EU) 2024/2690 spells out the security measures and incident thresholds. Secrato maps those requirements, NIS2 and ISO/IEC 27001 to one control set and shares the proof with customers through a trust centre.
Digital providers carry the most detailed NIS2 rules
Some digital entities are in scope whatever their size, such as qualified trust service providers, TLD name registries and DNS service providers. For the digital types listed in the implementing regulation, the main-establishment rule usually decides which Member State supervises you. Check your scope →
Prove security to the supervisor and to every customer
Implementing Regulation 2024/2690, control by control
Work through the technical and methodological requirements of Implementing Regulation (EU) 2024/2690 as controls with owners and evidence, and reuse what you already do for ISO/IEC 27001.
One trust centre for every security review
Your customers must assess their ICT suppliers under NIS2 and DORA. Publish policies, certificates and answers in a trust centre, with NDA-gated access where needed, and cut down repetitive questionnaires.
NIS2, ISO/IEC 27001 and customer frameworks together
Run NIS2, ISO/IEC 27001, SOC-style customer requirements and custom frameworks from shared controls, so a new customer framework is a mapping exercise, not a new project.
BUILT FROM BELGIUM
What applies to digital providers in the Benelux
In Belgium the CCB supervises; in the Netherlands the RDI supervises digital infrastructure and digital providers under the Cyberbeveiligingswet. Providers that serve banks and insurers are also asked about DORA, and the largest may be designated as critical ICT third-party providers at EU level.
Secrato is EU-first and hosted in a Tier IV data centre in Antwerp. Managing clients’ compliance as well? See NIS2 for MSPs and consultants.
Common questions
Which digital providers fall under Implementing Regulation (EU) 2024/2690?
DNS service providers, TLD name registries, cloud computing service providers, data centre service providers, content delivery network providers, managed service providers, managed security service providers, online marketplaces, online search engines, social networking platforms and trust service providers.
Are managed service providers in scope of NIS2?
Yes. Managed service providers and managed security service providers that serve other businesses are part of ICT service management, a sector of high criticality, when they are at least medium-sized. Large ones are generally essential entities.
Which country supervises a cloud or data centre provider?
For the digital entity types in the implementing regulation, NIS2 generally uses the main-establishment rule: the Member State where cybersecurity decisions are mainly taken. Public electronic communications providers fall under each country where they provide services.
Can we share our security posture with customers from Secrato?
Yes. The Trust Center lets you publish policies, certificates and security answers publicly or behind an NDA, so customers can review them without a questionnaire for every deal.
See how Secrato supports your NIS2 and customer assurance
Show us your services and customer requirements, and we will map them to NIS2 and Implementing Regulation 2024/2690 in Secrato.
