
Several frameworks, one team, one platform
Growing companies often face NIS2, customer demands for ISO/IEC 27001 and sector rules such as DORA or the Cyber Resilience Act at the same time, with a security and compliance team of a few people.
In short: Mid-market companies use Secrato to run NIS2, ISO/IEC 27001 and other frameworks from one control set, so each piece of evidence counts everywhere it applies. The Pro plan includes three frameworks in the main workspace and up to five per workspace, with advanced governance and automation, hosted in Belgium.
More frameworks, the same number of people
Each new framework brings its own requirements, audits and questionnaires. Without shared controls, the same policy or log review is documented three times, and the team spends its time on paperwork instead of security.
Do the work once, prove it many times
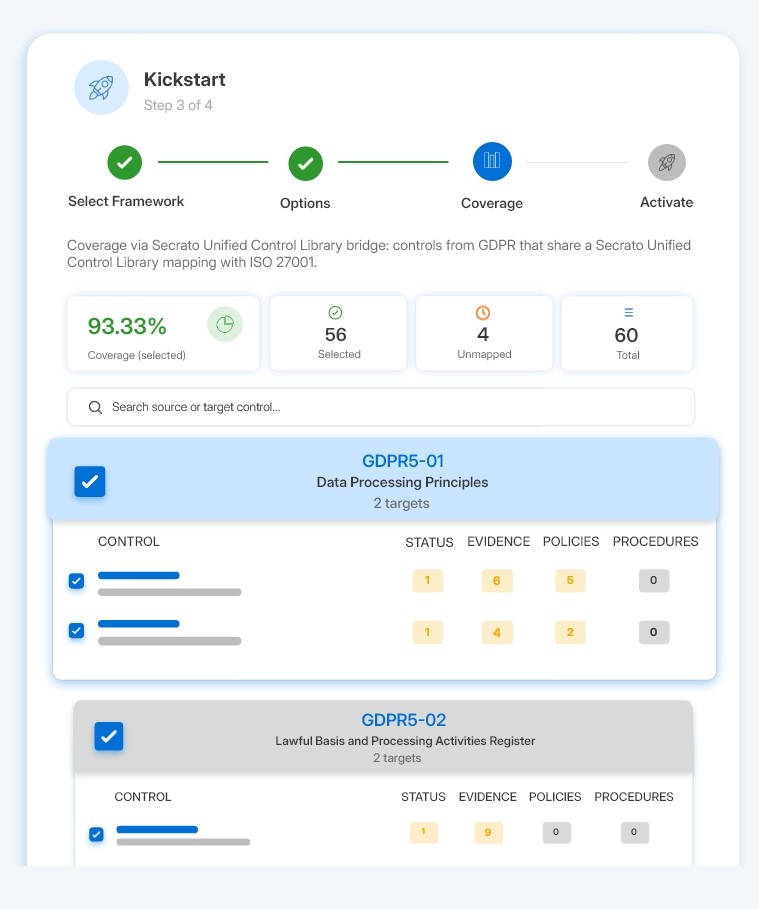
One control set for NIS2, ISO/IEC 27001 and more
Framework mapping links NIS2, ISO/IEC 27001, DORA, the CRA, CyFun® and more to shared controls, and shows the coverage per framework.
Evidence and tasks that keep themselves current
Connect your tools through 300+ integrations, assign controls and policies to owners, and let reminders and workflows keep evidence current between audits.
Audits and customer reviews without the scramble
Give auditors scoped access in the Audit Hub and share your security posture with customers through the Trust Center.
BUILT FROM BELGIUM
What applies to growing companies in the Benelux
Companies with 250 or more staff in a highly critical sector are generally essential entities under NIS2, with proactive supervision and, in Belgium, a mandatory conformity assessment. Many also hold ISO/IEC 27001 certification, so reusing that work for NIS2 saves months.
Secrato is built in Belgium and hosted in a Tier IV data centre in Antwerp. See compare plans or framework mapping. Running several entities or countries? See GRC for enterprises and groups.
Common questions
Which Secrato plan suits a mid-market company?
Most mid-market companies choose Pro: advanced governance, automation and multi-framework control, with three frameworks in the main workspace and up to five per workspace. See compare plans.
Can we reuse our ISO/IEC 27001 work for NIS2?
Yes. ISO/IEC 27001 controls are mapped to the NIS2 measures, so existing evidence counts towards NIS2 and the remaining gaps are shown per control.
Are companies with more than 250 staff essential entities?
In the sectors of high criticality (Annex I), large entities are generally essential. In the other critical sectors (Annex II) they are generally important, unless designated as essential. Use the NIS2 scope checker.
Does Secrato integrate with our existing tools?
Yes, through 300+ integrations across identity, HR, cloud, DevOps and security tools, plus the Secrato API. See integrations.
See how Secrato fits your compliance programme
Show us your frameworks and audits, and we will map them to one control set in Secrato.
