
NIS2 for hospitals, labs, pharma and medical device makers
Healthcare providers, EU reference laboratories, pharmaceutical research and manufacturing, and makers of critical medical devices are listed as highly critical under NIS2. They handle the most sensitive personal data and cannot afford long outages.
In short: Healthcare is an Annex I sector under NIS2. Large hospitals, labs and pharmaceutical companies are usually essential entities, and medium-sized ones important. Secrato links the NIS2 measures to clinical and business systems, keeps incident records ready for the 24-hour early warning, and maps NIS2, CyFun®, ISO/IEC 27001 and GDPR to one control set, hosted in Belgium.
Health is a sector of high criticality
The health sector in NIS2 covers healthcare providers, EU reference laboratories, entities doing research and development of medicinal products, manufacturers of basic pharmaceutical products and preparations, and manufacturers of medical devices considered critical during a public health emergency. Large entities are generally essential and face proactive supervision; in Belgium that includes a mandatory conformity assessment. Check your scope →
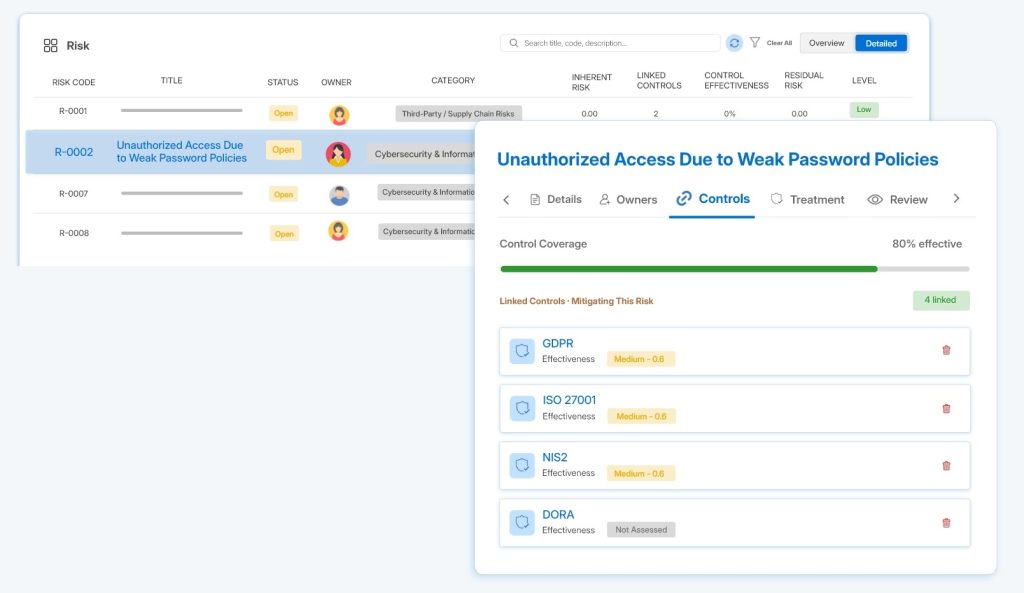
Keep patient care and compliance on the same page
Risks linked to the systems care depends on
Register the systems that care and production depend on, such as patient records, lab systems, imaging and connected devices, and link each one to its risks, controls, owners and suppliers.
Report within 24 hours without losing the thread
Keep incident records linked to the affected systems, controls and evidence, so the early warning, the 72-hour notification and the final report draw on the same facts, and the GDPR clock runs alongside.
GDPR and NIS2 from one record
Special categories of personal data, such as health data, need strong safeguards under GDPR. Map GDPR and NIS2 to shared controls such as access management, logging and supplier security, and prove them once.
BUILT FROM BELGIUM
What applies to healthcare in Belgium and the Netherlands
Belgian hospitals and health companies register with the CCB and typically use CyFun® or ISO/IEC 27001 to show the NIS2 measures; essential entities need a regular conformity assessment. Dutch healthcare organisations in scope register with the NCSC under the Cyberbeveiligingswet. Medical device manufacturers also follow the cybersecurity requirements of the Medical Device Regulation for their products.
Secrato processes all GRC data in a Tier IV data centre in Antwerp, under EU law. Prepare your team with the free tabletop exercise kit and the incident reporting playbook.
Common questions
Are hospitals essential or important entities under NIS2?
Healthcare providers are in Annex I, the sectors of high criticality. A large hospital (250 or more staff, or turnover above €50 million and balance sheet above €43 million) is generally an essential entity; a medium-sized provider is generally important, unless the authority designates it as essential.
Are pharmaceutical companies in scope of NIS2?
Yes. Research and development of medicinal products and the manufacture of basic pharmaceutical products and preparations are part of the NIS2 health sector, for entities that are at least medium-sized.
How do NIS2 and GDPR overlap in healthcare?
A cyber incident involving patient data can trigger both the NIS2 reporting clock (24 hours, 72 hours, one month) and the GDPR breach notification (72 hours). Many safeguards overlap, so Secrato maps both to the same controls and keeps one incident record.
Where is our data hosted?
All GRC data in Secrato is processed on self-managed infrastructure in a Tier IV data centre in Antwerp, Belgium, under EU law. See sovereign enterprise security.
See how Secrato supports your NIS2 programme in healthcare
Show us your sites, systems and frameworks, and we will map them to NIS2 and GDPR in one place.
