






ISO/IEC 27001

ISO/IEC 27001 compliance that stays audit-ready

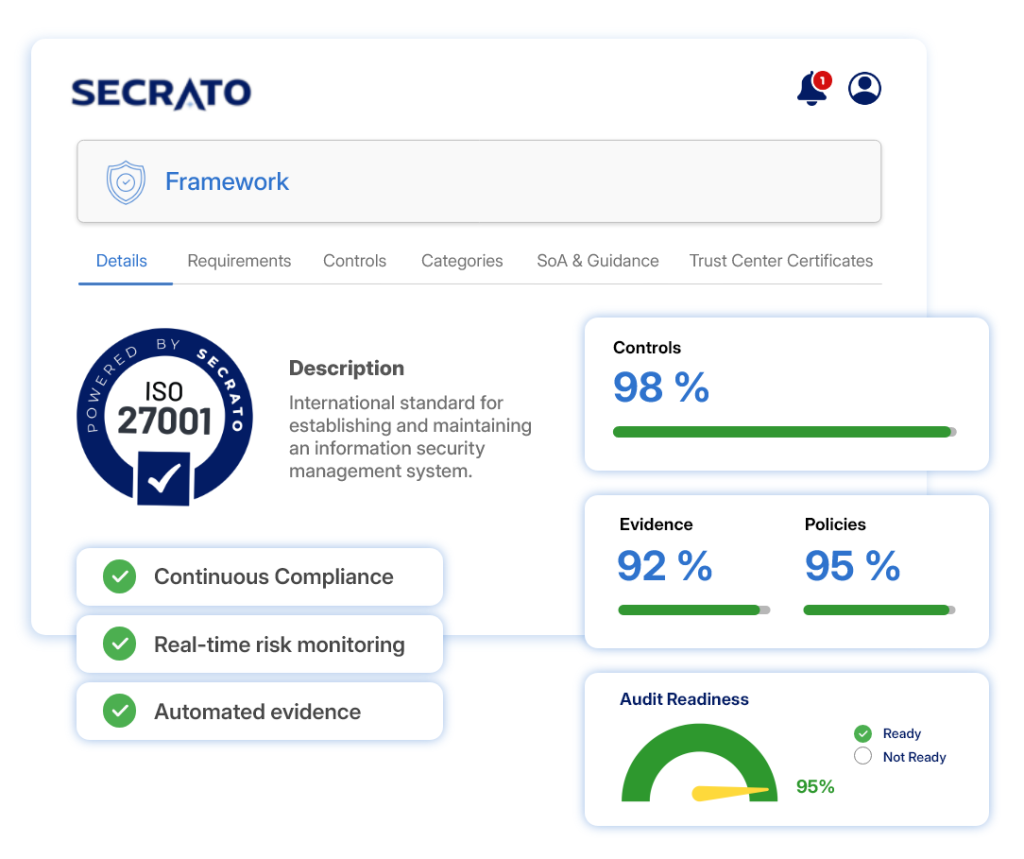
ISO/IEC 27001 asks you to run an information security management system and show it works. Secrato keeps your controls and evidence connected to the requirements they answer so what you can demonstrate stays current.

ISO/IEC 27001 compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
EVIDENCE MANAGEMENT

Keep controls backed by current evidence

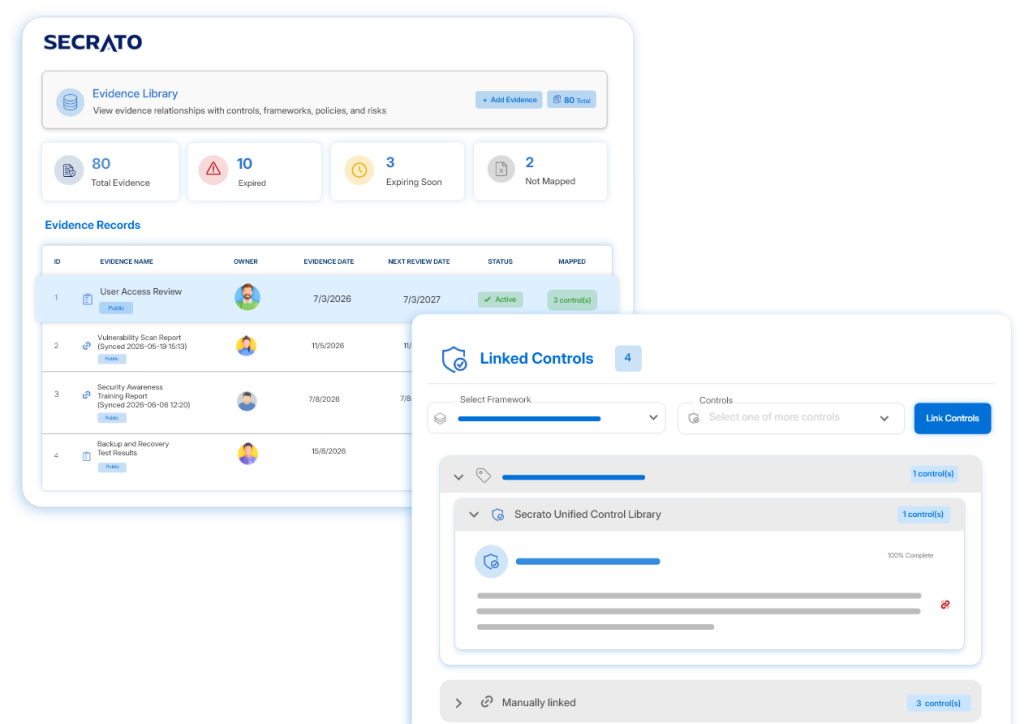
Connect evidence directly to the controls it supports so teams can see what is in place and where attention is needed. Keep supporting records organised and traceable as evidence changes.

  • Link evidence directly to the controls it supports.
  • Keep evidence current through uploads and integrations.
  • Keep records traceable for assessments and audits.
Secrato platform: Evidence library
Secrato platform: Control connection
RISK & GOVERNANCE

Connect risks, controls and policies

Bring the relationships between risks, controls and governing policies into one connected environment. See how risks are treated and which records support each control without reconciling information across separate systems.

  • Connect policies, procedures and control ownership.
  • Link controls to the risks they are designed to treat.
  • Keep treatment and residual exposure visible.
Secrato platform: Control connection
AUDIT READINESS

Stay ready for review and audit

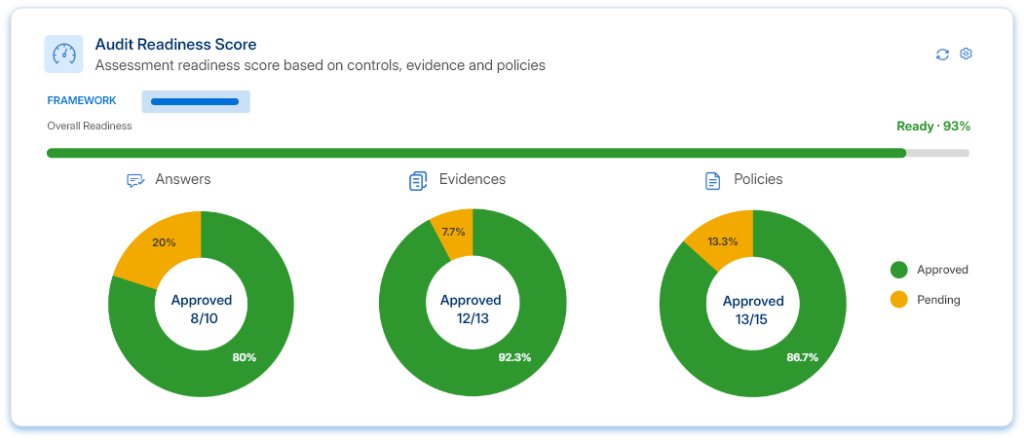
Maintain a current view of control status, risk posture and ISO/IEC 27001 readiness throughout the assessment cycle. Keep supporting information organised so reviewers can follow how requirements are being addressed.

  • Link assessment responses to evidence and policies.
  • Organise evidence and findings for audit review.
  • Track control status and target maturity.
Secrato platform: Audit readiness score
THE REST OF THE PLATFORM

More ways Secrato supports ISO/IEC 27001

Beyond the core outcomes above, these capabilities support the wider ISO/IEC 27001 programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

See where controls supporting ISO/IEC 27001 also address requirements in the other standards and regulations your organisation carries.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

Many ISO/IEC 27001 controls overlap with security requirements organisations also manage under NIS2, DORA and other cybersecurity frameworks. Secrato’s Unified Control Library maps shared controls across the relevant requirements, so teams can maintain and assess common control work once while keeping the requirements unique to each framework clearly visible.

FAQs for ISO/IEC 27001 compliance software

What is ISO/IEC 27001?

ISO/IEC 27001 is the international standard setting the requirements for an information security management system (ISMS). ISO/IEC 27001:2022 is the current edition of the international standard for information security management systems. It defines the requirements an ISMS must meet, while ISO/IEC 27002:2022 provides companion guidance on information security controls.

Yes, where requirements genuinely overlap. Controls maintained for ISO/IEC 27001 can often support corresponding requirements in other cybersecurity frameworks. Secrato maps that shared control work through the Unified Control Library while keeping each framework’s distinct obligations visible.

Secrato supports ISO/IEC 27001 readiness by connecting requirements, controls, risks, policies, evidence and assessments, giving organisations a clearer and more traceable view of how the ISMS is being implemented, maintained and demonstrated.

Keep ISO/IEC 27001 readiness current between audits

An ISMS is stronger when controls, risks and evidence remain connected. Secrato keeps the governance record behind ISO/IEC 27001 visible and traceable, giving teams a clearer view of readiness as the management system evolves.

Secrato