
Group-wide GRC across entities, countries and frameworks
Groups with subsidiaries in several countries must register and comply entity by entity, often under different national NIS2 laws, alongside DORA, ISO/IEC 27001, the CRA and customer frameworks.
In short: Enterprises and groups use Secrato to give each subsidiary, region or business unit its own workspace while governance, frameworks and reporting stay connected at group level. Global Governance cascades decisions, dashboards roll status up, and all GRC data stays in a Tier IV data centre in Antwerp under EU law. The Enterprise plan includes five frameworks in the main workspace and unlimited frameworks per workspace.
Every entity, every country, its own obligations
Under NIS2, each establishment generally follows the law of the Member State where it is established, so a Benelux group can have registrations and supervisors in several countries. Partner and linked enterprises also count when sizing an entity, so small subsidiaries of large groups are usually treated as large.
Central governance with local ownership
Tenants, workspaces and sub-workspaces
Model the group as tenants, workspaces and sub-workspaces, so each entity owns its controls, risks and evidence while the group keeps the overview.
Decide once, cascade everywhere
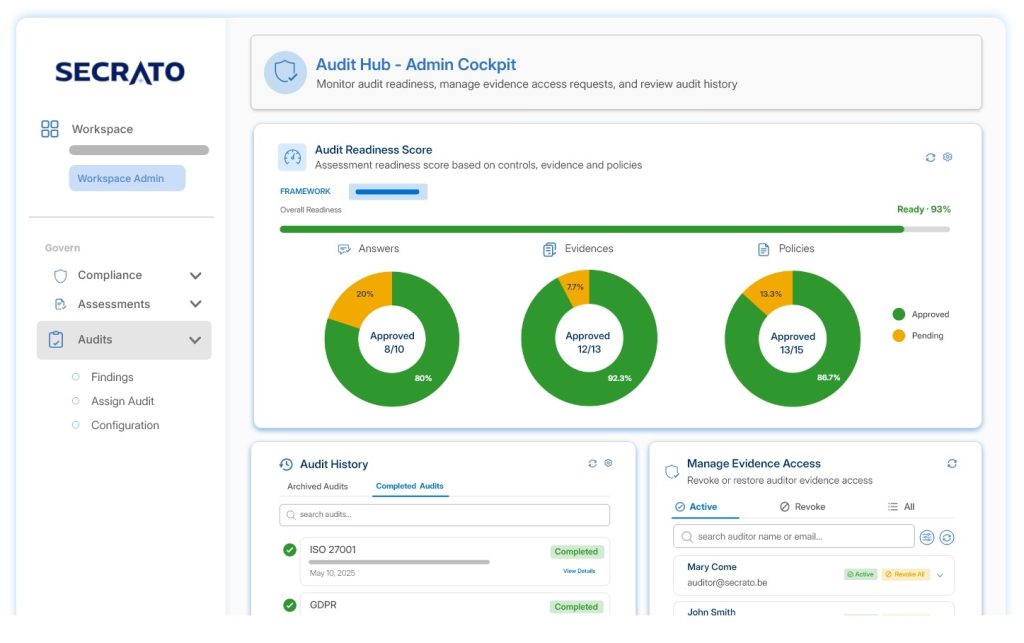
Set frameworks, policies and attributes at the top and cascade them through the hierarchy with Global Governance, so every entity starts from the same standard.
Audits, boards and customers on one source
Give auditors scoped access in the Audit Hub, report to the board from the same data, and share your posture with customers through the Trust Center.
BUILT FROM BELGIUM
What applies to groups operating in the Benelux
Essential entities face proactive supervision; in Belgium they need a regular conformity assessment, and in the Netherlands the Cyberbeveiligingswet applies with its own registration and reporting. Groups with financial entities add DORA, and manufacturers add the Cyber Resilience Act.
Secrato is self-managed infrastructure in Belgium, an answer to the data-residency questions of boards and regulators. See sovereign enterprise security and multi-tenant workspace management.
Common questions
Do we need to register every subsidiary for NIS2?
Each in-scope legal entity registers in each Member State that has jurisdiction. For most sectors that is the country where the entity is established; for certain digital providers it is the country of the main establishment.
Is a small subsidiary of a large group in scope?
Usually yes. NIS2 sizes an entity with its partner and linked enterprises, so a small subsidiary of a large group is generally treated as large.
Which Secrato plan suits a group?
The Enterprise plan is built for large organisations: five frameworks in the main workspace and unlimited frameworks per workspace, with multi-entity governance. See compare plans.
Where is our data hosted?
All GRC data is processed on self-managed infrastructure in a Tier IV data centre in Antwerp, Belgium, under EU law.
See how Secrato structures GRC for your group
Show us your group structure, and we will map it to tenants, workspaces and governance in Secrato.
