
DORA and NIS2 for banks, insurers and financial entities
Banks and financial market infrastructures are listed in NIS2, but for ICT risk management and incident reporting the Digital Operational Resilience Act (DORA) takes precedence. Insurers, investment firms and payment institutions follow DORA too. Their ICT providers often fall under NIS2.
In short: DORA has applied since 17 January 2025 and is the specific law for ICT risk management, incident reporting, resilience testing and ICT third-party risk in the financial sector, so it replaces the matching NIS2 obligations for banks and market infrastructures. Secrato maps DORA, NIS2 and ISO/IEC 27001 to one control set, keeps the register of ICT providers current and supports incident classification.
Where DORA applies and where NIS2 still matters
NIS2 Article 4 lets sector-specific EU law take over where it is at least equivalent, and DORA does that for financial entities. NIS2 remains relevant for group companies outside DORA and for your ICT providers, such as cloud and managed service providers. DORA compliance software →
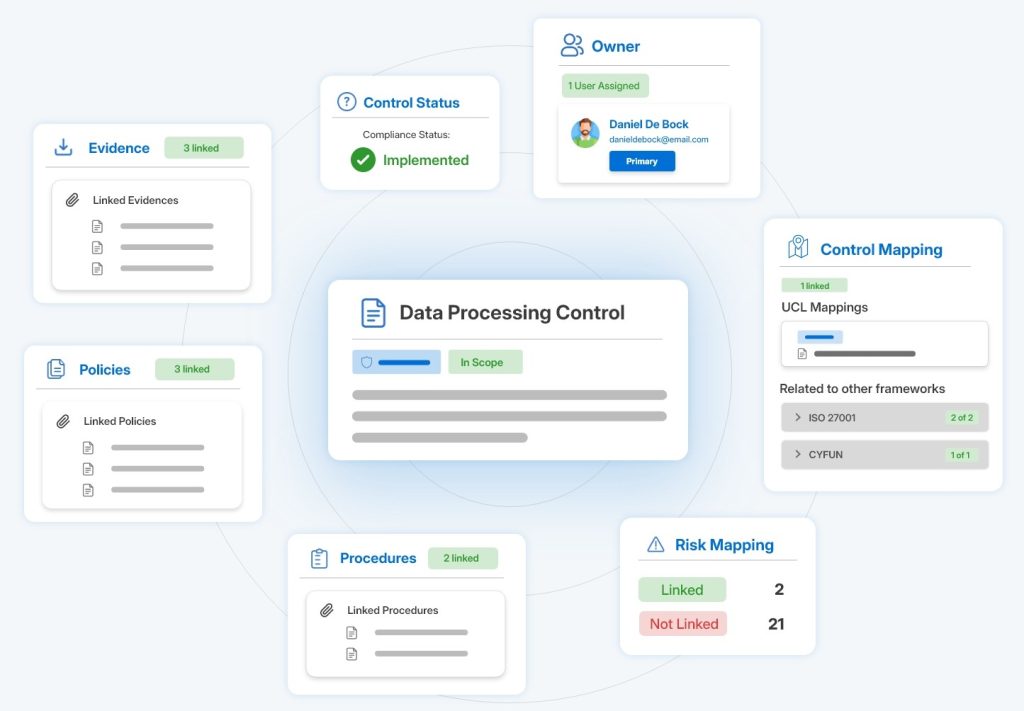
One ICT risk framework for regulators and auditors
DORA's ICT risk-management framework as controls
Turn DORA’s ICT risk-management framework into controls with owners and evidence, and reuse ISO/IEC 27001 work where it overlaps.
Your register of ICT providers, kept current
Keep contracts, criticality and assessments of ICT third-party providers in one supplier register, linked to the functions they support, ready for the register of information your supervisor asks for.
Classification, reporting and resilience testing
Classify major ICT-related incidents, keep the initial, intermediate and final reports on one record, and track resilience testing and follow-up actions.
BUILT FROM BELGIUM
What applies in Belgium and the Netherlands
In Belgium, the National Bank of Belgium and the FSMA supervise DORA; in the Netherlands, De Nederlandsche Bank and the AFM. Banks often also hold ISO/IEC 27001 certification and must answer group and customer audits, so one shared control set saves work across all of them.
Secrato processes all GRC data in a Tier IV data centre in Antwerp, under EU law. Start with the DORA step-by-step guide for the Benelux or the free DORA gap assessment.
Common questions
Do banks have to comply with NIS2 or DORA?
Banks and financial market infrastructures are listed in NIS2, but DORA is the specific law for ICT risk management, incident reporting, resilience testing and ICT third-party risk, so those DORA rules apply instead of the matching NIS2 obligations.
Since when does DORA apply?
DORA has applied since 17 January 2025 to banks, insurers, investment firms, payment and e-money institutions, crypto-asset service providers and other financial entities.
Are ICT providers to banks covered?
ICT providers must support their financial customers’ DORA obligations through contracts and assessments. Cloud, data centre and managed service providers are usually in NIS2 scope themselves, and the most important ones can be designated as critical ICT third-party providers under DORA.
Does Secrato support both DORA and NIS2?
Yes. DORA, NIS2, ISO/IEC 27001 and other frameworks are mapped to shared controls, so evidence is collected once. See framework mapping.
See how Secrato supports your DORA programme
Show us your entities and frameworks, and we will map DORA, NIS2 and ISO/IEC 27001 in Secrato.
