






CYBERBEVEILIGINGSWET

Cyberbeveiligingswet (Cbw) compliance you can show your supervisor

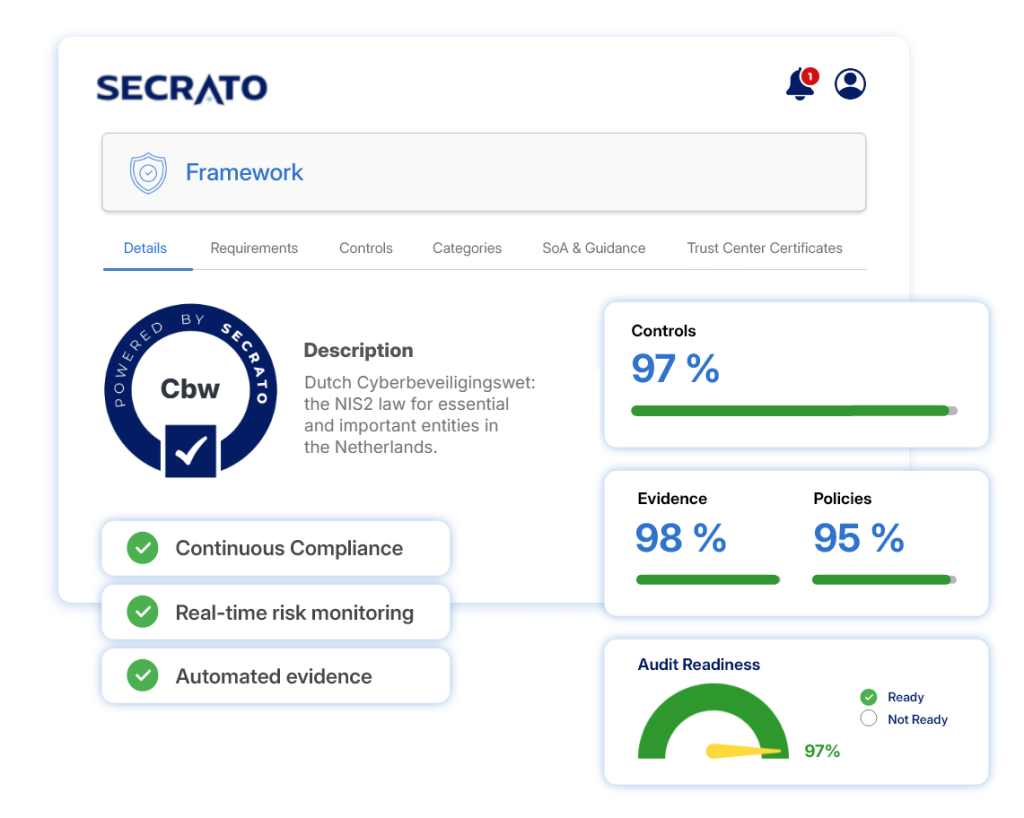
The Cyberbeveiligingswet (Cbw) has applied in the Netherlands since 15 August 2026 and implements NIS2. Secrato keeps your zorgplicht measures, incident reports and board decisions connected to the controls and evidence behind them, so you can show your supervisor where you stand at any moment.

In short: Secrato helps Dutch organisations meet the Cbw. Check whether you are an essential or important entity, register with the NCSC via MijnNCSC, implement the minimum measures of the Cyberbeveiligingsbesluit (Cbb, articles 6 to 18), report significant incidents within 24 hours, 72 hours and one month, and give the board what it needs to approve and oversee the measures.

Cyberbeveiligingswet (Cbw) compliance in Secrato
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
DUTY OF CARE

Meet the zorgplicht, measure by measure

Translate the minimum measures of the Cyberbeveiligingsbesluit into owned controls, from risk analysis and incident handling to supply chain security, cryptography and multi-factor authentication. See which measures are in place and where action is still needed.

  • Map Cbb articles 6 to 18 to controls and owners.
  • Track implementation status per measure.
  • Link each measure to its risks and evidence.
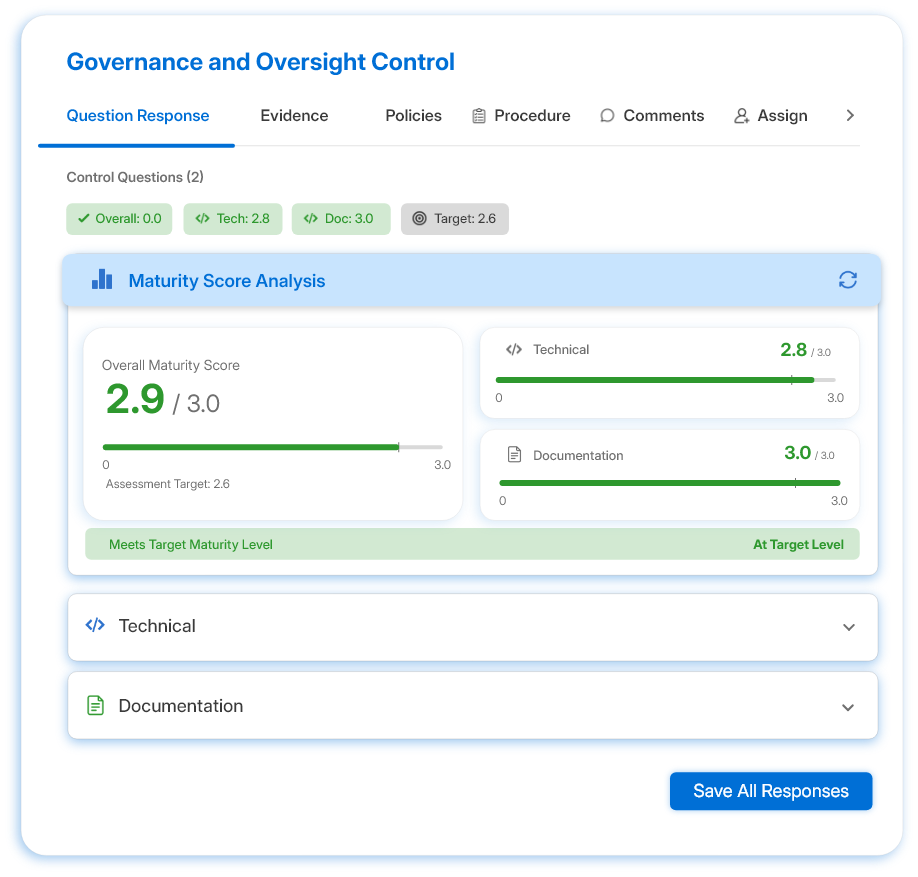
Secrato platform: Maturity score
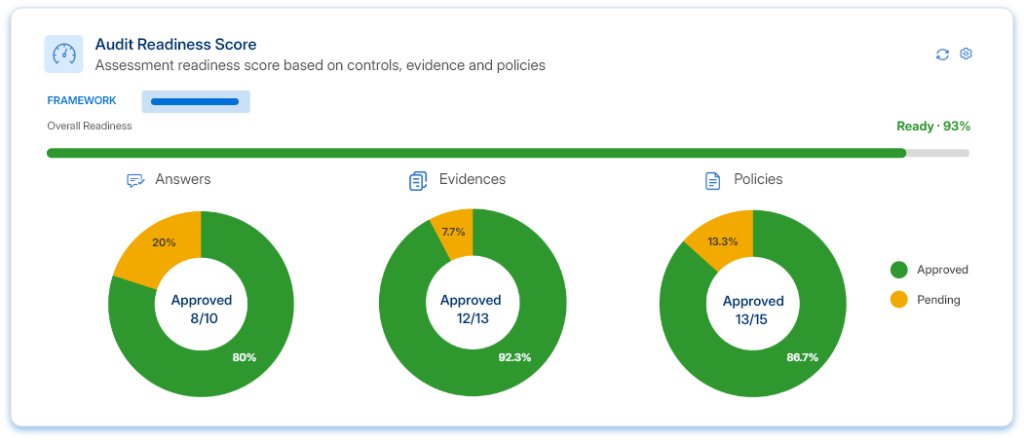
Secrato platform: Audit readiness score
INCIDENT REPORTING

Report significant incidents on time

Record incidents, assess whether they are significant and keep the reporting clock in view. Prepare the early warning, the incident notification and the final report for MijnNCSC with facts, impact and measures in one place.

  • Track the 24-hour, 72-hour and one-month deadlines.
  • Keep incident facts, impact and measures together.
  • Keep a record of what was reported and when.
Secrato platform: Audit readiness score
BOARD RESPONSIBILITY

Give the board what it must approve and oversee

Under the Cbw the board approves the cybersecurity measures, oversees their implementation and follows training. Give directors a current view of measures, risks and incidents, and record their decisions and training.

  • Present measures and risk status to the board.
  • Record approvals and oversight decisions.
  • Track board training.
Secrato platform: Control connection
THE REST OF THE PLATFORM

More ways Secrato supports the Cbw

Beyond the core outcomes above, these capabilities support the wider Cbw programme.

Connect controls and requirements across frameworks to identify shared coverage and reduce duplicated assessment work.

Keep risks connected to the controls and evidence behind their treatment, with visibility into ownership and residual exposure.

Bring evidence together, review control readiness and manage findings, with structured assessor access where appropriate.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

The Cbb measures build on the same foundations as ISO/IEC 27001, CyFun® and BIO2, creating significant opportunities to reuse existing cybersecurity controls. The Unified Control Library maps shared controls across frameworks so teams can see where existing work already contributes to the Cbw, while keeping clear that mapping shows correspondence, not equivalence.

FAQs for Cbw compliance software

What is the Cyberbeveiligingswet (Cbw)?

The Cyberbeveiligingswet (Cbw) is the Dutch law that implements the EU NIS2 Directive. Together with the Cyberbeveiligingsbesluit (Cbb), which sets the minimum measures, it has applied since 15 August 2026 and replaces the Wet beveiliging netwerk- en informatiesystemen (Wbni). The Wet weerbaarheid kritieke entiteiten (Wwke), which implements the CER Directive, took effect on the same day.

The Cbw covers medium-sized and large organisations in 18 sectors, such as energy, transport, healthcare, drinking water, digital infrastructure and public administration, and some organisations regardless of their size. They are classed as essential or important entities: essential entities face proactive supervision, important entities mainly supervision after the fact. Organisations assess for themselves whether they are in scope and register with the NCSC via MijnNCSC.

Secrato maps the Cbb measures to controls, owners and evidence, keeps risks and incidents connected to the measures that address them, and tracks the reporting deadlines for significant incidents. Work you already did for ISO/IEC 27001, CyFun® or BIO2 counts where controls correspond, and board approvals and training are recorded alongside the measures.

A significant incident is reported through MijnNCSC with an early warning within 24 hours, an incident notification within 72 hours and a final report within one month of the notification. The report reaches the competent CSIRT and the supervisor. Secrato keeps the incident record, the deadlines and what was reported together.

Keep Cbw readiness moving with you

The Cbw is not a one-off project: measures, risks, incidents and board oversight keep moving. See how Secrato keeps that work connected and gives your team a clear view of readiness before your supervisor asks.

Secrato