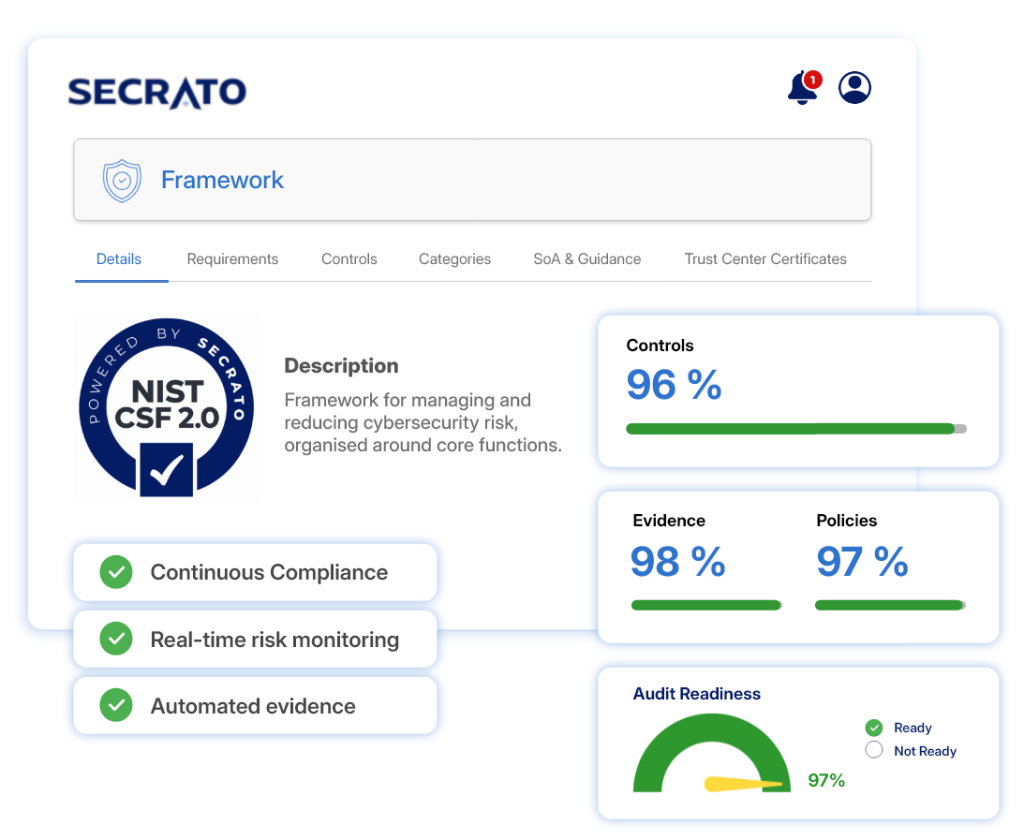
NIST CSF 2.0 sets out cybersecurity as outcomes you assess and show, across its six functions. Secrato keeps the controls, policies and evidence behind each outcome connected to the Subcategory it serves, so your Current Profile stays current between reviews.
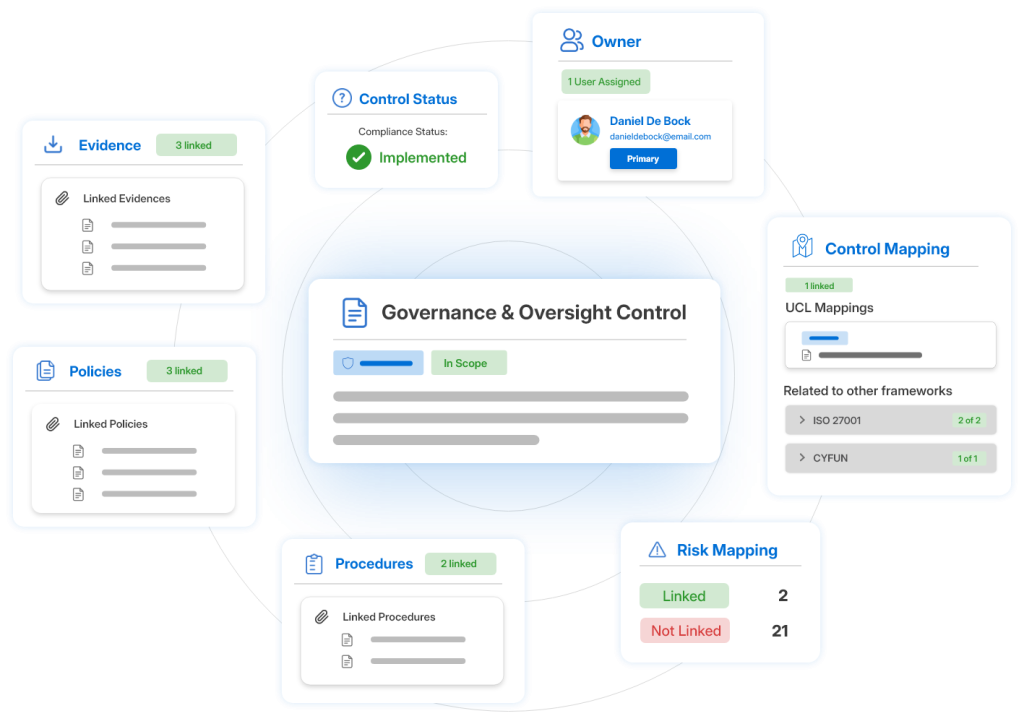
Connect cybersecurity strategy, policies, risks and controls across workspaces and entities. Apply central governance decisions while allowing approved local deviations where needed.
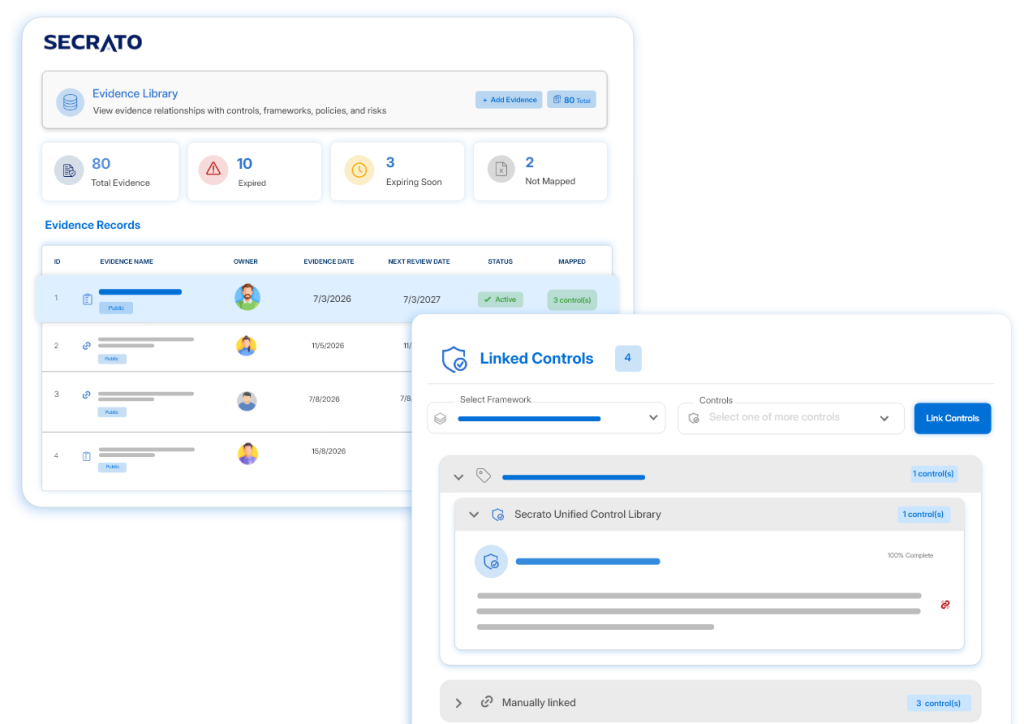
Connect evidence directly to the controls and CSF outcomes it supports. Keep records current through uploads, imports and integrations so teams can demonstrate how cybersecurity outcomes are being achieved.
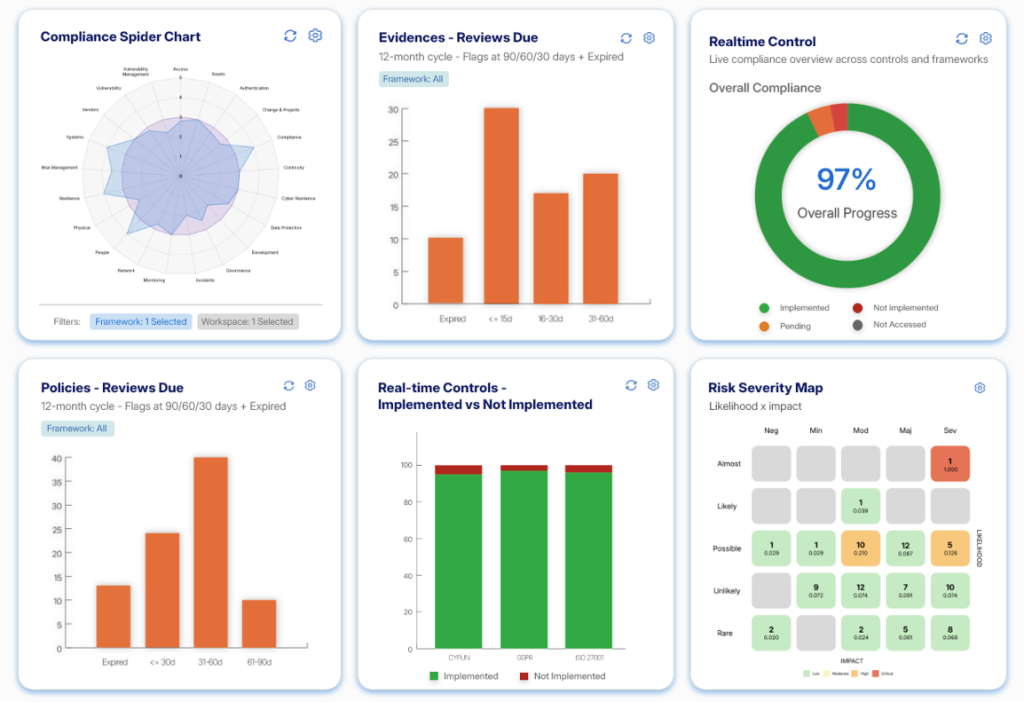
Compare current performance with target outcomes and keep gaps visible across the CSF functions. Maintain compliance status, findings and readiness in one view so teams can prioritise the work needed.
Beyond the core outcomes above, these capabilities support the wider NIST CSF 2.0 programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Keep risks tied to the controls and evidence behind them, with visibility into ownership, treatment and residual exposure.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.
See where controls supporting CSF outcomes also address requirements in the other frameworks your organisation carries.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
NIST CSF 2.0 is designed to work alongside other cybersecurity standards so many CSF outcomes can be supported by controls an organisation already maintains. The Unified Control Library maps those controls across the relevant outcomes and requirements, helping teams reuse existing work while seeing what remains to reach their CSF Target Profile.
+ More & growing
NIST CSF 2.0 is a voluntary cybersecurity framework that organises outcomes across six functions: Govern, Identify, Protect, Detect, Respond and Recover. NIST CSF 2.0, published as final NIST CSWP 29 on 26 February 2024, is the operative edition of the NIST Cybersecurity Framework. It provides non-prescriptive guidance and a taxonomy of high-level cybersecurity outcomes that can be used by organisations regardless of size, sector or maturity.
CSF 2.0 is designed for organisations of any size, sector or cybersecurity-maturity level. It is generally voluntary guidance, but external legal, regulatory, contractual, customer or supply-chain requirements may require its use for particular organisations.
Secrato supports CSF 2.0 by connecting governance, controls, policies, evidence and assessments to those outcomes, giving organisations a clearer view of their current posture, target state and the gaps between them.
A current profile is most useful when it continues to reflect how cybersecurity is actually being governed and improved. See how Secrato can connect CSF outcomes with the controls, risks and evidence behind them.
Data-driven realtime compliance for continuous readiness
Continuous readiness through structured assessments
Centralize, automate, and stay ahead of risks
Integrated policy & evidence for consistent governance