
EU AI Act compliance with AI governance ready to demonstrate
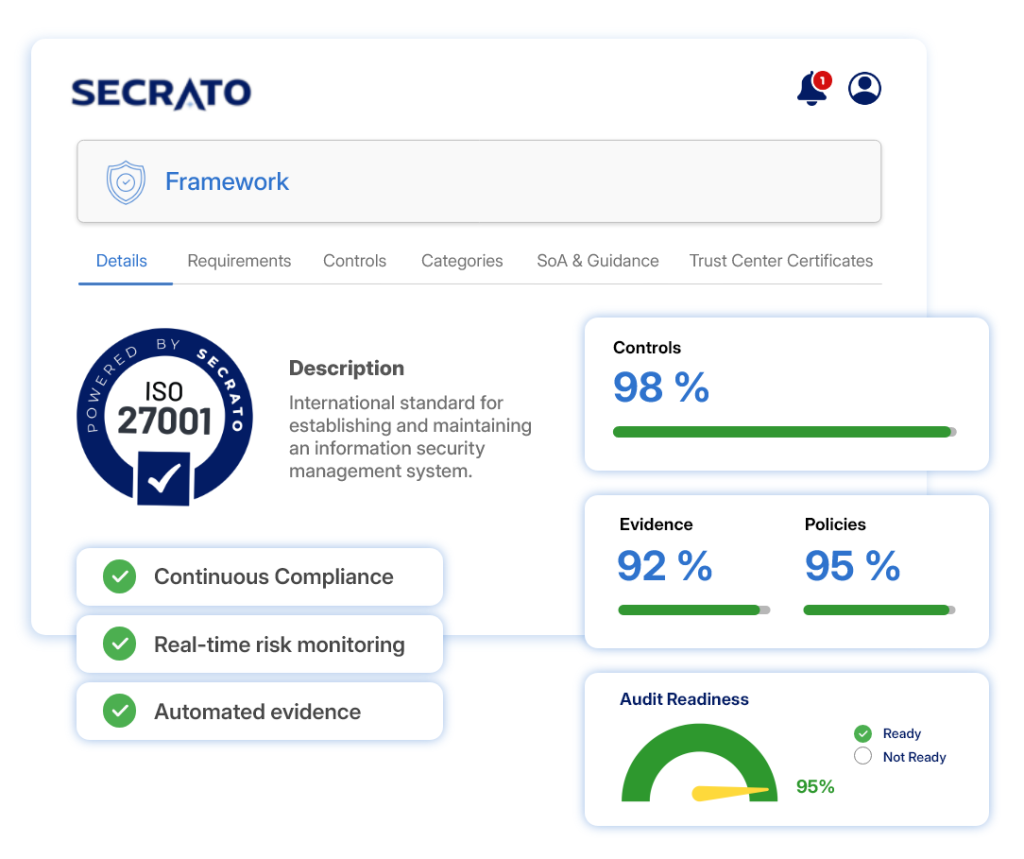
The EU AI Act requires organisations to govern AI according to their role and the risks involved. Secrato keeps AI risks, controls, policies and evidence connected to the requirements they answer. Governance decisions and readiness stay visible as obligations take effect.
Connect AI risks to governance controls
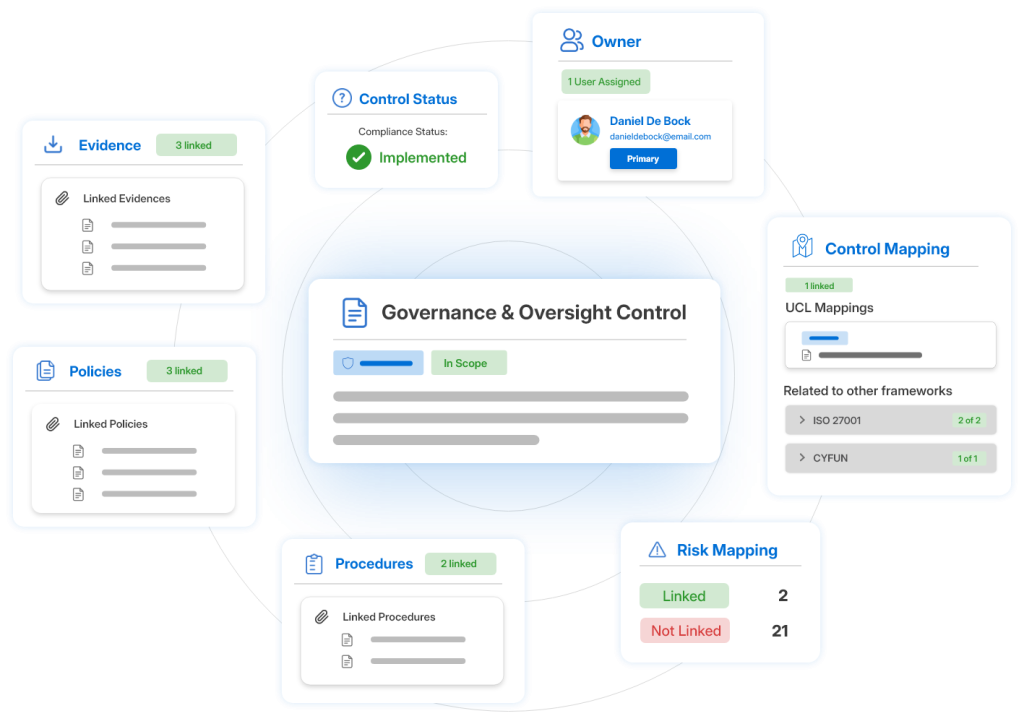
Link identified AI risks to the controls used to treat them and keep the supporting policies, procedures and ownership visible. Give teams a clearer view of how risk-management decisions translate into governed action.
Link AI risks to the controls that treat them.
Connect policies, procedures and ownership.
Keep risk treatment visible and traceable.
Keep obligations backed by evidence
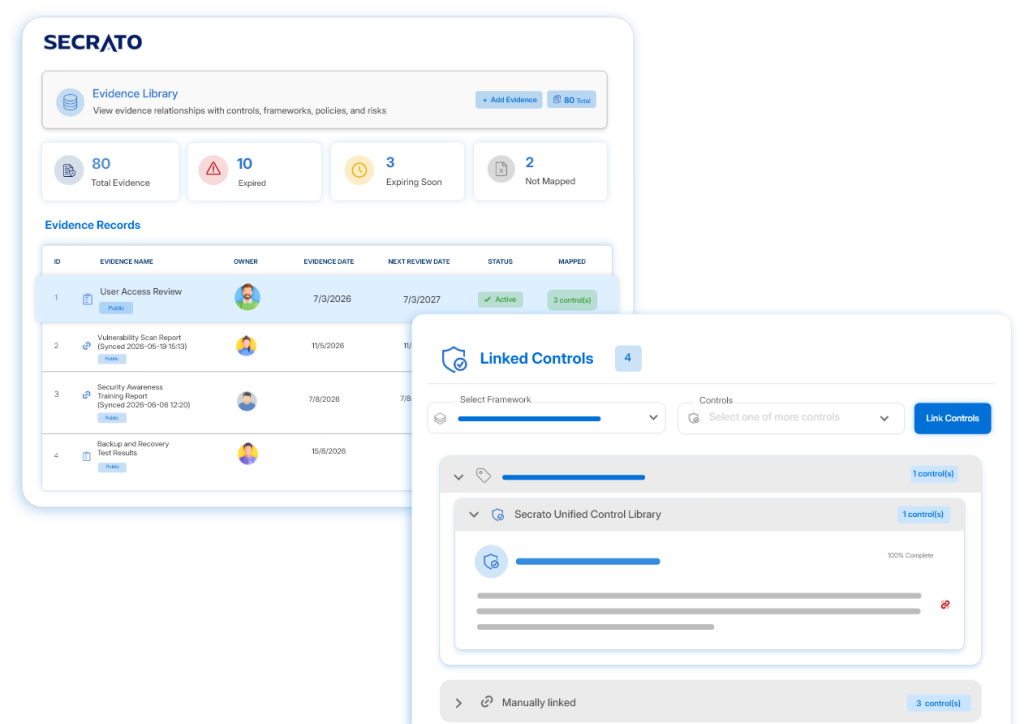
Connect supporting evidence to the controls and requirements it substantiates. Maintain records behind governance measures such as oversight, transparency, risk management and other applicable obligations without rebuilding the evidence picture for every review.
Link evidence directly to relevant controls.
Keep supporting records current and traceable.
Reduce repeated evidence collection.
Connect risks, controls and policies
Bring the relationships between risks, controls and governing policies into one connected environment. See how risks are treated and which records support each control without reconciling information across separate systems.
- Connect policies, procedures and control ownership.
- Link controls to the risks they are designed to treat.
- Keep treatment and residual exposure visible.
Maintain oversight as requirements evolve
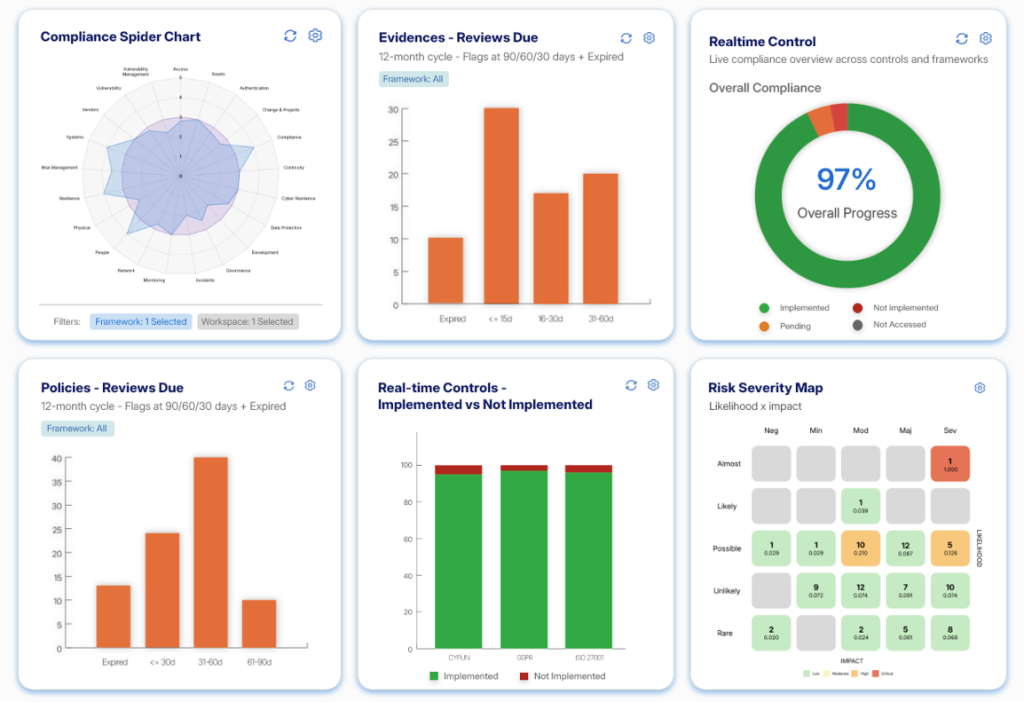
Bring assessment status, risks, control coverage and findings into a clearer view of AI Act readiness. Give governance teams and management visibility into what is covered, what needs attention and where further action is required.
See readiness across requirements and controls.
Track risks, findings and assessment progress.
Give management clearer oversight.
More ways Secrato supports the EU AI Act
Beyond the core outcomes above, these capabilities support the wider EU AI Act programme.
Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.
Scope, score and assign assessment work, with responses linked to the evidence and records behind them.
Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.
See where controls supporting EU AI Act also address requirements in the other standards and regulations your organisation carries.
Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.
Share relevant security and compliance information with stakeholders through controlled public or gated access.
One control. Multiple frameworks.
Many controls supporting the EU AI Act also contribute to other compliance and security frameworks. Secrato’s Unified Control Library maps shared controls across the relevant requirements so teams can reuse common governance work without treating the frameworks as equivalent.
+ More & growing
FAQs for EU AI Act compliance software
What is EU AI Act?
The EU AI Act establishes harmonised rules for artificial intelligence based on the role of the organisation and the risks associated with the AI system or model. Secrato supports AI Act governance by connecting AI risks, controls, policies, evidence and assessments, giving organisations a traceable view of how applicable requirements are being managed and demonstrated.
Who does the EU AI Act apply to?
The AI Act applies to several actors across the AI value chain. These include providers placing AI systems or general-purpose AI models on the EU market, deployers based in the EU, importers and distributors, and certain organisations outside the EU where the output of their AI systems is used in the Union.
How does Secrato support EU AI Act?
Secrato supports the governance side of AI Act readiness by connecting risks, controls, policies, procedures, evidence and assessments to the requirements an organisation needs to manage. Legal classification, technical implementation, conformity assessment and regulatory submissions remain outside the platform.
Make AI governance easier to demonstrate
Organisations also need a clear record of the risks, controls, decisions and evidence behind their governance programme. Secrato keeps that work connected, giving teams and management a clearer view of how AI governance is developing over time.
