
NIS2 for research organisations
Research organisations hold valuable intellectual property and work with many partners on open networks. NIS2 covers research organisations whose main goal is applied research or experimental development with a view to commercial use, when they are at least medium-sized.
In short: Research organisations that conduct applied research or experimental development to exploit the results commercially are “other critical” entities under NIS2, and usually important entities when they are at least medium-sized. Education institutions are excluded from this sector, although some countries can bring them in. Secrato helps you register research assets, link them to risks and controls, and show partners how you protect data.
Research is a critical sector under NIS2
The NIS2 definition of a research organisation excludes educational institutions. Universities may still be covered in other ways: as public administration entities, through a university hospital under health, or when national law adds them. Check your scope →
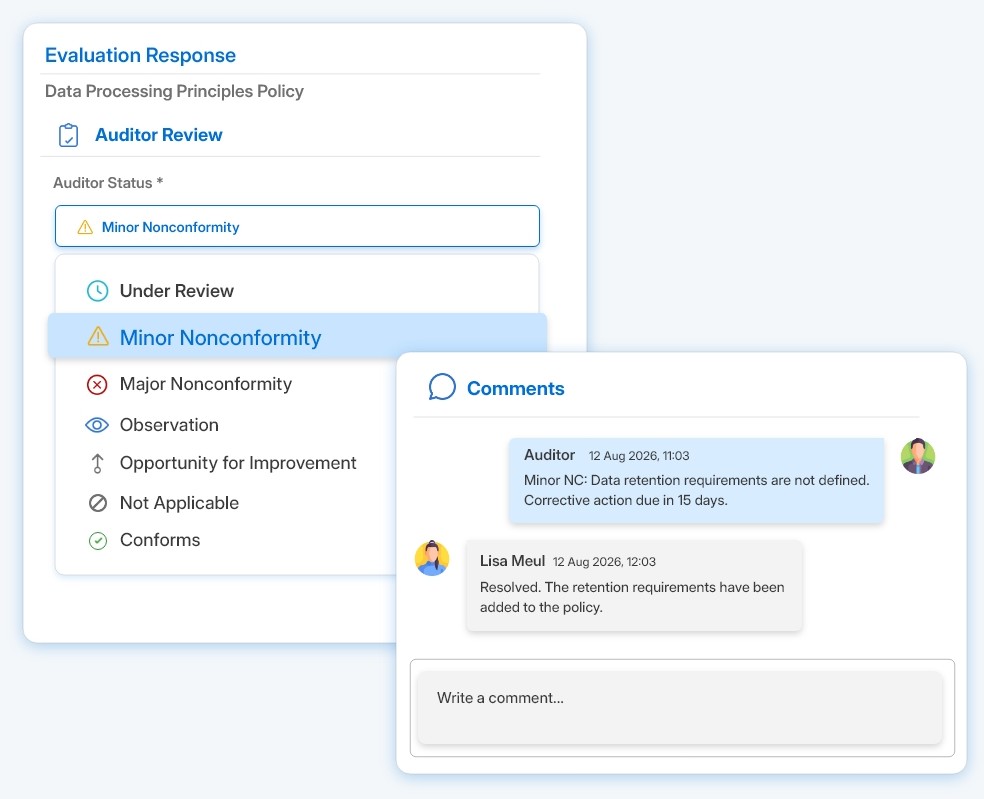
Protect research data without closing the lab
Know what you hold and who can reach it
Record research systems, datasets and labs as assets, classify them, and link them to access controls, owners and risks.
Collaboration with clear agreements
Keep consortium partners, suppliers and their security commitments in one register, and follow up on questionnaires and agreements.
Show funders and partners how you secure data
Use evidence from ISO/IEC 27001, CyFun® or NIS2 controls to answer security questions from funders, industry partners and customers.
BUILT FROM BELGIUM
What applies to research in Belgium and the Netherlands
In Belgium, research is an Annex II sector supervised with the Federal Minister for Science Policy as the sectoral authority; public universities may fall in scope as public administration entities. In the Netherlands, research institutions are important entities under the Cyberbeveiligingswet, and higher education institutions are covered only if the minister brings them in by regulation.
Secrato is built in Belgium and hosted in a Tier IV data centre in Antwerp. See how ISO/IEC 27001 and NIS2 fit together in one control set.
Common questions
Are research organisations in scope of NIS2?
Yes, if their primary goal is to conduct applied research or experimental development with a view to exploiting the results commercially, and they are at least medium-sized. They are generally important entities.
Are universities covered by NIS2?
Education institutions are excluded from the research sector. They can still be covered as public administration entities, through a university hospital, or when a Member State adds them, which the Directive allows.
Which authority is responsible in Belgium?
The Federal Minister for Science Policy is the sectoral authority for research and space, with the CCB as the national cybersecurity authority.
Where do we start?
Confirm your scope, list your research systems and datasets, and choose a framework such as CyFun® or ISO/IEC 27001 to show the NIS2 measures.
See how Secrato supports your research organisation
Show us your research organisation and frameworks, and we will map them to NIS2 in Secrato.
