
GAMP 5

GAMP 5 compliance, computerised systems you can show are fit for use

GAMP 5 asks for a risk-based approach to computerised systems in GxP environments. Secrato keeps the risks, controls, procedures and evidence behind each system connected to the requirements they answer, so your position holds up when an inspector asks.

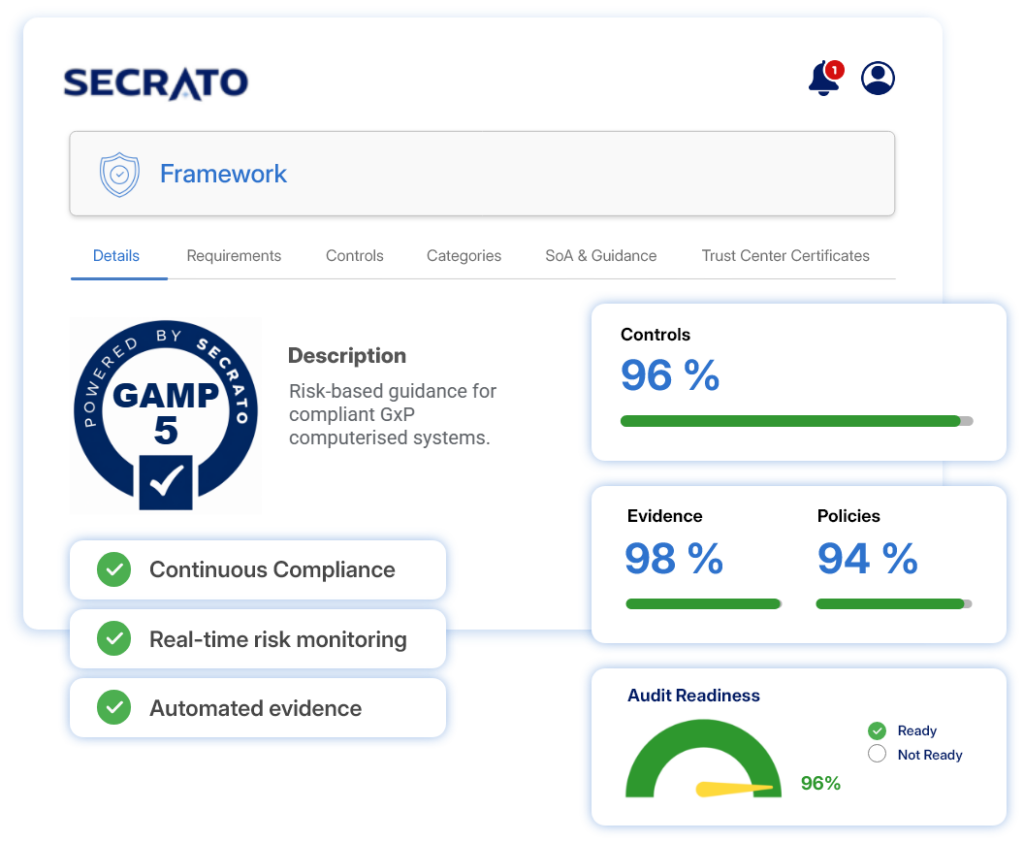
GAMP 5 framework banner
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
RISK-BASED APPROACH

Scale the effort to the risk

Record the GxP impact of each computerised system and connect it to the risks, controls and decisions that set the level of assurance required. Keep the reasoning visible, so the effort matches the risk to patient safety, product quality and data integrity.

  • Record GxP impact per system.
  • Link risks to the controls that address them.
  • Keep the rationale for each decision visible.
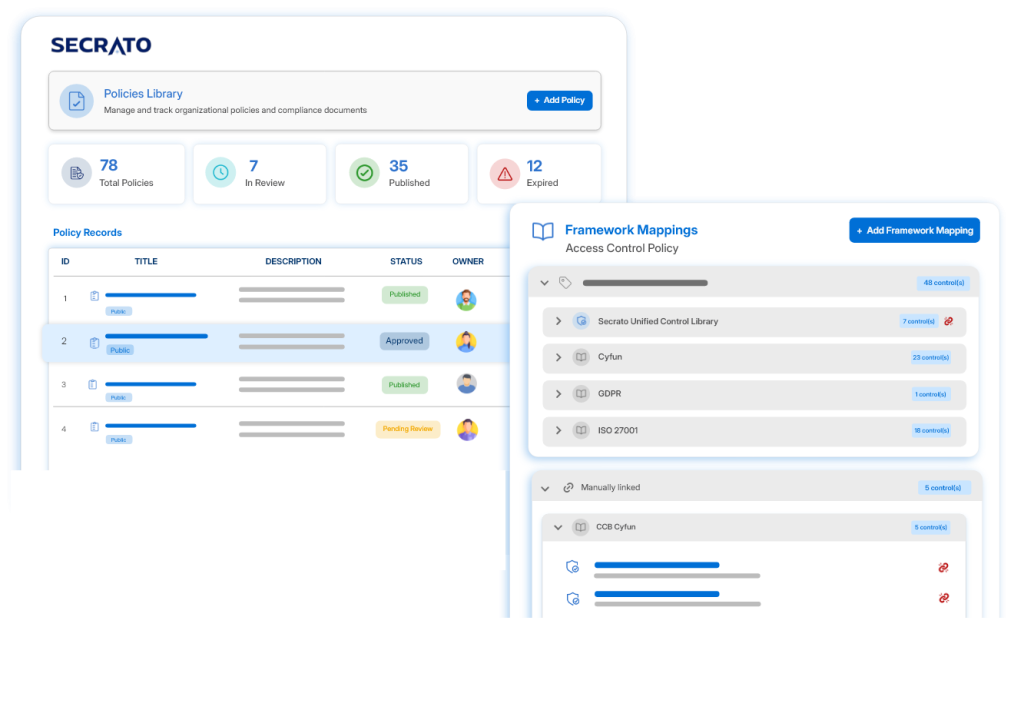
Secrato platform: Policies library
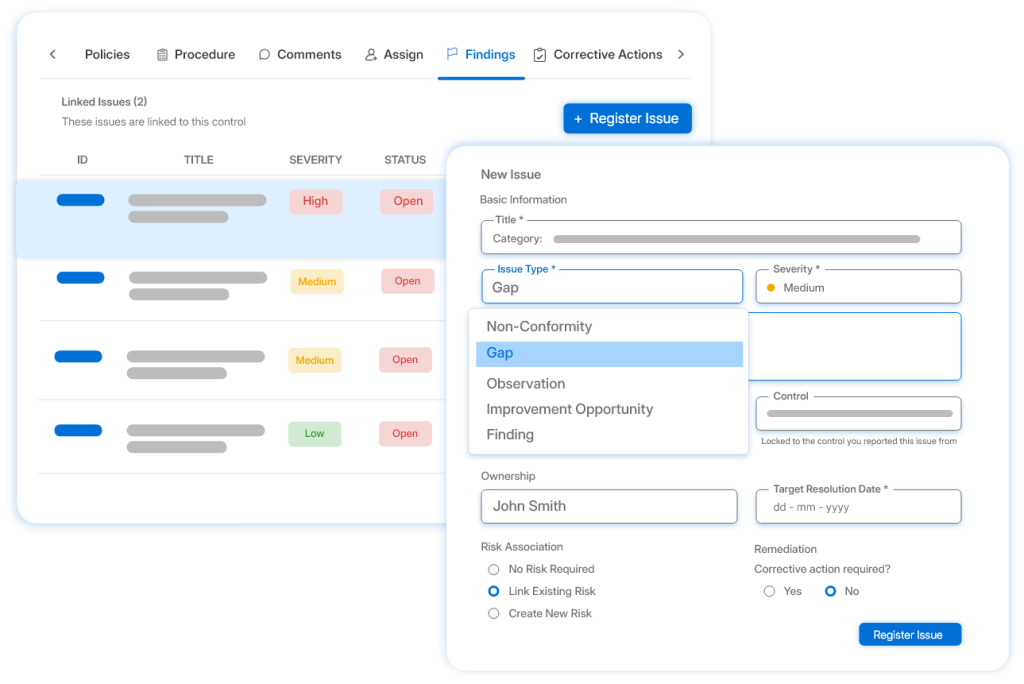
Secrato platform: Findings
LIFECYCLE GOVERNANCE

Keep procedures and records under control

Maintain SOPs, specifications and supporting policies as owned, versioned and reviewed records across the system lifecycle. Connect them to the controls and evidence they support as systems change.

  • Keep procedures owned and reviewable.
  • Maintain version history through change.
  • Link records to the controls they support.
LIFECYCLE GOVERNANCE

Keep procedures and records under control

Maintain SOPs, specifications and supporting policies as owned, versioned and reviewed records across the system lifecycle. Connect them to the controls and evidence they support as systems change.

  • Keep procedures owned and reviewable.
  • Maintain version history through change.
  • Link records to the controls they support.
Secrato platform: Findings
INSPECTION READINESS

Be ready when the inspector asks

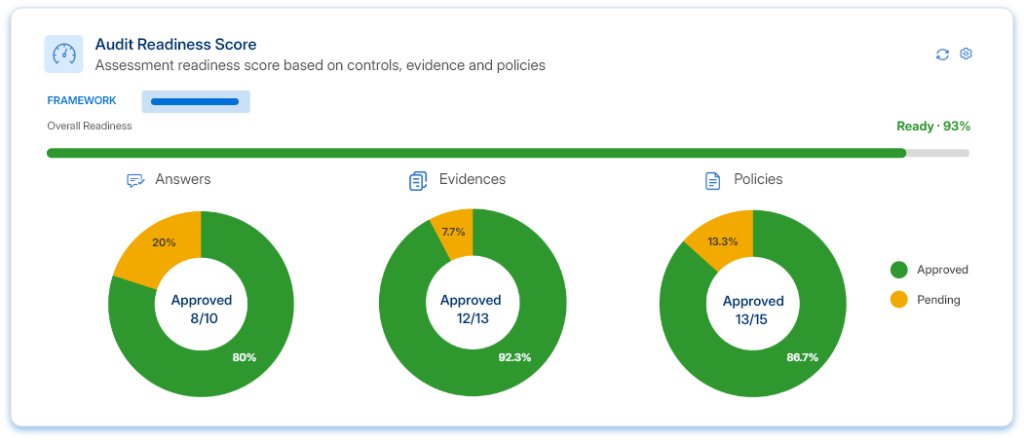
Maintain a current view of control status, evidence and findings across your GxP systems. Keep records organised for internal audit, supplier assessment and regulatory inspection.

  • Track readiness per requirement.
  • Keep findings and corrective actions together.
  • Prepare structured evidence for reviewers.
Secrato platform: Audit readiness score
THE REST OF THE PLATFORM

More ways Secrato supports GAMP 5

Beyond the core outcomes above, these capabilities support the wider GAMP 5 programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

See where GAMP 5 controls overlap with ISO/IEC 27001, ISO 9001 and other frameworks your organisation manages.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

Many controls behind a GAMP 5 approach, such as access management, change control and supplier oversight, also support other frameworks. The Unified Control Library maps those shared controls across the relevant requirements so teams can reuse work without treating the frameworks as equivalent.

FAQs for GAMP 5 compliance software

What is GAMP 5?

GAMP 5 is ISPE’s good-practice guide for a risk-based approach to compliant GxP computerised systems. The second edition, published in July 2022, keeps the original framework and updates it for service providers, iterative development methods, greater use of tools and automation, and critical thinking by experienced subject matter experts. GAMP 5 is guidance rather than a regulation, but it is widely used to meet regulatory expectations for computerised systems.

GAMP 5 is used by pharmaceutical, biotech and medical device companies and other organisations in regulated life-science environments, as well as the suppliers and service providers that deliver their computerised systems. It applies wherever a computerised system can affect patient safety, product quality or data integrity.

Secrato supports the governance and evidence work around GAMP 5 by connecting requirements, risks, controls, procedures and evidence for your GxP systems, giving teams a clearer view of readiness and outstanding gaps. Secrato does not validate systems on your behalf; validation decisions and their documentation remain your organisation’s responsibility.

Keep computerised systems inspection-ready

Systems, suppliers and procedures keep changing long after go-live. See how Secrato can keep the risks, controls and evidence behind your GxP systems connected, so your position holds between inspections.

Secrato
