
J-SOX

J-SOX compliance, internal control you can evidence every year

J-SOX requires management of companies listed in Japan to assess and report on internal control over financial reporting. Secrato keeps the processes, controls, tests and evidence connected to the requirements they answer, including at the subsidiaries in scope.

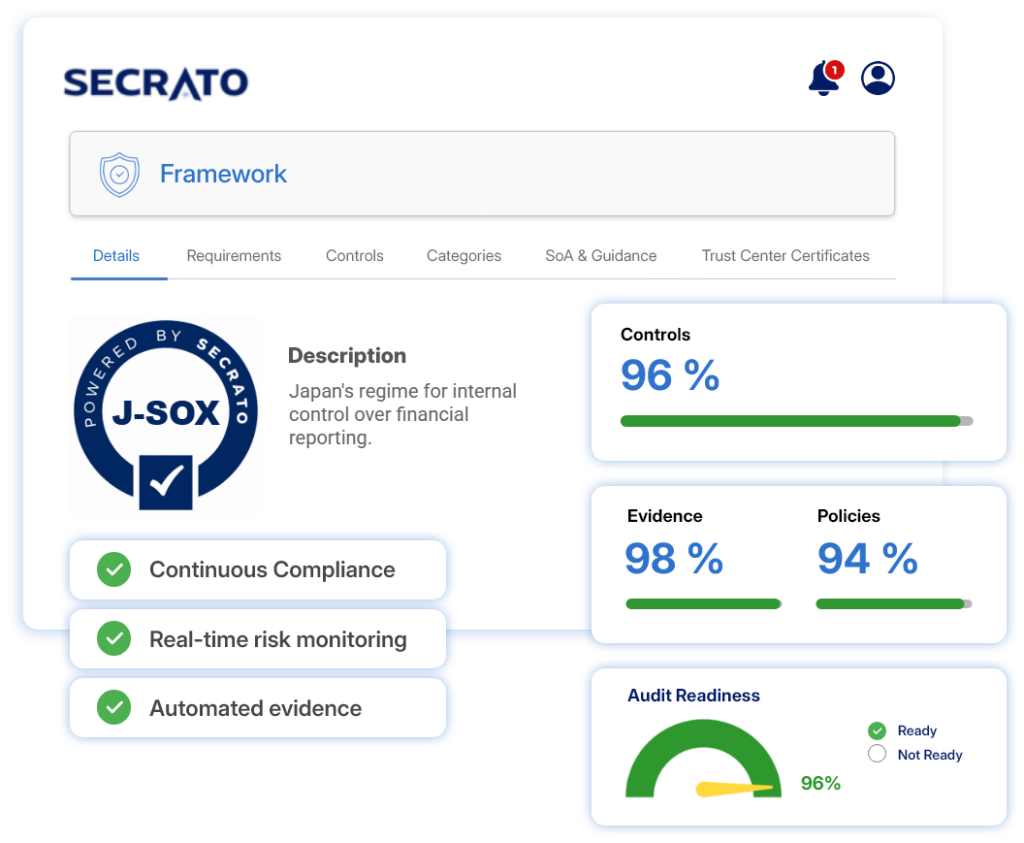
J-SOX framework banner
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
CONTROL DOCUMENTATION

Keep processes and controls documented

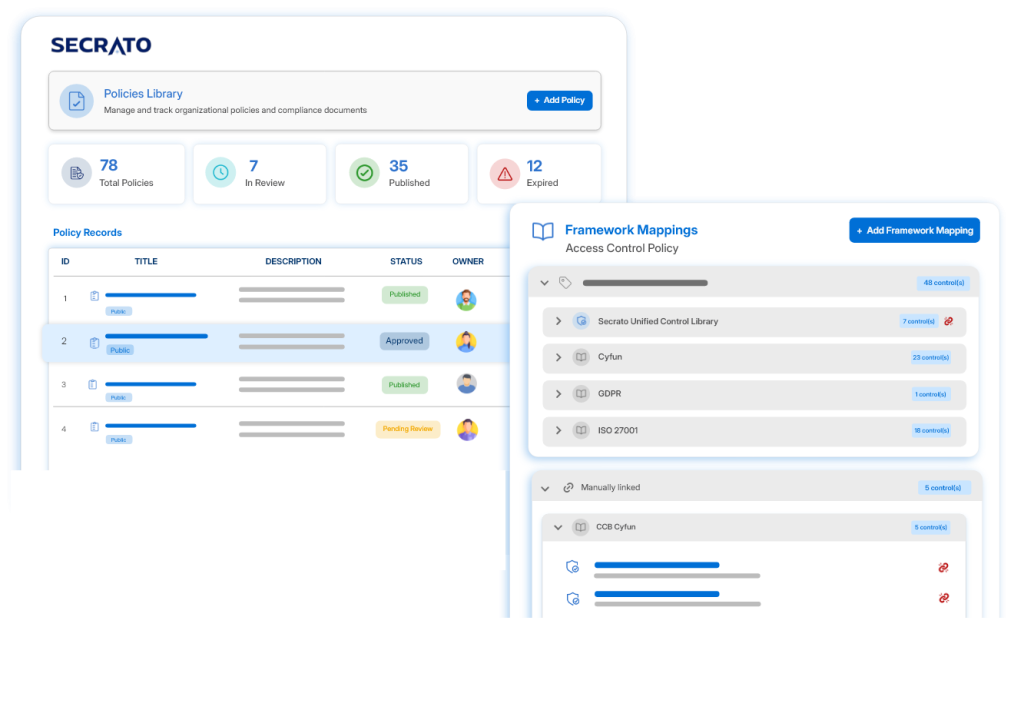
Maintain business processes, key controls and their owners as governed records. Connect each control to the risks it addresses and the evidence that shows it operates.

  • Document processes and key controls.
  • Assign owners across entities.
  • Link evidence to each control.
Secrato platform: Policies library
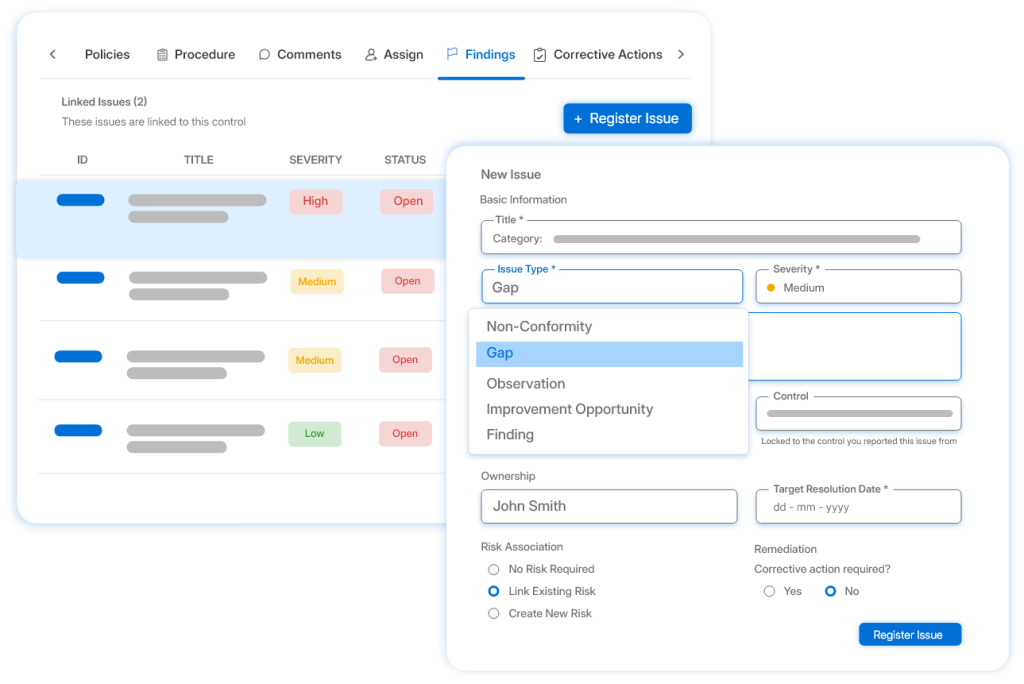
Secrato platform: Findings
IT CONTROLS

Connect IT controls to reporting risk

Keep IT general controls and application controls tied to the financial reporting risks they address. Track access, change and operations controls with evidence that is ready for testing.

  • Map IT general controls to the systems in scope.
  • Link controls to reporting risks.
  • Keep test evidence organised.
IT CONTROLS

Connect IT controls to reporting risk

Keep IT general controls and application controls tied to the financial reporting risks they address. Track access, change and operations controls with evidence that is ready for testing.

  • Map IT general controls to the systems in scope.
  • Link controls to reporting risks.
  • Keep test evidence organised.
Secrato platform: Findings
ASSESSMENT READINESS

Support management's assessment

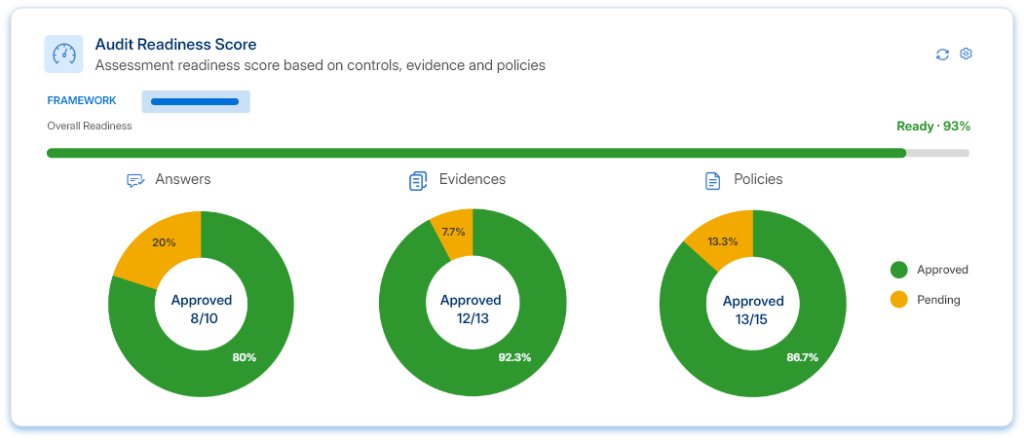
Maintain a current view of control status, deficiencies and remediation across the group. Keep assessments and evidence organised for management’s assessment and the external auditor’s review.

  • Track deficiencies and remediation.
  • See status across subsidiaries.
  • Prepare structured evidence for auditors.
Secrato platform: Audit readiness score
THE REST OF THE PLATFORM

More ways Secrato supports J-SOX

Beyond the core outcomes above, these capabilities support the wider J-SOX programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

See where J-SOX IT controls overlap with ISO/IEC 27001, SOC 2 and other frameworks your organisation manages.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

Many IT general controls used for J-SOX, such as access management and change control, also support other frameworks. The Unified Control Library maps those shared controls across the relevant requirements so teams can reuse work without treating the frameworks as equivalent.

FAQs for J-SOX compliance software

What is J-SOX?

J-SOX is the common name for Japan’s regime for internal control over financial reporting under the Financial Instruments and Exchange Act. Management of a listed company assesses the effectiveness of internal control and files an internal control report, which an external auditor audits. The standards were revised in 2023, with changes to scoping, IT controls and governance that apply to fiscal years beginning on or after 1 April 2024.

It can. J-SOX is assessed on a consolidated basis, so subsidiaries outside Japan of a company listed in Japan can fall within the scope of management’s assessment when they are material to the group’s financial reporting. The parent company decides the scope, usually based on the significance of each location and business process.

Secrato supports J-SOX work by connecting processes, risks, controls and evidence in one place, giving teams a current view of control status and deficiencies across entities. Secrato does not perform management’s assessment or the external audit; those remain with your organisation and its auditor.

Keep internal control ready for year-end

Processes, systems and people change throughout the year. See how Secrato can keep your controls, tests and evidence connected, so management’s assessment does not start from scratch.

Secrato
