
ISO/IEC 27701

ISO/IEC 27701 compliance, privacy management you can evidence

ISO/IEC 27701:2025 sets out a privacy information management system in its own right. Secrato keeps privacy risks, controls, policies and evidence connected to the requirements they answer, so you can show how personal data is governed rather than describe it.

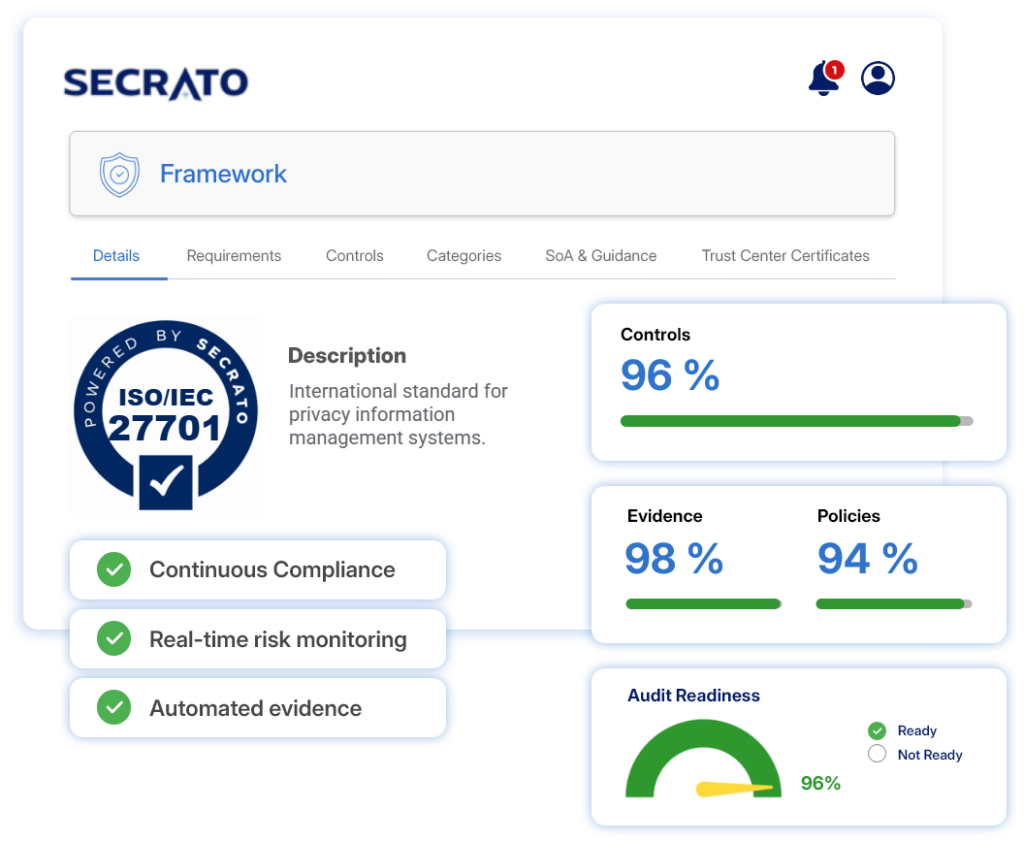
ISO/IEC 27701 framework banner
GDPR by design
GDPR BY DESIGN
Hosted in Belgium
HOSTED IN BELGIUM
EU data sovereignty
EU DATA SOVEREIGNTY
Enterprise-grade security
ENTERPRISE-GRADE SECURITY
PRIVACY CONTROLS

Connect privacy requirements to controls

Map the requirements of ISO/IEC 27701 to the controls that address them, whether you act as a PII controller, a PII processor or both. Keep ownership, status and supporting evidence visible for every control.

  • Track controller and processor controls separately.
  • Assign owners and keep status current.
  • Link evidence to the controls it supports.
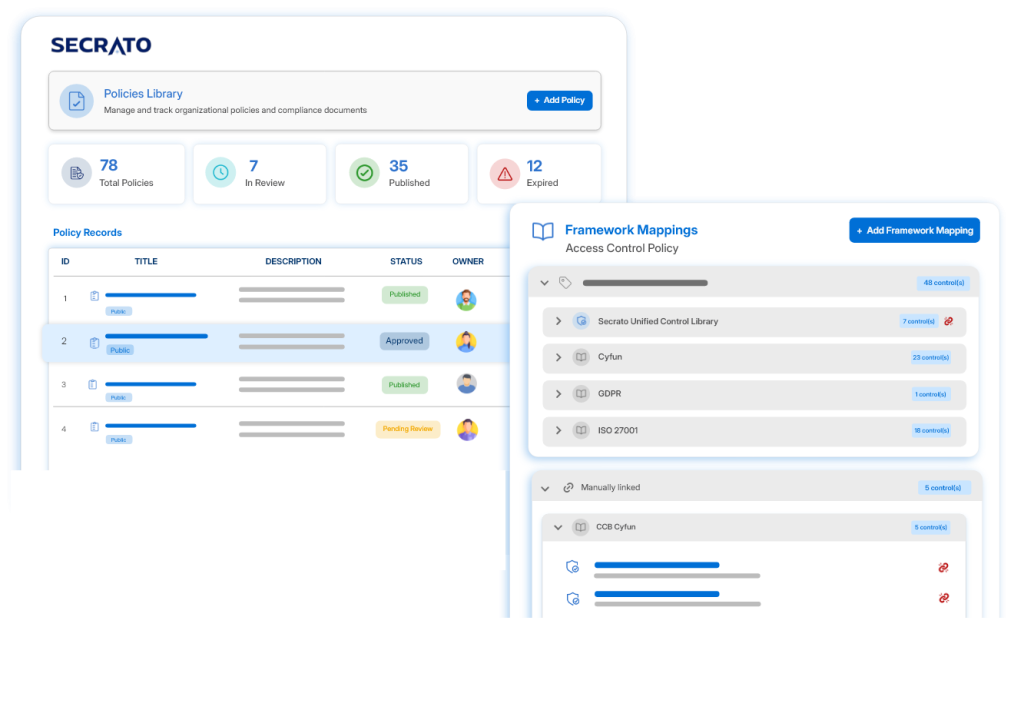
Secrato platform: Policies library
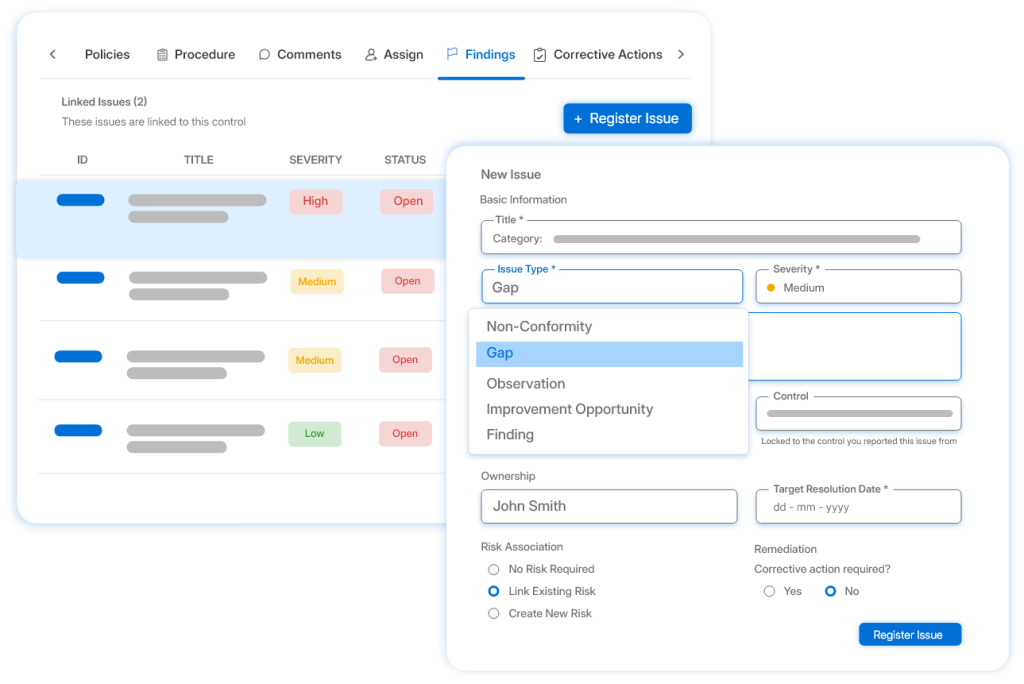
Secrato platform: Findings
PRIVACY RISK

Keep privacy risks tied to treatment

Record risks to personal data and to the people it concerns, and connect them to the controls and decisions used to treat them. Keep treatment status and residual exposure in view as processing changes.

  • Assess privacy risks alongside security risks.
  • Link each risk to its treatment and controls.
  • See residual exposure at a glance.
PRIVACY RISK

Keep privacy risks tied to treatment

Record risks to personal data and to the people it concerns, and connect them to the controls and decisions used to treat them. Keep treatment status and residual exposure in view as processing changes.

  • Assess privacy risks alongside security risks.
  • Link each risk to its treatment and controls.
  • See residual exposure at a glance.
Secrato platform: Findings
AUDIT READINESS

Show the PIMS in operation

Keep assessments, evidence and findings organised for internal audit, management review and certification. Give auditors a clear route from each requirement to the records behind it.

  • Track readiness per requirement.
  • Keep findings and corrective actions together.
  • Prepare structured evidence for auditors.
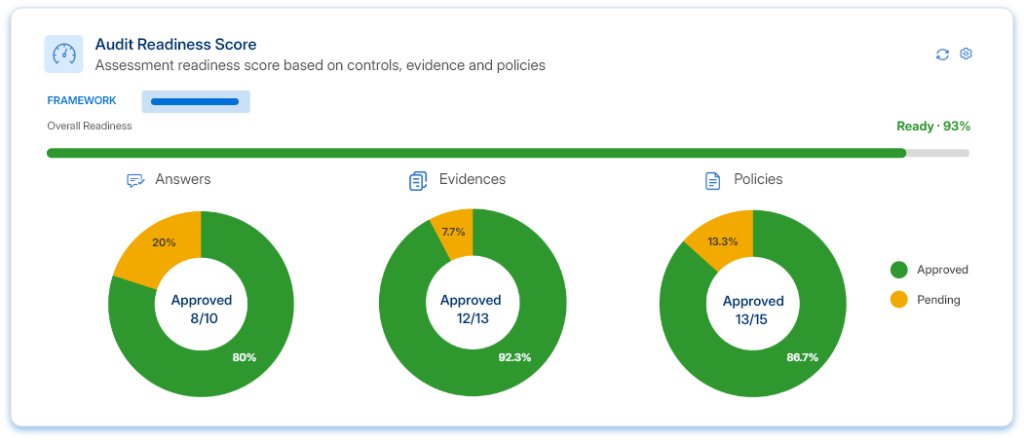
Secrato platform: Audit readiness score
THE REST OF THE PLATFORM

More ways Secrato supports ISO/IEC 27701

Beyond the core outcomes above, these capabilities support the wider ISO/IEC 27701 programme.

Manage requirements, controls, evidence, policies and status together, giving teams a current view of where implementation stands.

See where ISO/IEC 27701 controls overlap with GDPR, ISO/IEC 27001 and other frameworks your organisation manages.

Scope, score and assign assessment work, with responses linked to the evidence and records behind them.

Organise evidence, review control readiness and manage findings, with structured reviewer access where appropriate.

Connect internal and external systems through APIs and integrations to support evidence collection and reduce manual chasing.

Share relevant security and compliance information with stakeholders through controlled public or gated access.

FRAMEWORK COVERAGE

One control. Multiple frameworks.

ISO/IEC 27701 shares much of its control work with ISO/IEC 27001 and GDPR. The Unified Control Library maps those shared controls across the relevant requirements so teams can reuse work without treating the frameworks as equivalent.

FAQs for ISO/IEC 27701 compliance software

What is ISO/IEC 27701?

ISO/IEC 27701 specifies requirements for a privacy information management system (PIMS) for organisations that act as PII controllers, PII processors or both. The current edition, ISO/IEC 27701:2025, was published on 14 October 2025 and replaces the 2019 version. It is now a standalone management system standard, so it can be certified without an ISO/IEC 27001 certificate. Accreditation bodies are still setting the transition period for certificates issued against the 2019 version.

ISO/IEC 27701 is a voluntary international standard, while GDPR is binding EU law. The standard gives a structured way to manage privacy and can support the accountability that GDPR expects, but certification does not by itself prove GDPR compliance. Many organisations run both, with ISO/IEC 27701 as the management system and their GDPR obligations mapped to its controls.

Secrato supports ISO/IEC 27701:2025 by connecting privacy requirements with the controls, risks, policies and evidence behind them. Teams get a current view of PIMS readiness and outstanding gaps, and can reuse shared control work across ISO/IEC 27001, GDPR and other frameworks. Secrato does not certify organisations; certification is carried out by an accredited certification body.

Keep privacy governance ready for review

Privacy obligations change with every new processing activity, supplier and system. See how Secrato can keep your privacy controls, risks and evidence connected, so your PIMS stays current between audits.

Secrato
